In some cases, the new IP address change is not displayed on the SSO sessions tab on FortiAuthenticator.
This behavior can be seen in the following output:
On FSSO debug displays:
- 06/18/2026 15:02:21 [EE2E36C0] Logon Cache [INFO]: Updated logon, workstation:LAP-MNT-CO1-001 ip:changed from 172.20.10.9 to 172.20.20.51 user:FORTINET/testfsso

- 06/18/2026 15:03:18 [EE2F46C0] DC/TS Agent [INFO]: LOGON 2026-06-18-15:03:18/2026-06-18-15:03:18 DC Agent (null):LAP-MNT-CO1-001/172.20.20.51 FORTINET/testfsso

- 06/18/2026 15:03:18 [EE2F46C0] Group Cache [INFO]: Loaded groups for user FORTINET/testfsso

On DC agent logs it identifies correctly new IP change:

- 06/18/2026 15:02:21.510: processing Logon (level=1, logonid=0-0) FORTINET estfsso (Test FSSO) from LAP-MNT-CO1-001

- Domain:CZFS DNS suffix added:FORTINET.LOCAL.

- process_logonevent 940, queue size:0

- 06/18/2026 15:02:21.525: finish processing.

- ProcessLogonRequest_thread 496, queue size:1, pRec:000000E3CA9ED290

- ProcessRequest 621 Enter

- workstation IP:172.20.20.51

After, switch network in order to change IP to 172.20.10.9, but previous IP address it kept despite already being on the new network.

06/18/2026 16:10:44 [EE2D26C0] Logon Cache [INFO]: Updated logon, workstation:LAP-MNT-CO1-001 ip:172.20.20.51 user:FORTINET/testfsso

- 06/18/2026 16:15:58 [EE5A76C0] Group Cache [INFO]: pending group lookup for user FORTINET/testfsso

- 06/18/2026 16:15:58 [EE1CB6C0] Group Cache [INFO]: Loaded groups for user FORTINET/testfsso

- 06/18/2026 16:15:58 [EE1CB6C0] Group Cache [INFO]: try to remove FORTINET/testfsso((null))

- 06/18/2026 16:15:58 [EE1CB6C0] Group Cache [INFO]: added (replaced existing one): FORTINET/testfsso
DC agent log:
- 06/18/2026 16:10:44.043: processing Logon (level=1, logonid=0-0) FORTINET estfsso (Test FSSO) from LAP-MNT-CO1-001

- Domain:CZFS DNS suffix added:FORTINET.LOCAL.

- process_logonevent 940, queue size:0

- 06/18/2026 16:10:44.059: finish processing.

- ProcessLogonRequest_thread 496, queue size:1, pRec:000000E3CA9EAD60

- ProcessRequest 621 Enter

- workstation IP:172.20.20.51

- ProcessRequest 821 Leave

- DcAgentSendLogonEvent 190 Enter

- DcAgentSendLogonEvent 196 len:42

- DcAgentSendLogonEvent 208 index:0

- DcAgentSendLogonEvent 355 Leave

- Msv1_0SubAuthenticationFilter is called
Suggested Solution:
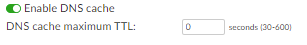
The suggestion is to reduce the maximum TTL of the FortiAuthenticator's DNS record cache to a lower number, such as 2 or 5 minutes, to ensure that the original IP address of the workstation does not stick around too long, and it is also recommended to force the workstation to update its associated DNS records in Active Directory by running the command 'ipconfig /registerdns' in an elevated command prompt.
NOTE:
Keep in mind that fifteen is the default TTL (in Active Directory) for the DNS records created during the workstation DHCP process.
While it can be reduced, making a significant change can likely create other performance bottlenecks. |