



Technical Tip: SAML Authentication with FortiAuthenticator as IdP, FortiAnalyzer as SP
Description
This article explains how to configure FortiAuthenticator as IdP and FortiAnalyzer as SP.
Scope
FortiAuthenticator as IdP and FortiAnalyzer as SP.
Solution
FortiAuthenticator settings:
To configure SAML Portal settings, go to Authentication -> SAML IdP.
Under the general settings, configure the following options:
- Enter the FQDN of the configured device from the system dashboard.
- Select the Realm & Filter the configured user group.
- Select IdP certificate.
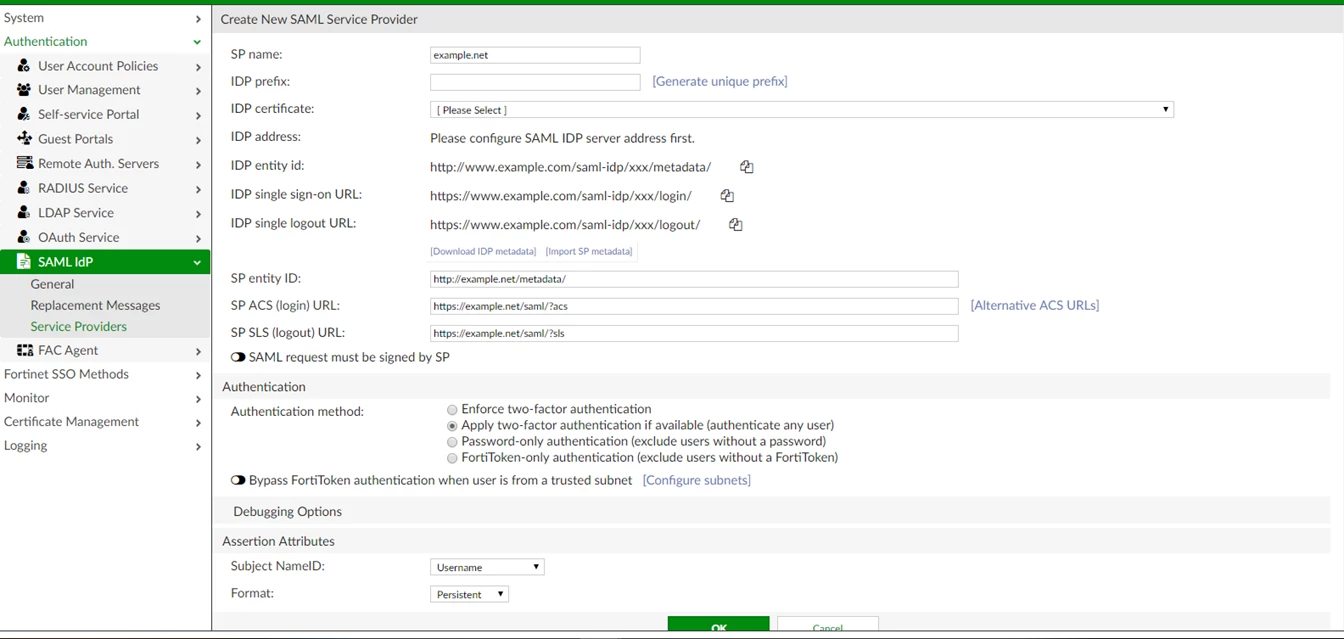
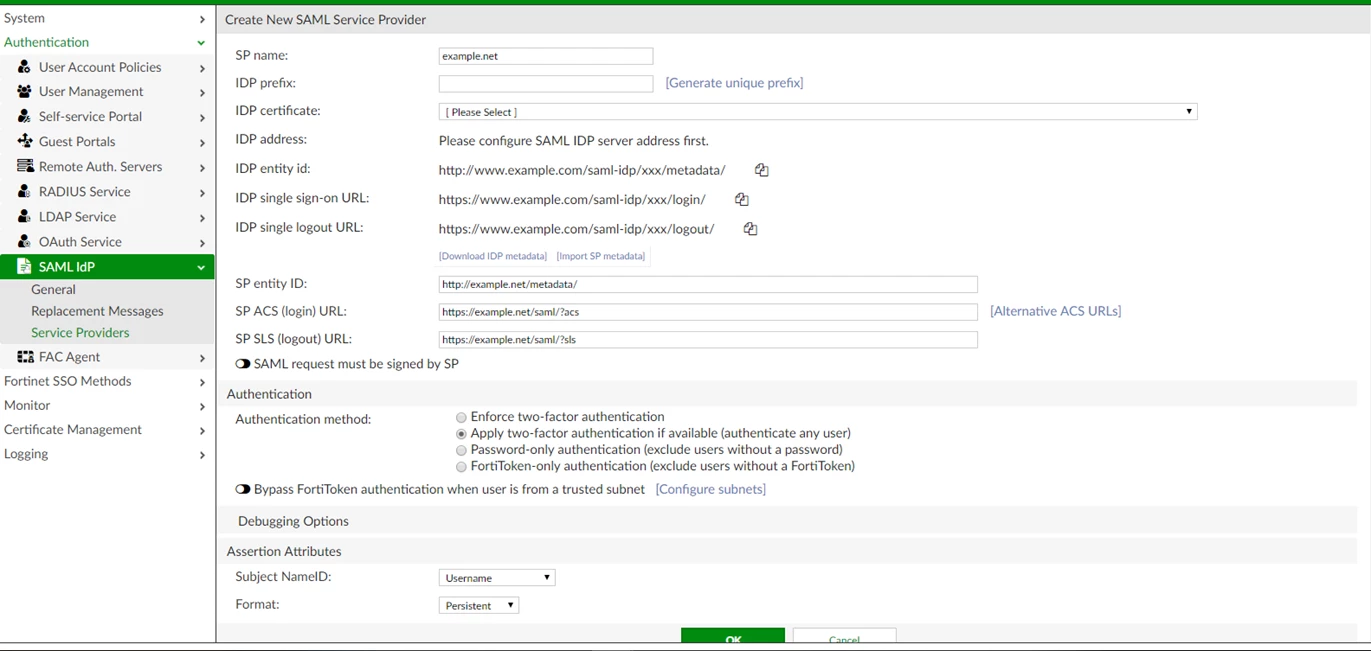
Under the Service Providers:
- Configure the SP parameter & Attributes.
FortiAnalyzer settings:
To configure the SP, go to Admin -> SAML SSO -> SP.
The admin user must be created on FortiAnalyzer.
Testing:
- Go to FortiAnalyzer and log in through SSO.
- The login will redirect to the FortiAuthenticator.
- After entering the correct credentials, it will redirect back to the FortiAnalyzer.
Note:
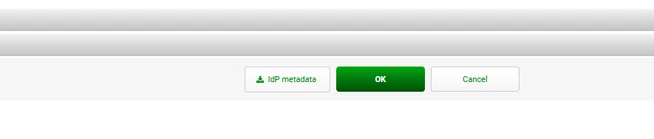
In the newer version of FortiAuthenticator, IdP metadata can be downloaded at the bottom of the SP configuration page:
Useful links:
Fortinet documentation:
https://help.fortinet.com/fauth/5-2/Content/Admin%20Guides/5_2%20Admin%20Guide/400/411_SAML_IdP.htm
https://docs.fortinet.com/document/fortiauthenticator/6.0.0/administration-guide/360613/whats-new-in-fortiauthenticator-6-0-0


