Technical Tip: Local user authentication from x.x.x.x (MS-CHAP) with cloud token failed: invalid user parameter
| Description | This article describes a use case where users are unable to log in with an IPsec dial-up VPN with two-factor authentication using FortiToken Cloud. |
| Scope | FortiGate and FortiAuthenticator Cloud. |
| Solution | In FortiAuthenticator raw logs, the 1st attempt happens with MS-CHAP, 2nd attempt happens with CHAP, and 3rd attempt happens with PAP. In this use case, the authentication is successful with PAP.
date=2025-11-26 time=10:50:22+0000 oid=3060 logid=20002 cat="Event" subcat="Authentication" level="information" nas="10.10.19.17" action="Authentication" status="Success" msg="Local user authentication from x.x.x.x with cloud token successful" user="joe"
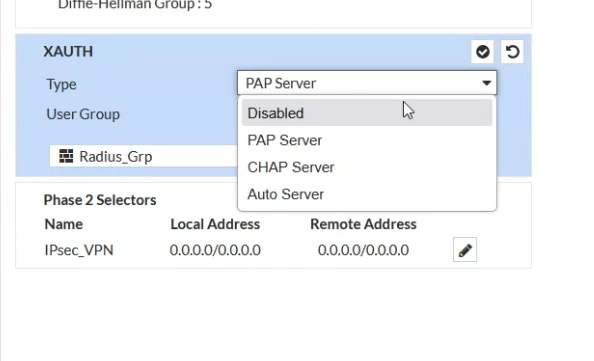
In FortiGate under an IPsec tunnel, the default 'auto server' setting is used. When Windows-AD authentication is enabled, the connection between FortiAuthenticator and FortiGate uses MS-CHAP. In the case of FortiToken Cloud, FortiGate does not send a cleartext token code for the non-PAP case.
Solution: Modify to PAP server under XAUTH settings in the IPsec tunnel through RADsec.
|