



Technical Tip: LDAPS with FortiAuthenticator
Description
This article describes how to configure LDAPS with FortiAuthenticator, assuming that the domain controller has a valid computer certificate in place.
Scope
FortiAuthenticator.
Solution
In this example, the Microsoft Windows Active Directory has been used as the Certificate Authority,
These tests were performed with Windows Server 2019.
Open Run and write mmc.exe.
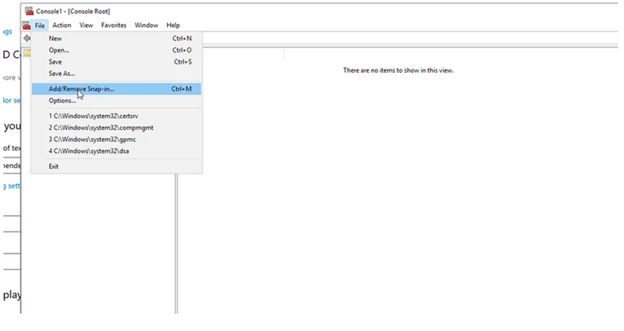
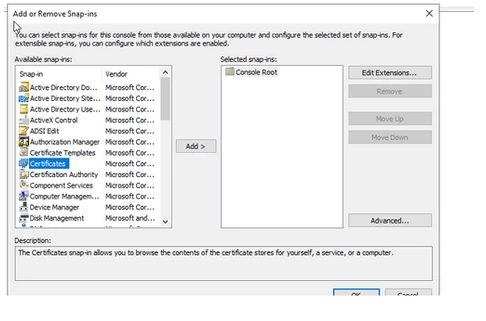
Go to File and select Add/Remove Snap-in, choose Certificates, and select 'Add'.
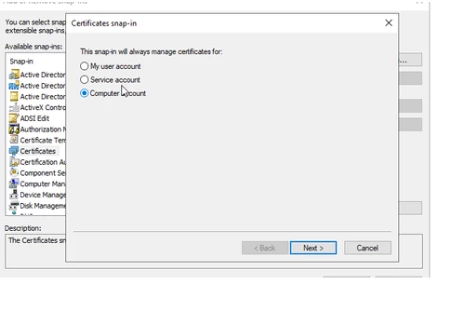
Select the option 'Computer Account'.
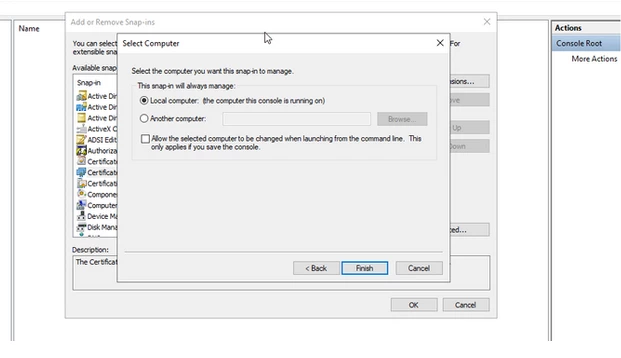
Select the option 'Local Computer' and choose 'Finish'.
Select 'Certificates', go to Personal- Certificates, and select the certificate that has the same name as the domain controller (computer certificate).
'Right-click', select All tasks, and choose 'Export'.
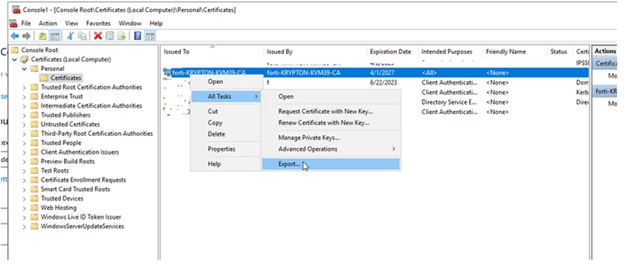
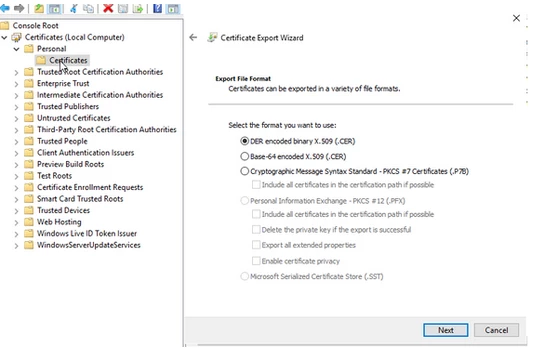
Select the 'No' option, do not export the private key, and the DER file format.
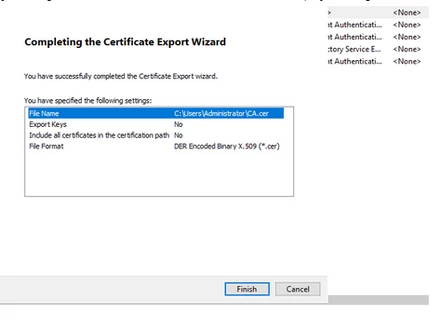
Specify the name and select 'Next', specify a filename, and choose 'Finish'.
Alternatively, follow the article to extract the Root CA certificate:
Technical Tip: How to export root CA from Certificate Authority Server and import to FortiGate
Note: If the domain controller does not have a valid computer certificate in place, the following error may appear in the FortiAuthenticator GUI when browsing to the directory with LDAPS enabled:
Query failed: ldap_simple_bind_s failed: Can't contact LDAP server error:0A000086:SSL routines::certificate verify failed (unhandled critical extension)
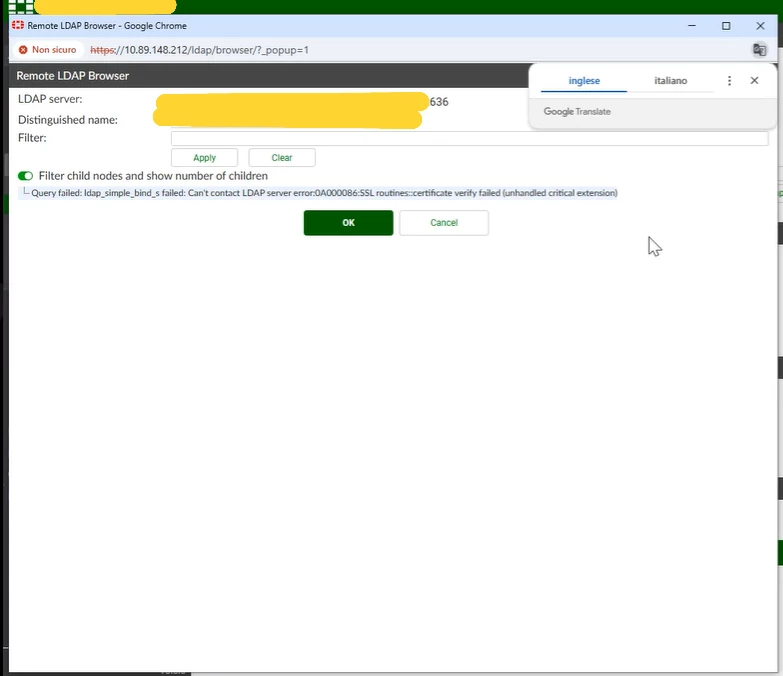
Import this CA certificate on FortiAuthenticator as a Trusted CA.
Go to Certificate Management -> Certificate Authorities -> Trusted CA and select Import.
Specify an ID for the certificate and select Upload a file to import the certificate previously exported.
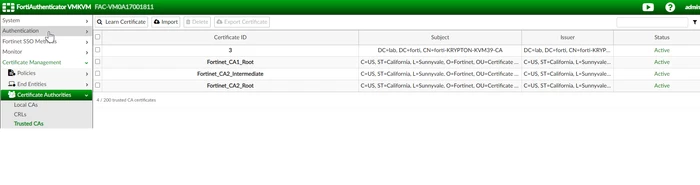
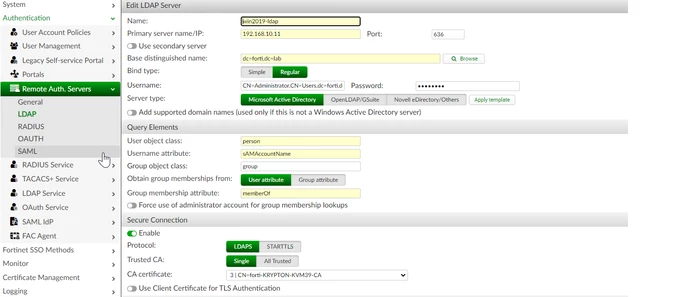
Go to Authentication -> Remote Auth.Servers -> LDAP, enable the Secure Connection option, and select the correct certificate.
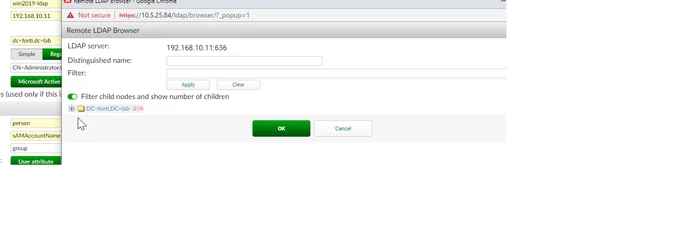
Try to browse to the directory with LDAPS enabled, which should work fine now.
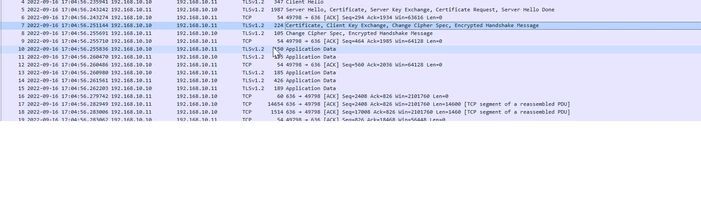
Also, run a packet capture. No readable data should be seen, with only TLS encryption.
Note that from version 6.6.2, certificates with SHA1 are no longer supported; if this is added, then the LDAP bind will not work. On v6.6.2, the certificate created needs to be on SHA2. Refer to the following document: SHA-1 cryptographic operations are no longer supported.

