



Technical Tip: How to use specific FortiAuthenticator RADIUS policies for different IPsec VPN tunnels in FortiGate
Description
This article describes how to use specific FortiAuthenticator RADIUS policies for different IPsec VPN tunnels from the same FortiGate.
Scope
FortiAuthenticator, FortiGate.
Solution
To allow different IPsec VPN tunnels to authenticate against separate RADIUS policies on FortiAuthenticator, the FortiGate must attach a unique identifier to each authentication request so FortiAuthenticator can filter on this identifier.
FortiGate only has one easily modified RADIUS attribute suitable for this purpose, in particular, the NAS-IP-Address. FortiGate can set different NAS-IP-Address attributes for different RADIUS server entries, and each IPSec tunnel can be configured to reference a specific RADIUS server (and thus a unique NAS-IP-Address attribute).
On the FortiAuthenticator:
Two user groups are configured with different RADIUS attributes.
Two RADIUS policies are defined, each matching specific attribute criteria (including NAS-IP-Address).
This allows FortiAuthenticator to distinguish requests and apply the correct policy and group assignment per tunnel.
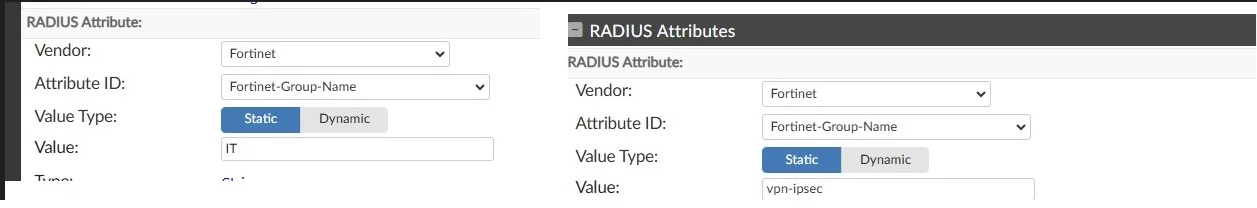
Figure 1: RADIUS attributes for different user groups.
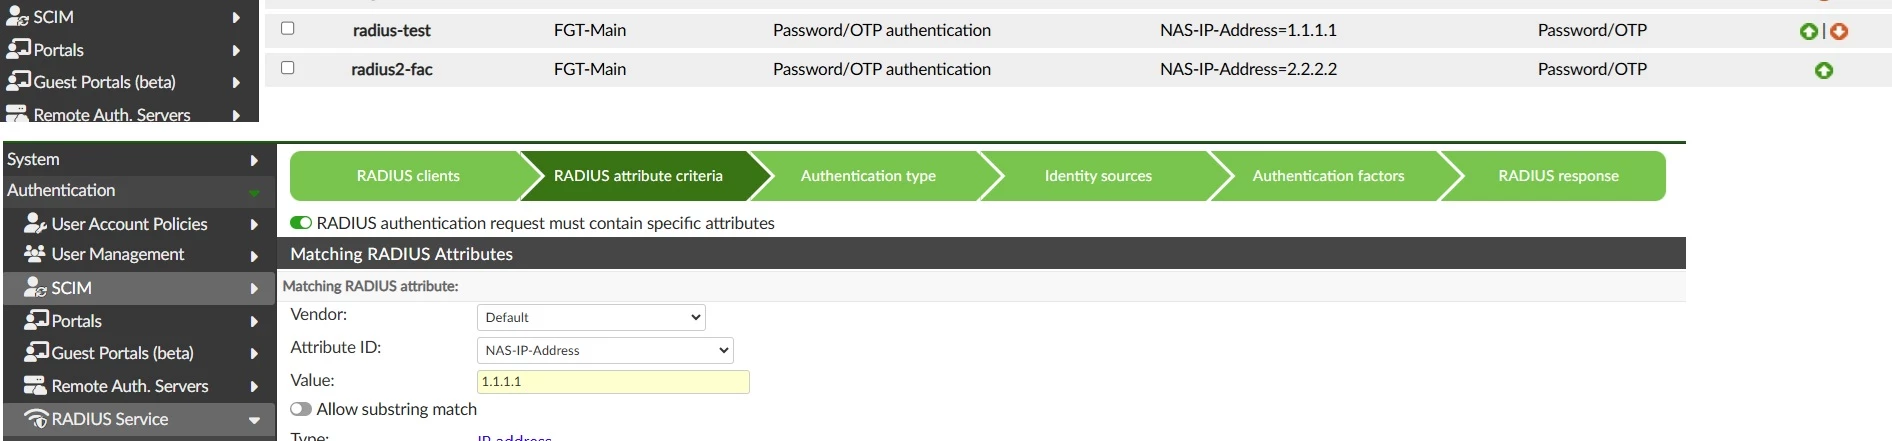
Figure 2: RADIUS attribute criteria.
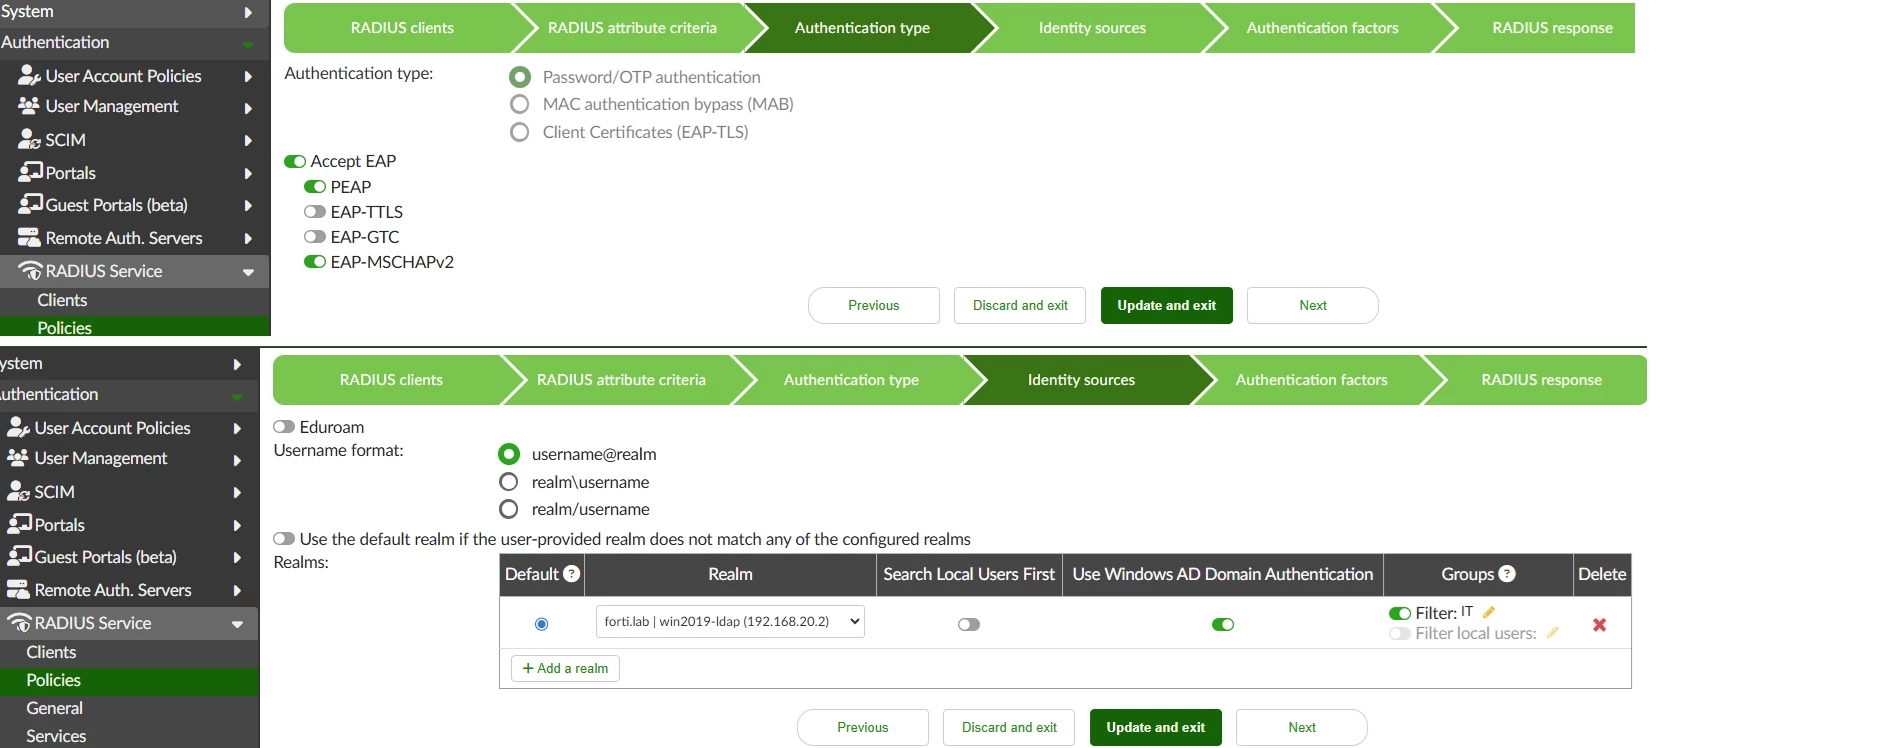
Figure 3: RADIUS policy configuration.
The second RADIUS policy has the same configuration as the first one, with the only difference being the NAS-IP-Address value. Additionally, a different user group is defined under the Identity Sources section.
On the FortiGate, two user groups are configured to match specific RADIUS attributes returned by the FortiAuthenticator. Each group is associated with a separate IPsec VPN tunnel and referenced in its respective firewall policy.
Furthermore, two RADIUS server entries are configured on the FortiGate, each using a distinct NAS-IP-Address. These NAS-IP values correspond to the matching RADIUS client configurations on the FortiAuthenticator and allow the RADIUS policies to differentiate authentication requests per tunnel.
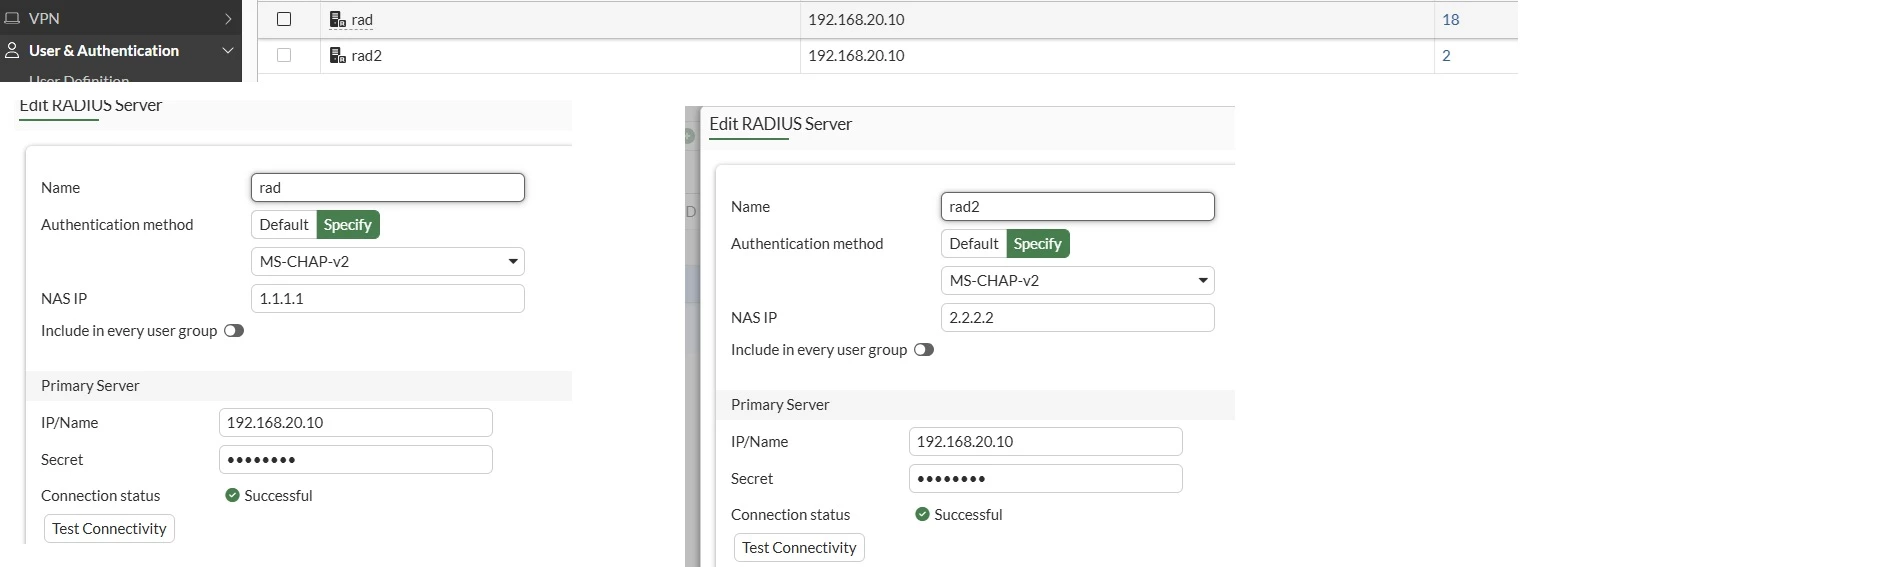
Figure 4: RADIUS server configured on FortiGate.
The first user group created on the FortiGate is named 'rad_group' in this example.
config user group
    edit "rad_grp"
        set member "rad"
            config match
                edit 1
                    set server-name "rad"
                    set group-name "IT"
                next
            end
    next
end
The second user group created on the FortiGate is named 'rad_group1'.
config user group
    edit "rad_group1"
        set member "rad2"
            config match
                edit 1
                    set server-name "rad2"
                    set group-name "vpn-ipsec"
                next
            end
        next
    end
The first IPsec VPN tunnel is configured with its corresponding Phase 1 and Phase 2 interface settings:
'set authusrgrp "rad_grip"' references a specific group via RADIUS and NAS IP attribute.
'set peerid "cert0"' has a different peer ID specified for each tunnel.
config vpn ipsec phase1-interface
    edit "Dialup-0"
        set type dynamic
        [...]
        set peertype one
        [...]
        set authusrgrp "rad_grp"
        [...]
        set peerid "cert0"
        [...]
    next
end
config vpn ipsec phase2-interface
    edit "Dialup-cert_0"
        set phase1name "Dialup-0"
        [...]
    next
end
A dedicated firewall policy is configured on the FortiGate to allow traffic from the first IPsec tunnel interface to the internal network. This policy should not have a user group specified.
An identical configuration is implemented for the second IPsec tunnel. The only variations are the assigned user group, the peer ID defined in Phase 1, and the corresponding firewall policy referencing the second tunnel.
Testing results from the first IPsec tunnel with user 'pirlo', RADIUS debug logs from FortiAuthenticator.
2026-03-02T11:09:48.167849+01:00 FortiAuthenticator radiusd[6060]: (1) Received Access-Request Id 13 from 192.168.20.1:15311 to 192.168.20.10:1812 length 173
2026-03-02T11:09:48.167896+01:00 FortiAuthenticator radiusd[6060]: (1) EAP-Message = 0x02940007031a06
2026-03-02T11:09:48.167902+01:00 FortiAuthenticator radiusd[6060]: (1) User-Name = "pirlo"
[...]
2026-03-02T11:09:48.167918+01:00 FortiAuthenticator radiusd[6060]: (1) Framed-IP-Address = 192.168.20.3
2026-03-02T11:09:48.167923+01:00 FortiAuthenticator radiusd[6060]: (1) NAS-IP-Address = 1.1.1.1
[...]
2026-03-02T11:09:48.168046+01:00 FortiAuthenticator radiusd[6060]: (1) Connect-Info = "vpn-ikev2"
2026-03-02T11:09:48.168054+01:00 FortiAuthenticator radiusd[6060]: (1) Fortinet-Vdom-Name = "root"
[...]
2026-03-02T11:09:48.168976+01:00 FortiAuthenticator radiusd[6060]: (1) facauth: Found vendor 0, attr 4 --> "1.1.1.1"
2026-03-02T11:09:48.168983+01:00 FortiAuthenticator radiusd[6060]: (1) facauth: Found authpolicy 'radius-test' for client '192.168.20.1'
[...]
2026-03-02T11:09:48.169361+01:00 FortiAuthenticator radiusd[6060]: (1) facauth: LDAP user found: pirlo
[...]
2026-03-02T11:09:48.342126+01:00 FortiAuthenticator radiusd[6060]: (3) facauth: EAP authentication success - add configured radius attributes to response
2026-03-02T11:09:48.342824+01:00 FortiAuthenticator radiusd[6060]: (3) facauth: Add Static Radius attribute: attr_id:85 (attr 85, vendor 0) attr_val:'60'
2026-03-02T11:09:48.342832+01:00 FortiAuthenticator radiusd[6060]: (3) facauth: Add Static Radius attribute: attr_id:809762817 (attr 1, vendor 12356) attr_val:'IT'
2026-03-02T11:09:48.342856+01:00 FortiAuthenticator radiusd[6060]: (3) facauth: Updated auth log 'pirlo' for attempt from 192.168.20.1: 802.1x authentication successful
2026-03-02T11:09:48.342909+01:00 FortiAuthenticator radiusd[6060]: (3) Sent Access-Accept Id 15 from 192.168.20.10:1812 to 192.168.20.1:15311 length 181
[...]
2026-03-02T11:09:48.343003+01:00 FortiAuthenticator radiusd[6060]: (3) User-Name = "pirlo"
2026-03-02T11:09:48.343039+01:00 FortiAuthenticator radiusd[6060]: (3) Framed-MTU += 994
2026-03-02T11:09:48.343310+01:00 FortiAuthenticator radiusd[6060]: (3) Acct-Interim-Interval += 60
2026-03-02T11:09:48.343320+01:00 FortiAuthenticator radiusd[6060]: (3) Fortinet-Group-Name += "IT"
Testing results from the second IPsec tunnel with user 'genci', RADIUS debug logs from FortiAuthenticator:
2026-03-02T11:31:03.821024+01:00 FortiAuthenticator radiusd[7409]: (0) Received Access-Request Id 19 from 192.168.20.1:6993 to 192.168.20.10:1812 length 158
2026-03-02T11:31:03.821049+01:00 FortiAuthenticator radiusd[7409]: (0) EAP-Message = 0x0290000a0167656e6369
2026-03-02T11:31:03.821058+01:00 FortiAuthenticator radiusd[7409]: (0) User-Name = "genci"
[...]
2026-03-02T11:31:03.821073+01:00 FortiAuthenticator radiusd[7409]: (0) NAS-IP-Address = 2.2.2.2
[...]
2026-03-02T11:31:03.821217+01:00 FortiAuthenticator radiusd[7409]: (0) Connect-Info = "vpn-ikev2"
2026-03-02T11:31:03.821224+01:00 FortiAuthenticator radiusd[7409]: (0) Fortinet-Vdom-Name = "root"
[...]
2026-03-02T11:31:03.823260+01:00 FortiAuthenticator radiusd[7409]: (0) facauth: Did not find vendor 0, attr 4 --> "1.1.1.1"
2026-03-02T11:31:03.823298+01:00 FortiAuthenticator radiusd[7409]: (0) facauth: Found vendor 0, attr 4 --> "2.2.2.2"
2026-03-02T11:31:03.823316+01:00 FortiAuthenticator radiusd[7409]: (0) facauth: Found authpolicy 'radius2-fac' for client '192.168.20.1'
[...]
2026-03-02T11:31:03.823925+01:00 FortiAuthenticator radiusd[7409]: (0) facauth: LDAP user found: genci
[...]
2026-03-02T11:31:03.942593+01:00 FortiAuthenticator radiusd[7409]: (3) facauth: EAP authentication success - add configured radius attributes to response
2026-03-02T11:31:03.943319+01:00 FortiAuthenticator radiusd[7409]: (3) facauth: Add Static Radius attribute: attr_id:809762817 (attr 1, vendor 12356) attr_val:'vpn-ipsec'
2026-03-02T11:31:03.943350+01:00 FortiAuthenticator radiusd[7409]: (3) facauth: Updated auth log 'genci' for attempt from 192.168.20.1: 802.1x authentication successful
2026-03-02T11:31:03.943400+01:00 FortiAuthenticator radiusd[7409]: (3) Sent Access-Accept Id 22 from 192.168.20.10:1812 to 192.168.20.1:6993 length 182
[...]
2026-03-02T11:31:03.943481+01:00 FortiAuthenticator radiusd[7409]: (3) User-Name = "genci"
2026-03-02T11:31:03.943487+01:00 FortiAuthenticator radiusd[7409]: (3) Framed-MTU += 994
2026-03-02T11:31:03.943491+01:00 FortiAuthenticator radiusd[7409]: (3) Fortinet-Group-Name += "vpn-ipsec"
Debug logs that can be collected on the FortiGate side:
Only use 'diagnose debug application eap_proxy -1' with IKEv2.
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug application fnbamd -1
diagnose debug application eap_proxy -1
diagnose vpn ike log filter rem-addr4 <RemoteClientIp>
diagnose debug application ike -1
diagnose debug enable
Related articles:

