



Technical Tip: How to sign a CSR on FortiAuthenticator
Description
This article describes how FortiAuthenticator can be used to sign a Certificate Sign Request (CSR) generated by other device like a FortiGate.
Scope
FortiAuthenticator, FortiGate.
Solution
1. Generating CSR file by FortiGate.
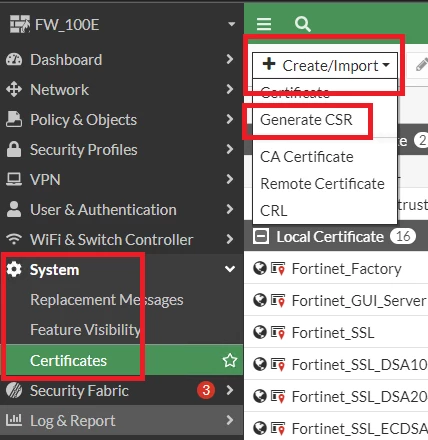
- Go to System -> Certificate, select Create/Import -> Generate CSR.
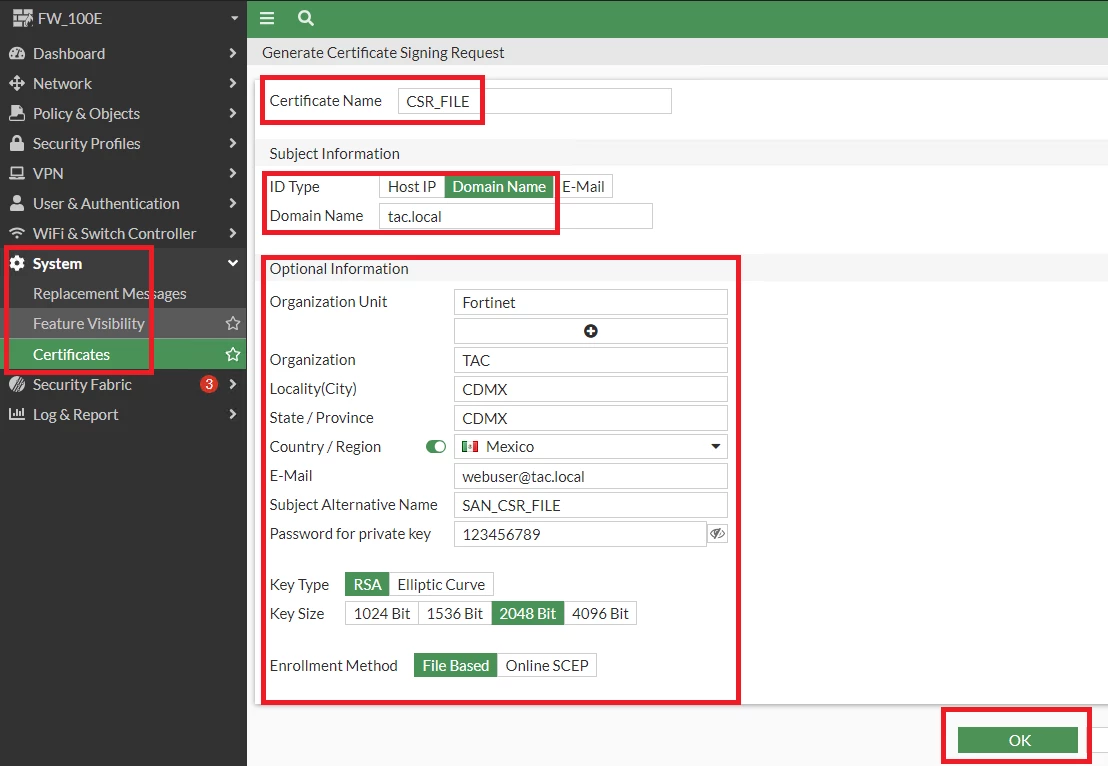
- Set Certificate Name.
- Select ID Type. You can select: 'Host IP', 'Domain Name' or 'E-Mail'.
Optional Information:
- Organization Unit.
- Organization.
- Locallity(City).
- State / Province.
- Country / Region.
- Email.
- Subject Alternative Name.
- Password for private key.
Select:
- Key Type.
- Key Size.
- Select Enrollment Method: File Based.
- Select 'OK'.
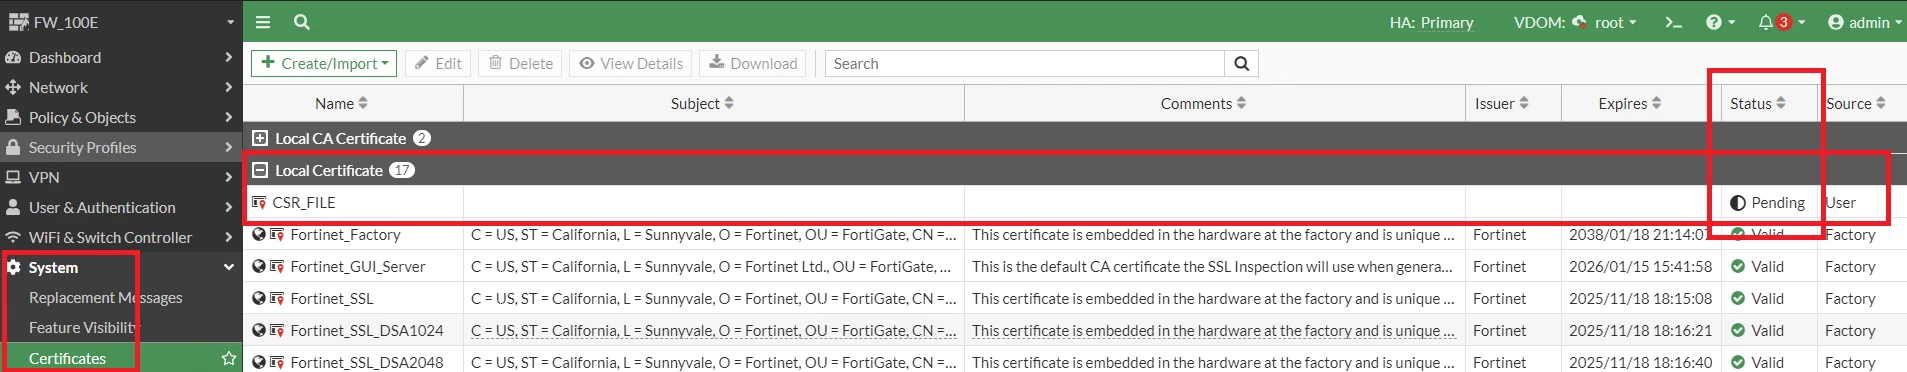
- FortiGate shows this certificate file as 'Local Certificate' and Status: 'Pending'.
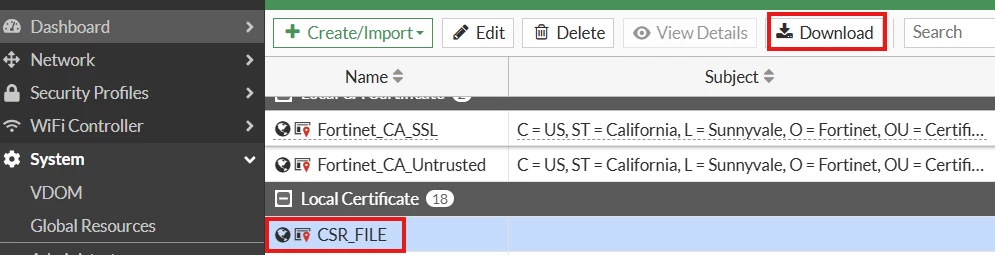
- Select the CSR File, download, and save.
2. Generating FortiAuthenticator Certificate Autority (CA).
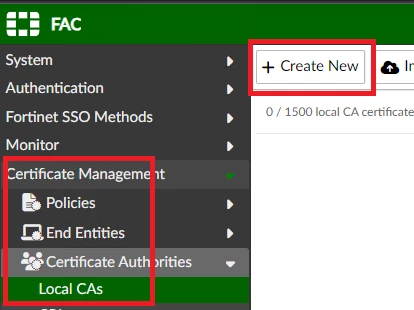
- Go to Certificate Management -> Certificate Authorities -> Local CAs -> Create New.
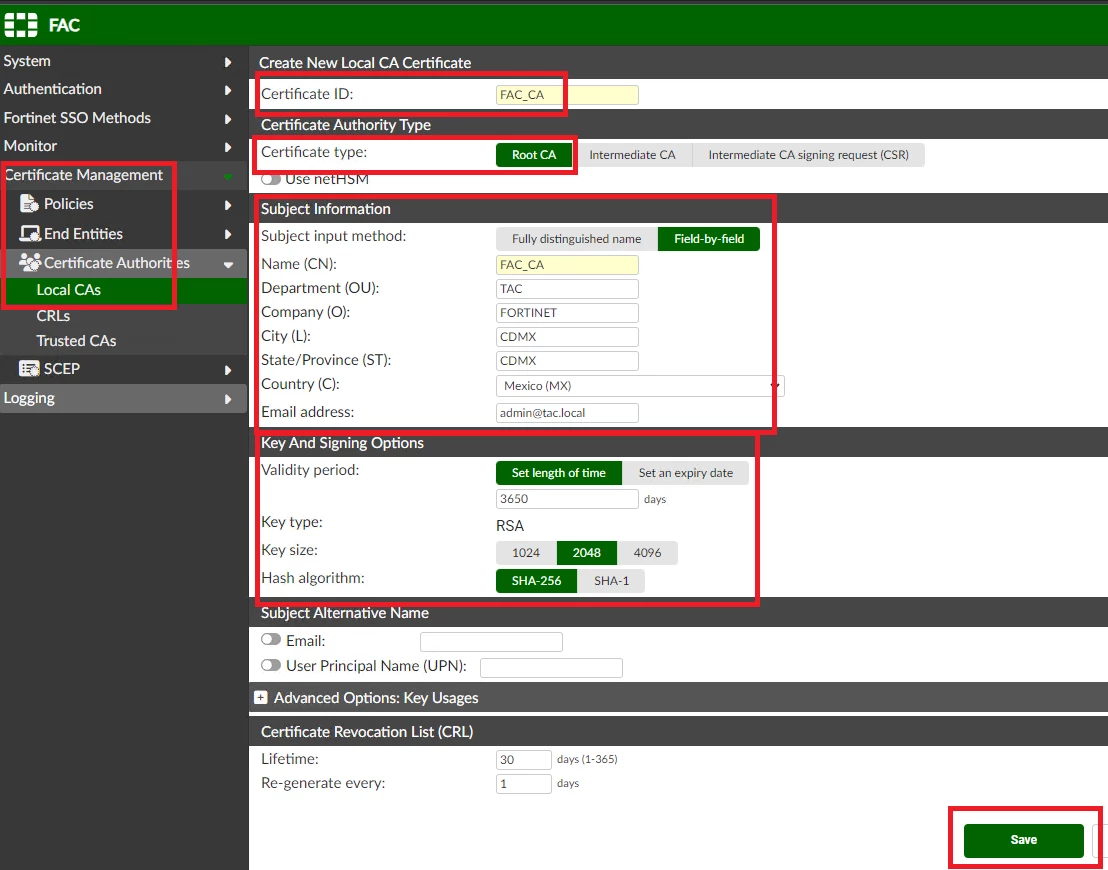
- Set Certificate ID.
- Select Certificate Authority Type: Root CA
- Select Subject input method.
- Complete Subject Information.
- Select Key And Signing Options.
Optional:
- Subject Alternative Name (SAN).
- Advanced Options: Key Usage.
- Certificate Revocation List (CRL).
- Select 'Save'.
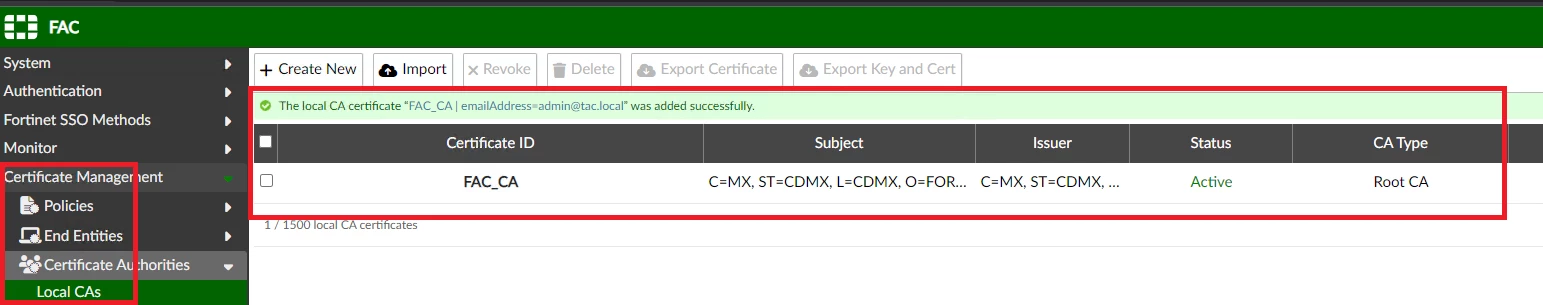
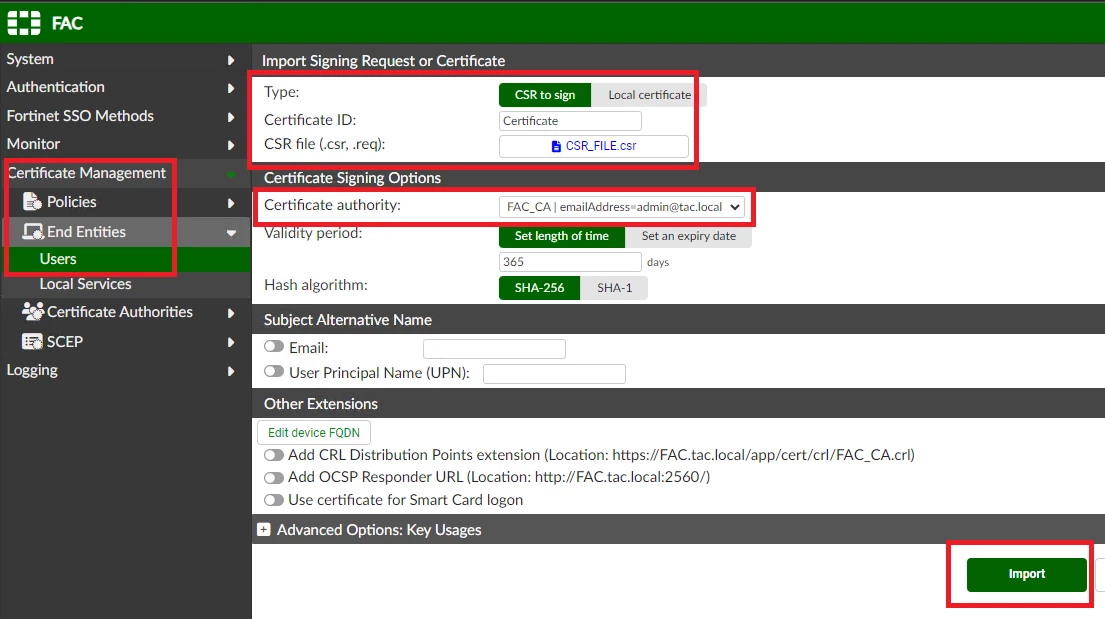
- To sign a CSR navigate to Certificate Management -> End Entities -> Users and select Import.
- Select Type: CSR to sign.
- Set Certificate ID.
- Upload CSR File created by Fortigate: CSR_FILE.csr
- Select the Certificate Authority created: FAC_CA
- A Subject Alternative Name can be specified. Note that FortiAuthenticator only supports email and User Principal Name(UPN).
- Select Import.
Note:
If a CSR is imported with a Subject Alternative Name as DNS or other fields, which is signed by the FortiAuthenticator. Those fields (Subject Alternative Name) will be deleted. Try to sign those CSRs with another CA.
Also, the purpose of this certificate can be selected, and the key usages needed.
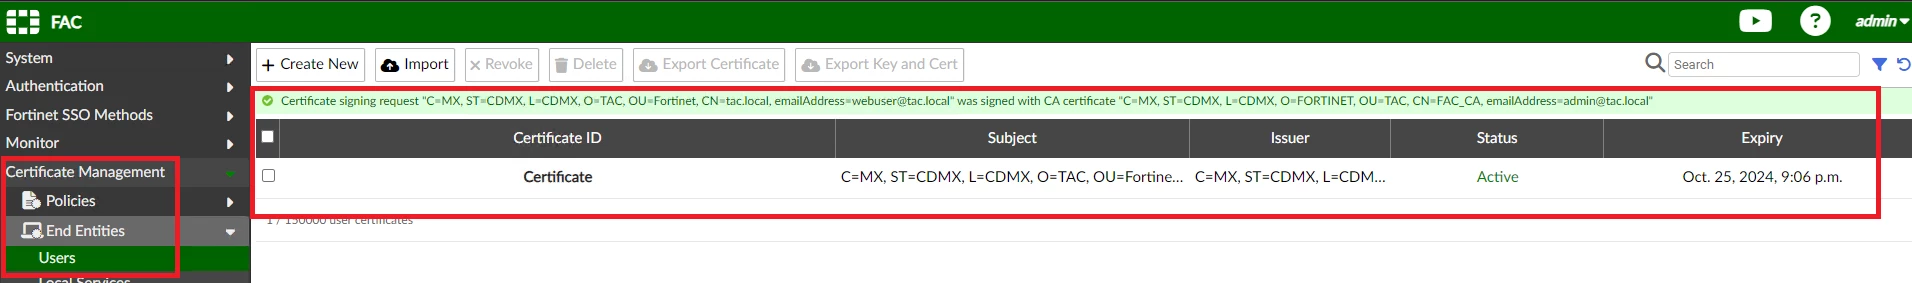
- Go to Certificate Management -> End Entities -> Users, select file and 'Export Certificate'.
- The type of this file will be: Security Certificate (.cer)
- File name: Certificate.cer
- Download and save.
Importing Signed File: Security Certificate (.cer) to FortiGate
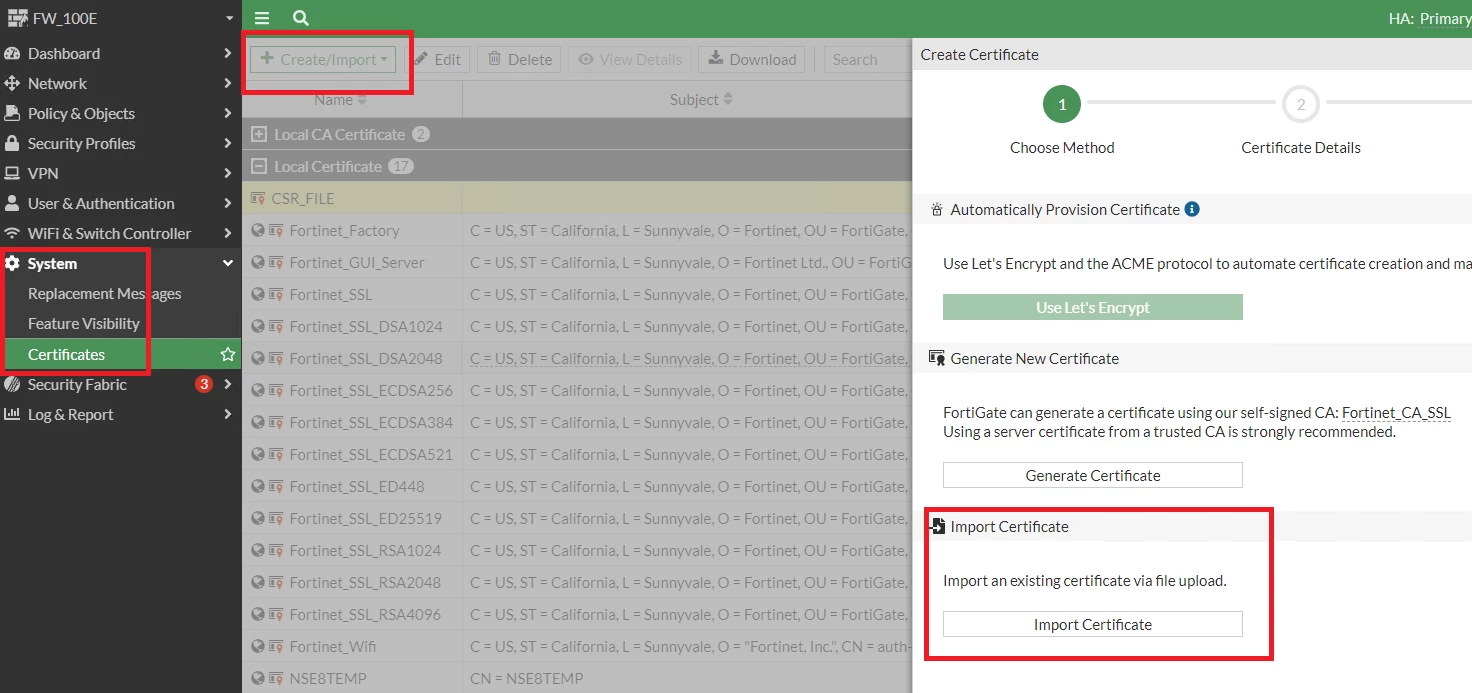
- Go to System -> Certificate -> Create/Import -> Select: 'Certificate' -> Import Certificate.
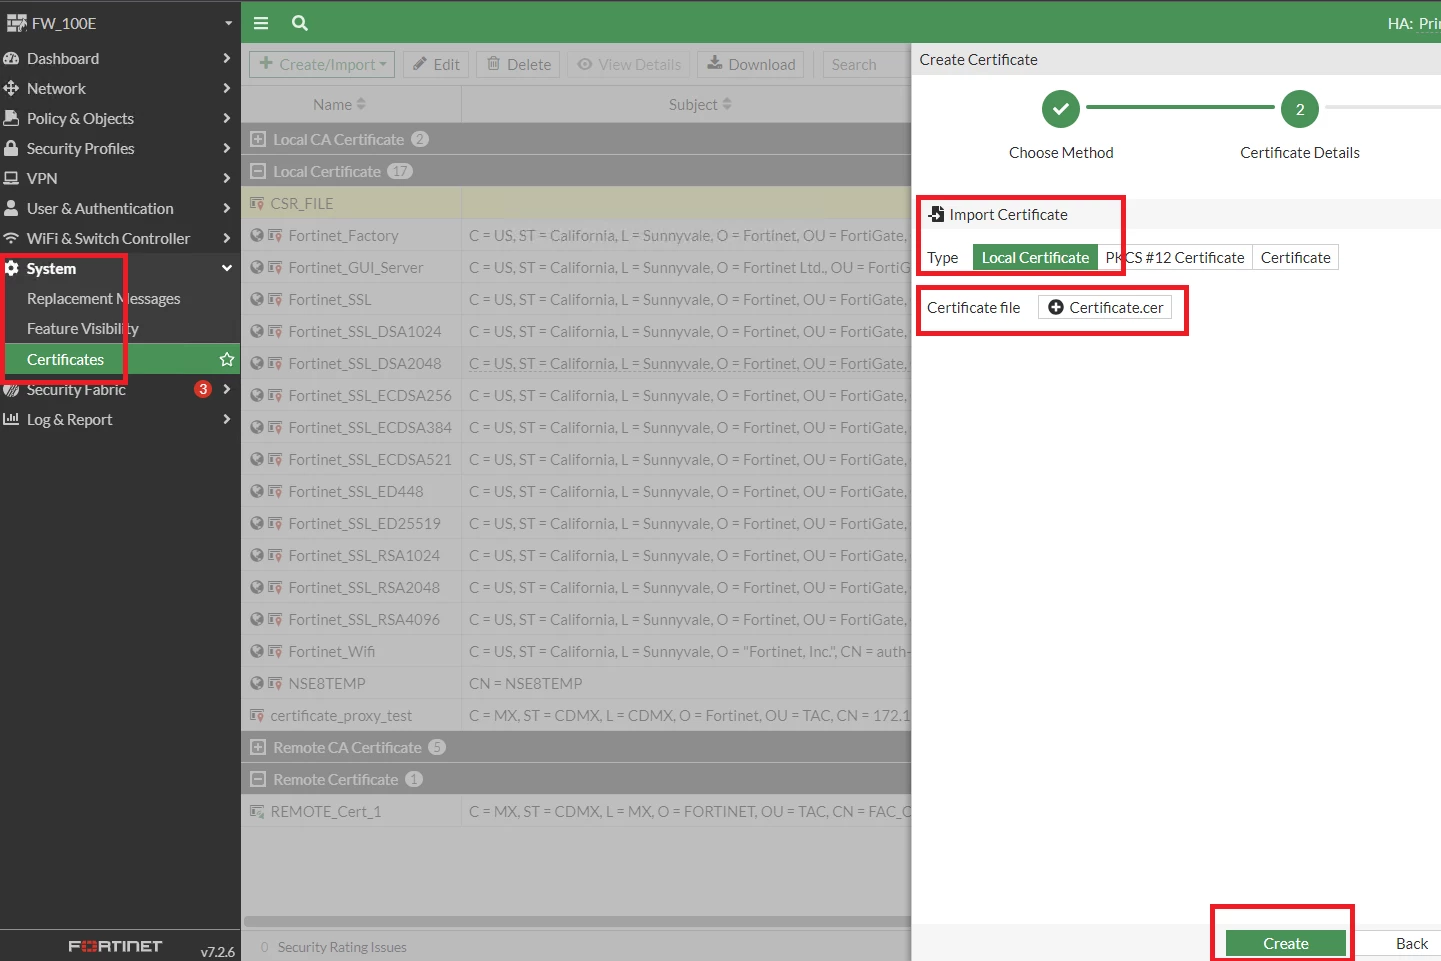
- Select Type: 'Local Certificate'.
- Certificate file: Certificate.cer
- Select 'Create'.
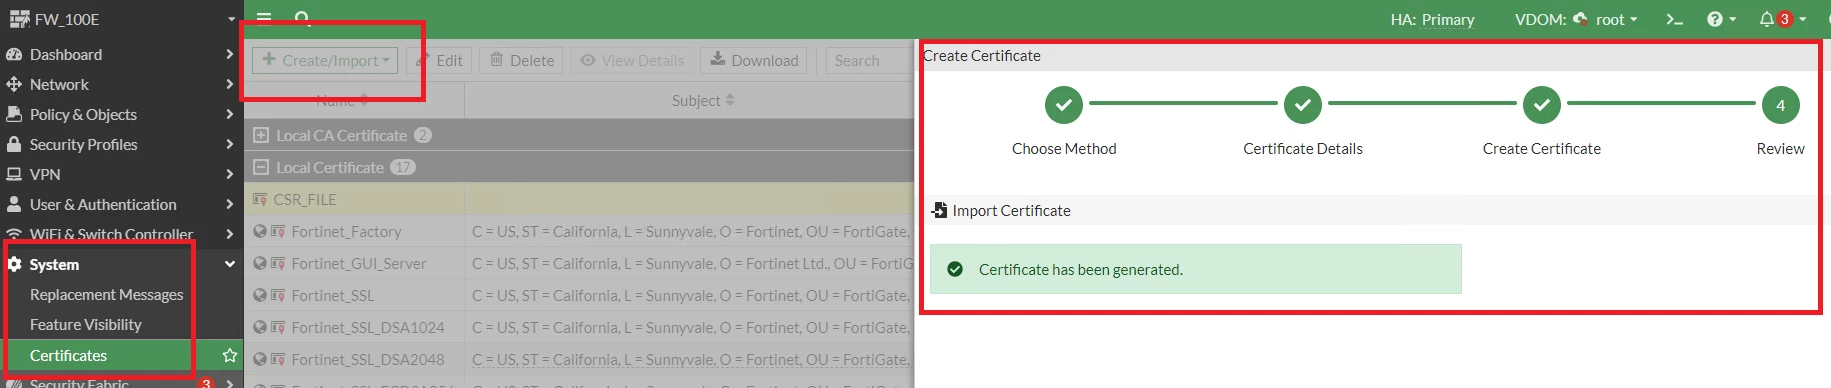
- After importing Certificate.cer to FortiGate, 'CSR_FILE' with status 'Pending' will change to status 'Valid'.
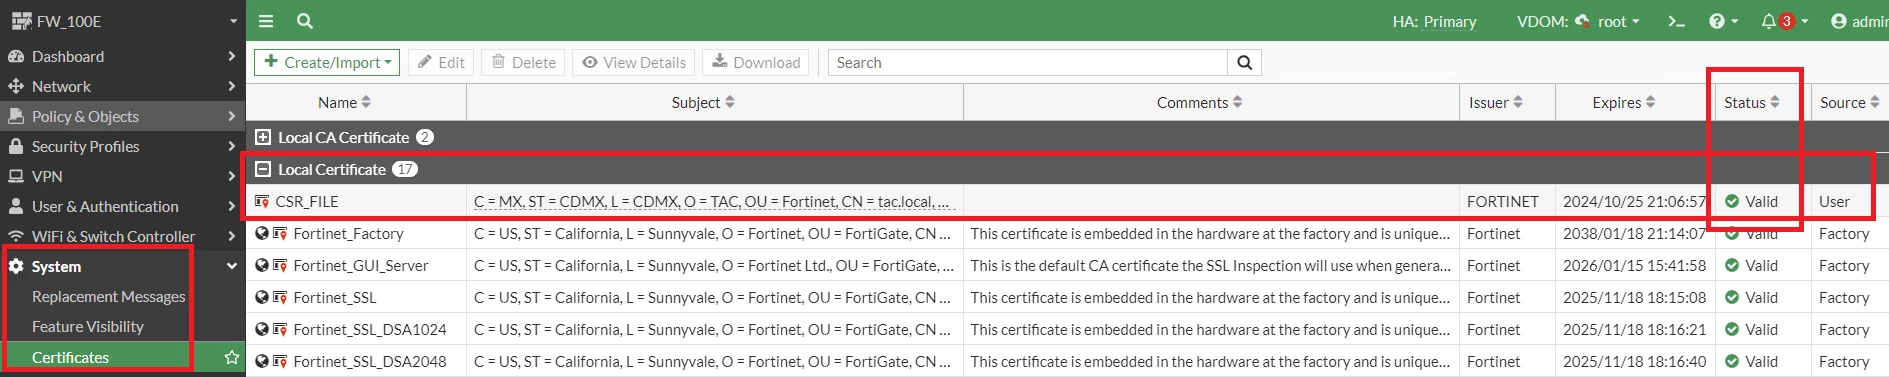
- It is possible to import CA created 'FAC_CA' file to FortiGate if needed.
For more details regarding the Certificate, refer to the documents below:

