


Technical Tip: How to resolve the 'EAP authentication failed due to missing token' error when using EAP-TTLS /PAP + 2FA Authentication
Description | This article describes how to resolve the EAP authentication failed due to missing token error while using EAP-TTLS/PAP with two-factor authentication in FortiAuthenticator. |
Scope | FortiAuthenticator v6.6.3+, FortiGate, FortiClient. |
Solution | FortiClient added support for EAP-TTLS in IPsec VPN starting with version 7.4.3. FortiAuthenticator, as a RADIUS server, supports EAP-TTLS with PAP when using an IPsec IKEv2 tunnel.
The FortiClient documentation provides instructions on enabling EAP-TTLS support for EMS-managed FortiClients: EAP-TTLS support for IPsec VPN.
For unlicensed (VPN-only) FortiClients, EAP-TTLS can be enabled by manually editing the configuration file. Technical Tip: How to enable EAP-TTLS for IPSec IKEv2 tunnels in VPN-only (unlicensed) FortiClient.
Note that EAP-TTLS MFA support for LDAP users requires the following minimum firmware versions:
On FortiAuthenticator, allowed EAP types are configured under: Authentication -> RADIUS Service -> Policies.
For more details, refer to:
Important: When using FortiAuthenticator as a RADIUS server, the EAP-TTLS authentication tunnel from FortiClient terminates on FortiAuthenticator, not on FortiOS.
For additional technical details, see: Technical Tip: FortiOS IKEv2 EAP user authentication operation.
However, when using EAP-TTLS/PAP with two-factor authentication and FortiAuthenticator as the RADIUS server, the error EAP authentication failed due to missing token may appear in the FortiAuthenticator RADIUS logs.
(23) facauth: Updated auth log 'abc@support' for attempt from 10.10.10.10~11.11.11.100: Remote LDAP administrator authentication partially done, expecting FortiToken (23) facauth: EAP authentication failed due to missing token. Additionally, no token prompt is displayed in FortiClient during the authentication process, and the authentication attempt fails with the following error message: 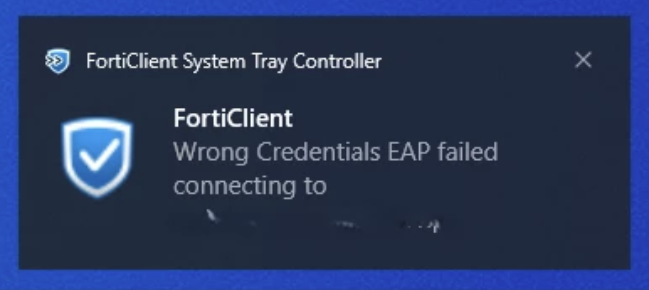 As of November 2025, no version of FortiAuthenticator supports challenge-based EAP-TTLS two-factor authentication (2FA).
As a workaround, users must use a concatenation token for EAP-TTLS 2FA, which combines the password and token. For example: p@ssw0rd345678.
Note: Since an email or SMS token can only be received after entering the username and password, token concatenation for EAP-TTLS does not work with SMS or Email as a two-factor method. This also applies to FortiIdentity Cloud (formerly FortiTokenCloud) if it uses SMS or Email for 2FA.
Related documents: |

