| In this scenario is shown an error which refers to unable authentication via Radius to Splunk servers using the FortiAuthenticator. Message: Remote LDAP user authentication from (null) with FortiToken failed: replay previous token. Authentication failed, use/replay previous token code. After FortiAuthenticator upgrades to v6.6.2, connecting to the Splunk server could lead to an error like this: 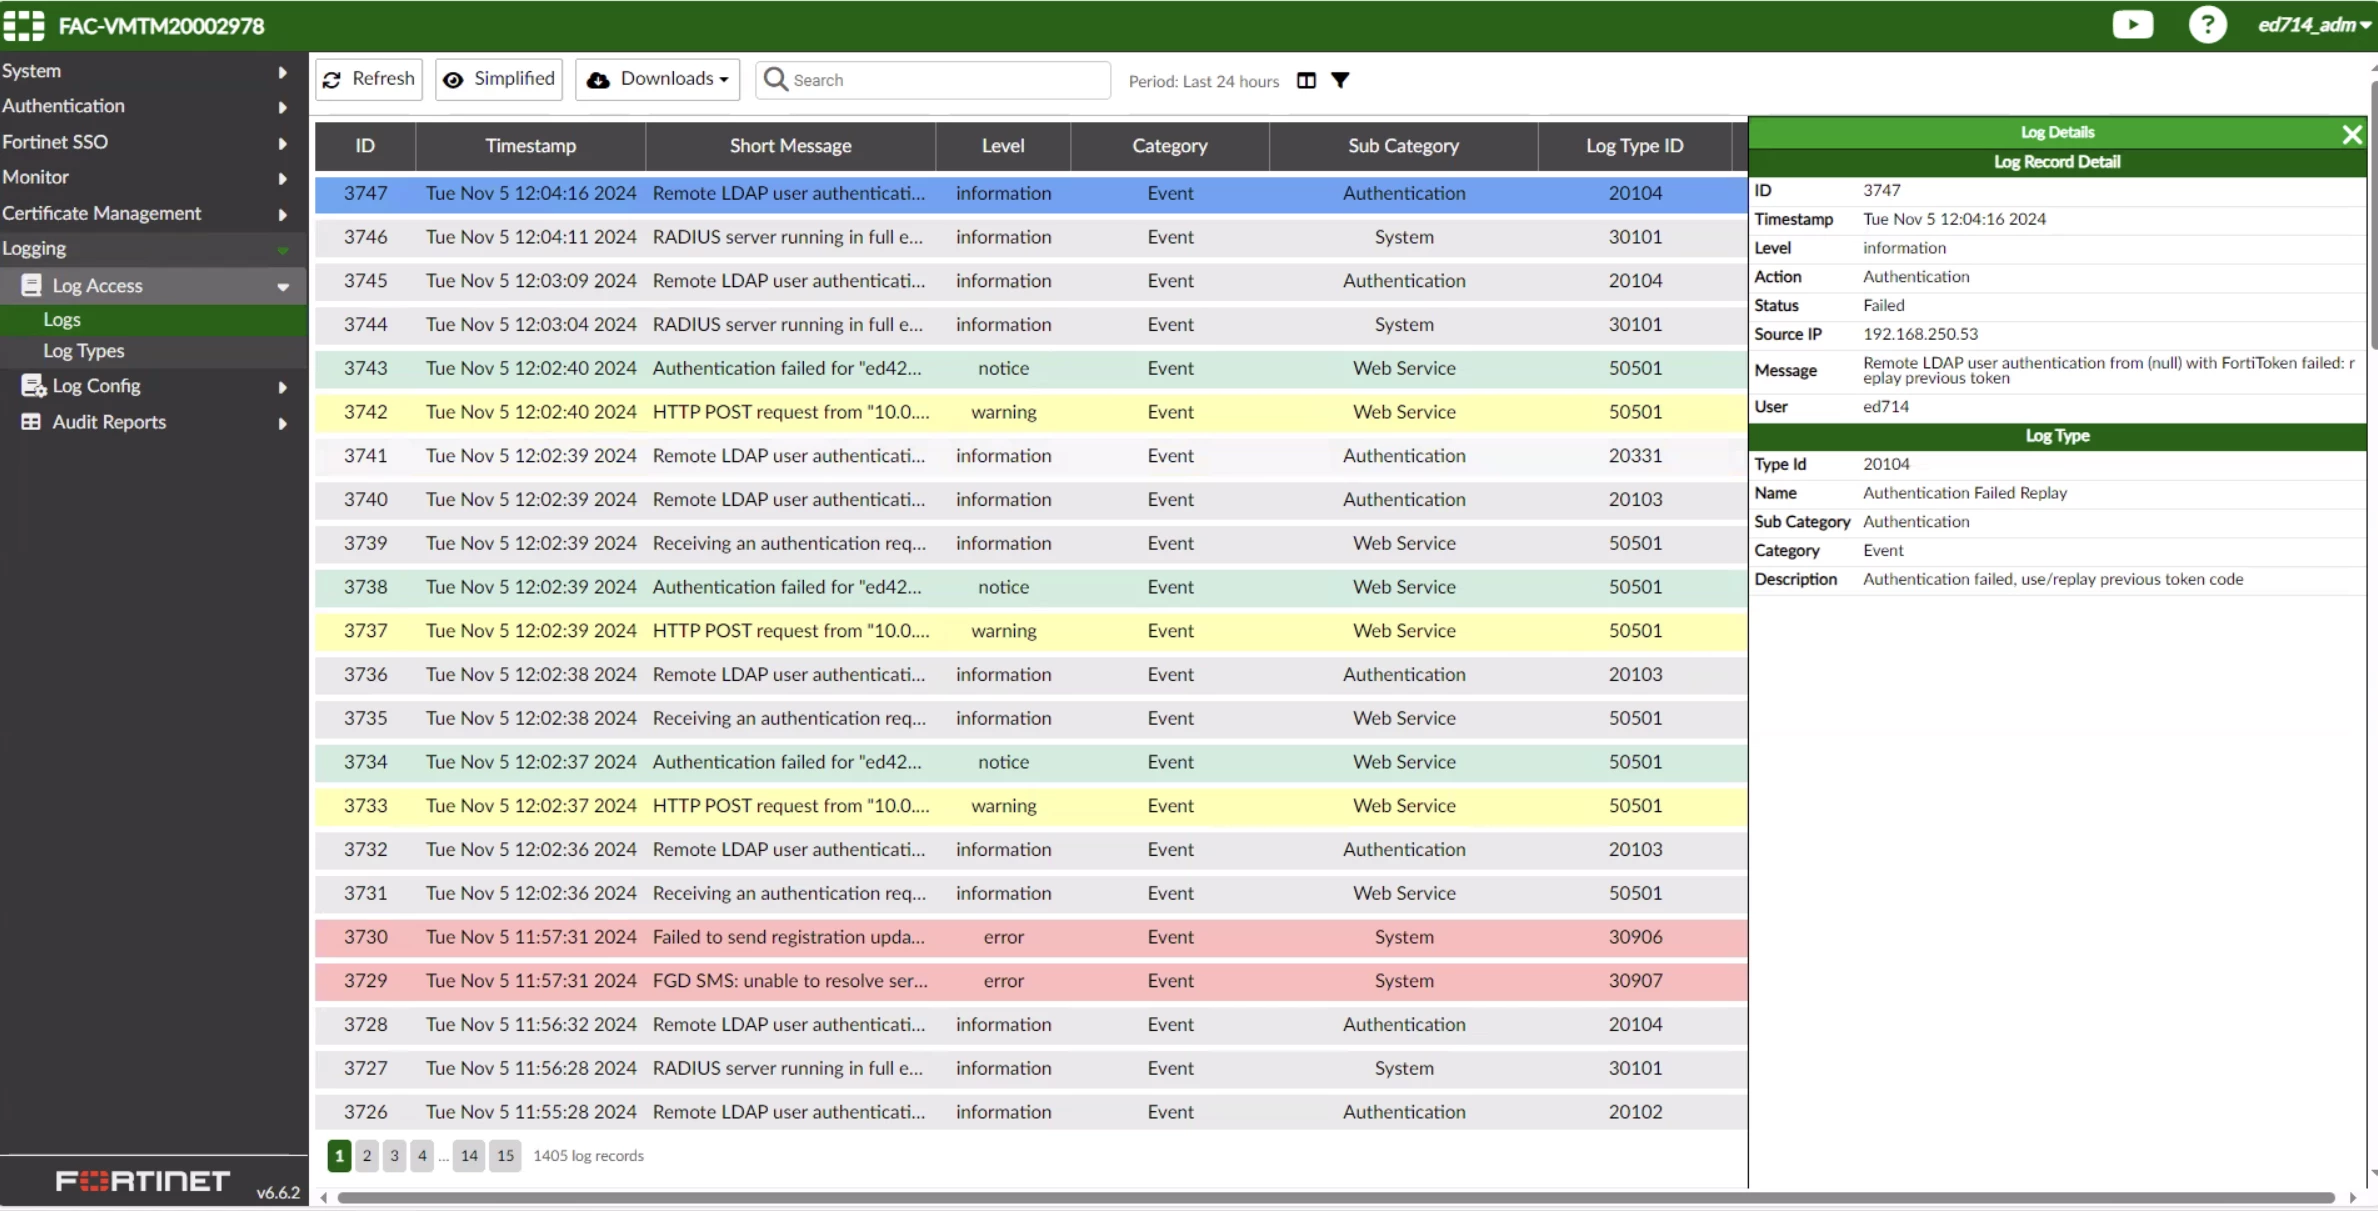
The first step is checking the FortiAuthenticator logs: FortiAuthenticator -> Logging -> Log Access -> Logs. In this example above, there is this error present: Remote LDAP user authentication from (null) with FortiToken failed: replay previous token. Authentication failed, use/replay previous token code. The next steps include checking further logs, like: - Radius Authentication logs.
- Kernel logs.
From the Radius authentication logs for this example: 2024-11-06T11:50:39.615999+08:00 lab-prdvfa03 radiusd[19152]: (0) facauth: Authentication OK
2024-11-06T11:50:39.616009+08:00 lab-prdvfa03 radiusd[19152]: (0) facauth: Setting 'Post-Auth-Type := FACAUTH' <--- last message seen.
2024-11-06T11:50:40.687241+08:00 lab-prdvfa03 radiusd[19181]: main {
2024-11-06T11:50:40.687265+08:00 lab-prdvfa03 radiusd[19181]: security {
2024-11-06T11:50:40.687275+08:00 lab-prdvfa03 radiusd[19181]: allow_core_dumps = no
2024-11-06T11:50:40.687290+08:00 lab-prdvfa03 radiusd[19181]: }
2024-11-06T11:50:40.687300+08:00 lab-prdvfa03 radiusd[19181]: name = "radiusd"
2024-11-06T11:50:40.687309+08:00 lab-prdvfa03 radiusd[19181]: prefix = "/usr"
2024-11-06T11:50:40.687322+08:00 lab-prdvfa03 radiusd[19181]: localstatedir = "/usr/var"
2024-11-06T11:50:40.687332+08:00 lab-prdvfa03 radiusd[19181]: logdir = "/usr/var/log/radius"
2024-11-06T11:50:40.687341+08:00 lab-prdvfa03 radiusd[19181]: run_dir = "/usr/var/run/radiusd"
2024-11-06T11:50:40.687351+08:00 lab-prdvfa03 radiusd[19181]: } From the Kernel logs for this example: 2024-11-06T11:50:39.617860+08:00 lab-prdvfa03 kernel: [508108.602445] radiusd[19170]: segfault at 10 ip 00007f4fb7e9aaac sp 00007f4fa6ffbe90 error 6 in rlm_facauth.so[7f4fb7e91000+20000]
2024-11-06T11:50:39.617875+08:00 lab-prdvfa03 kernel: [508108.602460] Code: 08 89 4c 24 24 89 04 24 44 89 c8 8b 34 24 c1 e8 10 44 89 4c 24 18 89 c2 89 44 24 04 e8 6d 7e ff ff 8b 4c 24 24 44 8b 4c 24 18 <c7> 40 10 09 00 00 00 49 89 c5 ff c9 74 1e 4d 85 ff 0f 84 75 01 00 Additional logs: File "./fac/fac/common/admin.py", line 323, in changelist_view
File "./fac/fac/common/admin.py", line 102, in changelist_view
File "/lib/python3.11/site-packages/django/utils/decorators.py", line 43, in _wrapper
return bound_method(*args, **kwargs)
^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
File "/lib/python3.11/site-packages/django/utils/decorators.py", line 130, in _wrapped_view
response = view_func(request, *args, **kwargs)
^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
File "/lib/python3.11/site-packages/django/contrib/admin/options.py", line 1739, in changelist_view
response = self.response_action(request, queryset=cl.get_queryset(request))
^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
File "/lib/python3.11/site-packages/django/contrib/admin/options.py", line 1408, in response_action
response = func(self, request, queryset)
^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
File "./fac/fac/common/actions.py", line 339, in edit
AttributeError: 'RadiusVendor' object has no attribute 'id' From the logs, after each attempt at login to the Splunk server via Radius authentication with FortiAuthenticator, the Radiusd service is crashing. Time in the kernel logs and radius authentication logs match the crash. Note: This scenario explains when the upgrade is done without modifying users, user groups, policies, etc. How to avoid this scenario: - Delete the Custom Vendor object 'Splunk' in FortiAuthenticator -> Authentication -> RADIUS Service -> Dictionaries -> Custom Vendors -> Locate the wanted object and delete it.
- Create a new object and upload the file that contains the object 'Splunk'.
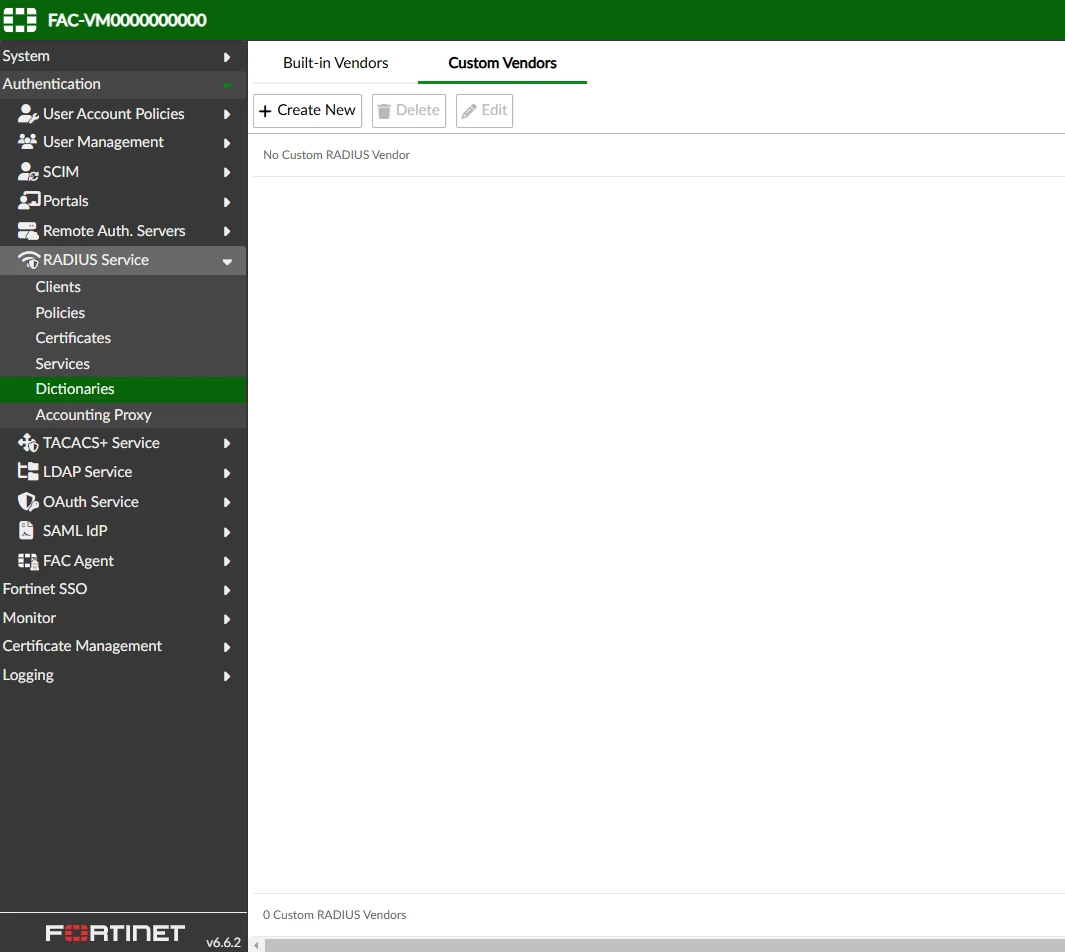
Try the connection again; the 500 error on the server should not be visible anymore. | 



