Technical Tip: How to configure secondary LDAP on FortiAuthenticator
| Description | This article describes how to configure secondary LDAP and troubleshoot. |
| Scope | FortiAuthenticator. |
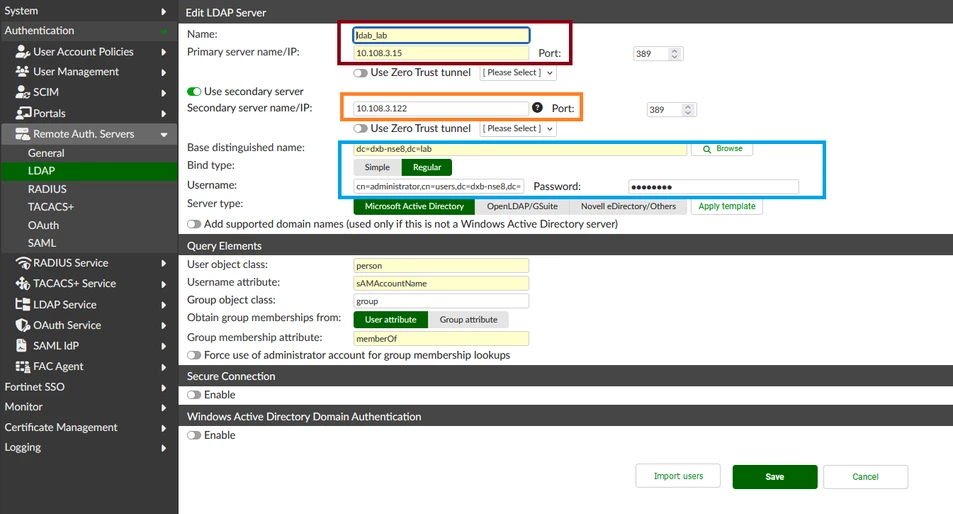
| Solution | The user should have 2 LDAP servers with the same domain name, in this case, below are the LDAP servers:
On FortiAuthenticator configure the LDAP configuration below:
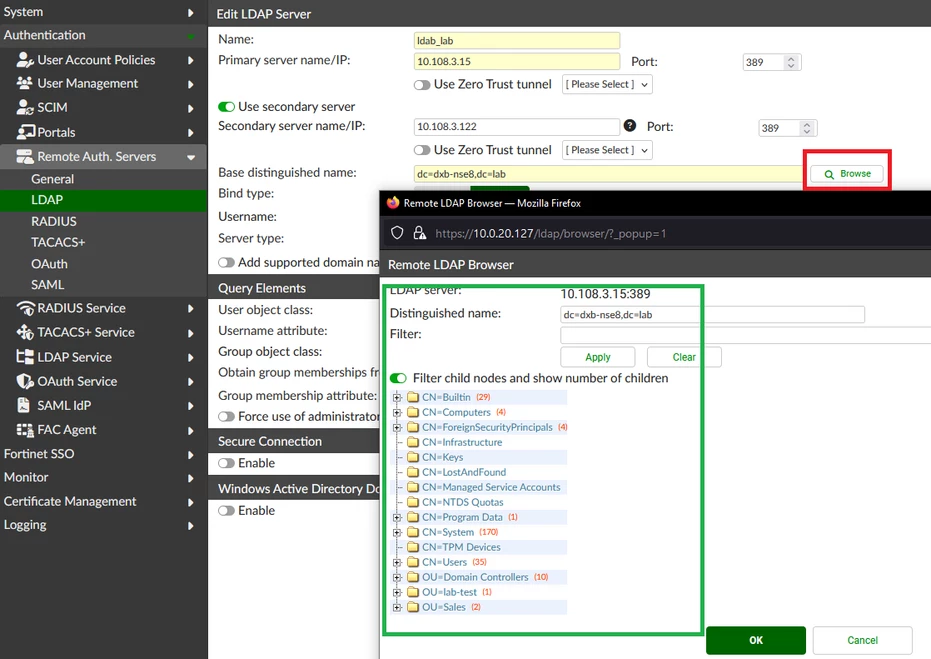
The user can try to press the 'Browse' option to verify whether the LDAP server is working or not.
To verify whether the secondary LDAP 10.108.3.122 is working or not, the user has to disable the NIC on the primary server or make sure the primary LDAP is not reachable from FortiAuthenticator (by changing the IP address)
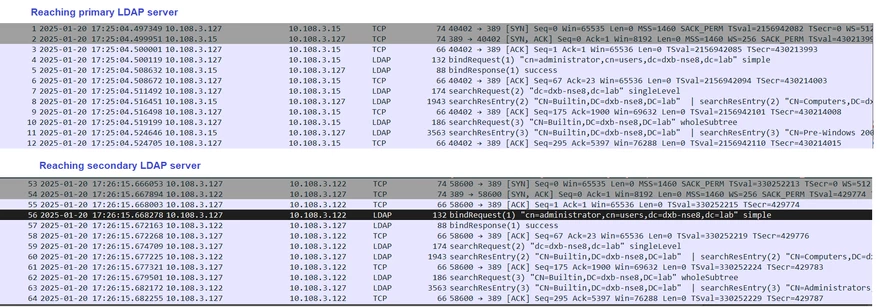
Then start the packet capture on the respective interface on FortiAuthenticator, then browse the LDAP as above, now the traffic should reach the secondary server.
Refer to the below sniffer traces:
|