


Technical Tip: How to configure LDAP services on FortiAuthenticator and integrate it to FortiGate for authentication
Description
This article describes how to configure the LDAP service on FortiAuthenticator and use FortiAuthenticator as an LDAP authentication server for FortiGate.
Scope
FortiAuthenticator, FortiGate.
Solution
Diagram.
User/client <----> FortiGate <----> FortiAuthenticator (LDAP authentication).
FortiAuthenticator configuration.
Enable the LDAP service on the FortiAuthenticator interface that communicates with the FortiGate.
Go to System -> Network -> Interfaces, edit the required interface, and under Access Rights -> Services, select LDAP (TCP/389).
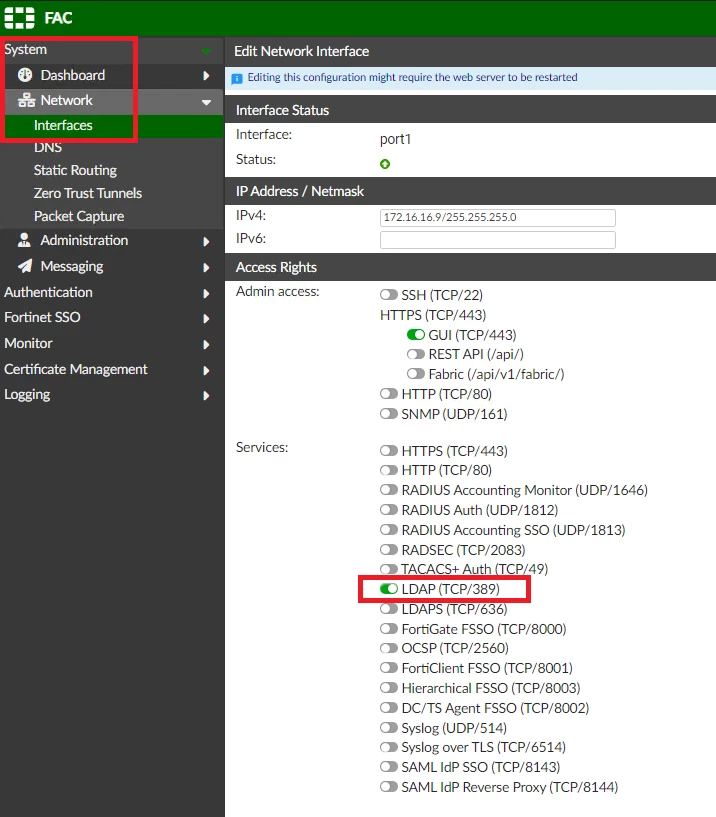
This example uses LDAP over TCP/389. For an encrypted connection, enable LDAPS or STARTTLS and configure the required certificate settings. LDAPS uses TCP/636.
Create the local groups.
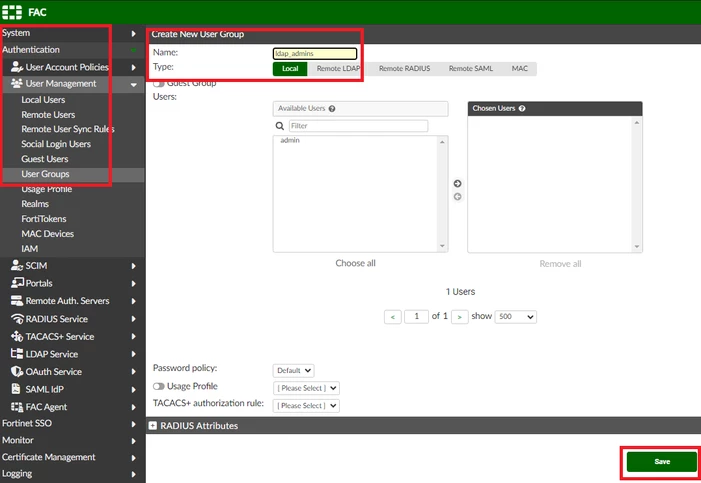
Create the 'ldap_admins' group.
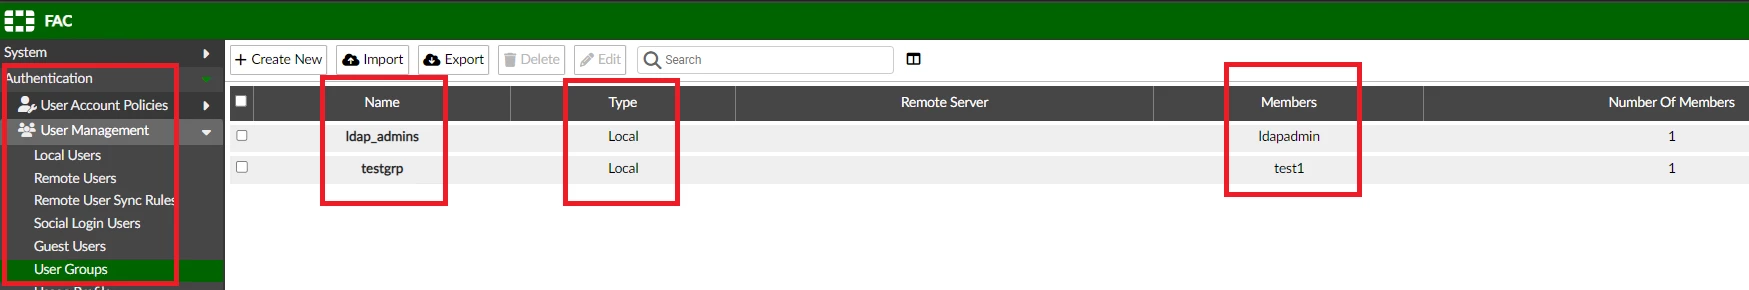
Go to Authentication -> User Management -> User Groups, select Create New, and create a local group named 'ldap_admins'.
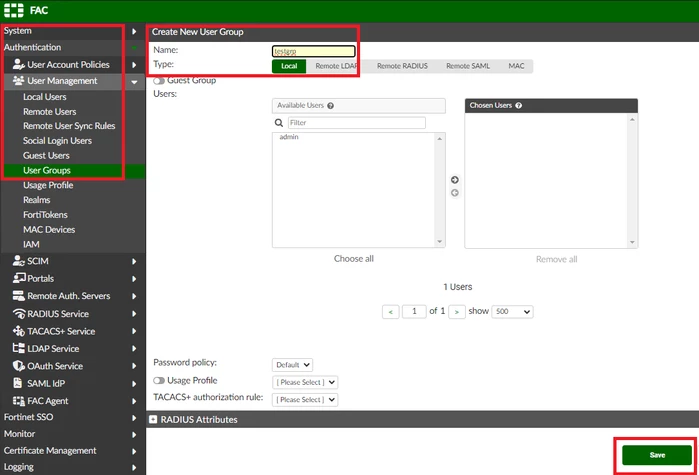
Create the authentication user group. Go to Authentication -> User Management -> User Groups, select Create New, and create a local group named 'testgrp'.
Create the local users and add them to the required groups.
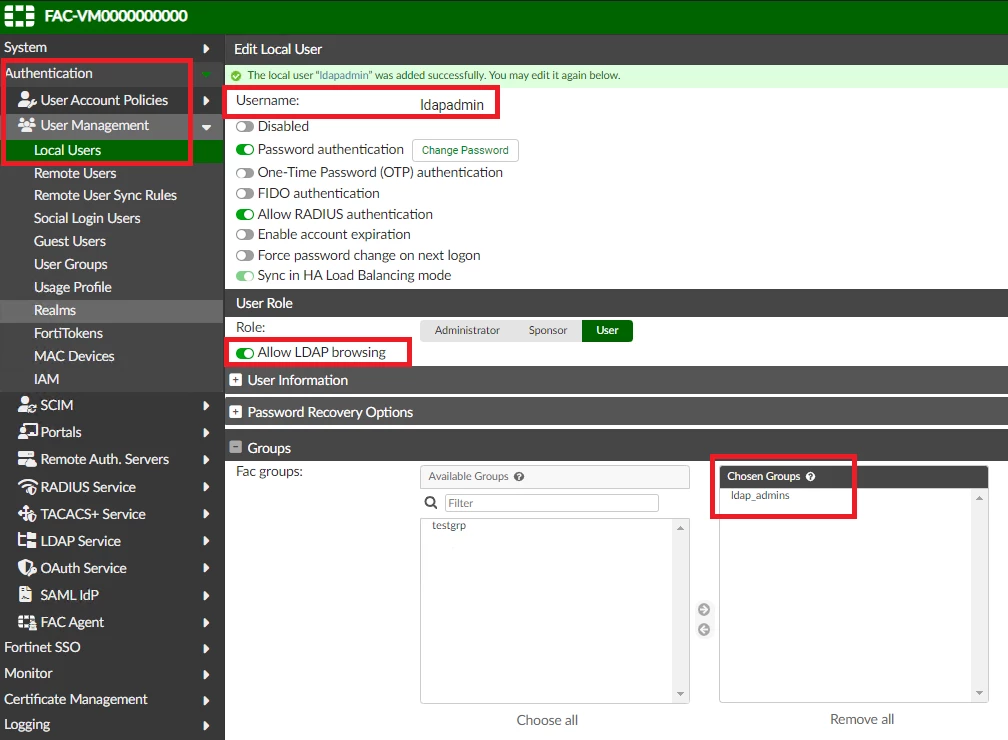
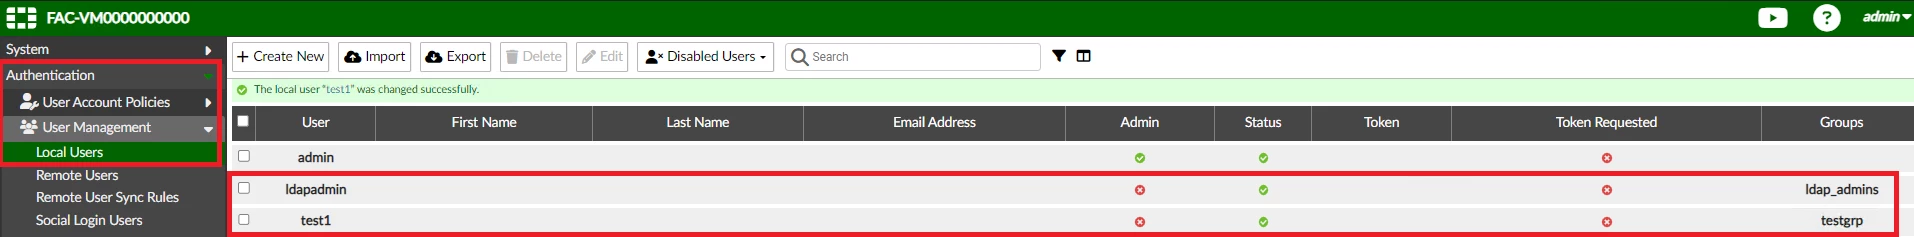
Go to Authentication -> User Management -> Local Users and select Create New. Add 'ldapadmin' to the 'ldap_admins' group.
Enable Allow LDAP browsing for the 'ldapadmin' account. This account is used by FortiGate to bind to and search the FortiAuthenticator LDAP directory.
Add 'test1' to the 'testgrp' group.
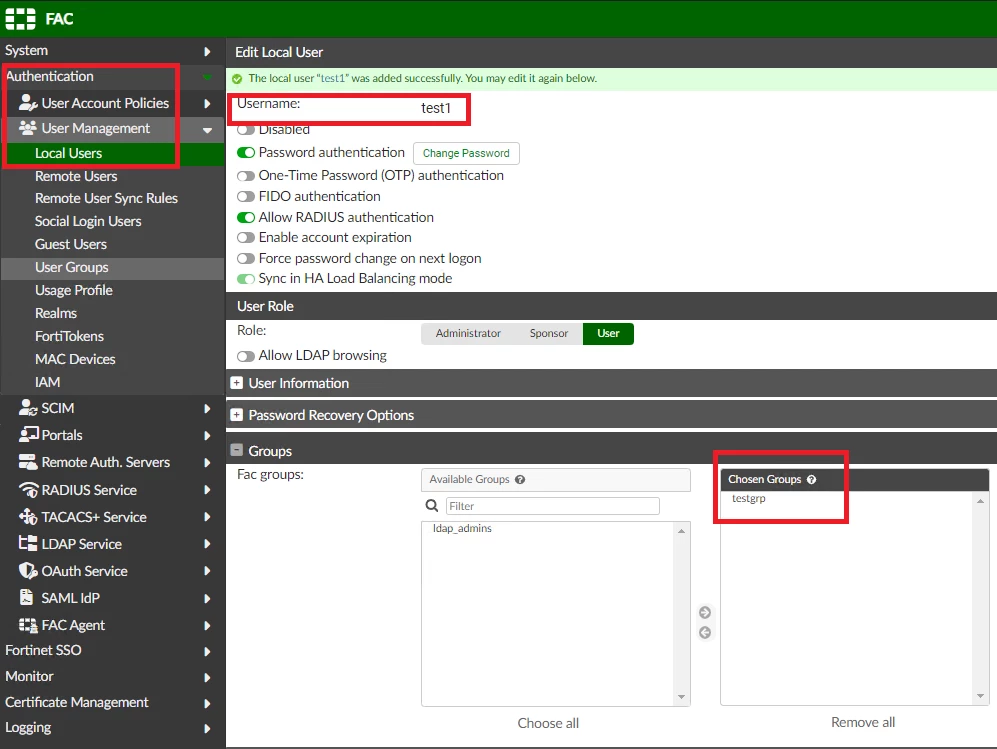
The resulting local user configuration is shown below.
The resulting local group configuration is shown below.
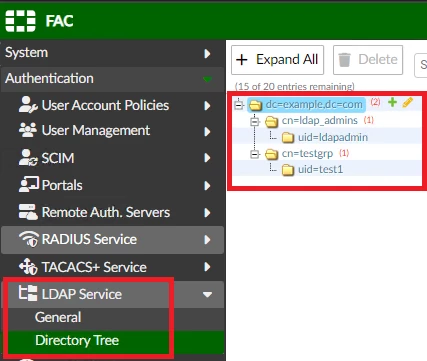
Configure the LDAP directory tree.
Go to Authentication -> LDAP Service -> Directory Tree.
Add the LDAP bind account and the required authentication users to the directory tree. The Distinguished Name configured on FortiGate must identify an LDAP node under which the required user accounts can be found.
The 'ldapadmin' account used for LDAP searches must be present in the FortiAuthenticator LDAP directory tree and have Allow LDAP browsing enabled.
FortiGate configuration.
Configure FortiAuthenticator as an LDAP server.
Go to User & Authentication -> LDAP Servers and select Create New.
Configure the LDAP server with the following settings:
Server IP/Name: FortiAuthenticator IP address or FQDN.
Server Port: 389 for LDAP in this example.
Common Name Identifier: uid.
Distinguished Name: The LDAP node containing the required user accounts in the FortiAuthenticator directory tree.
Bind Type: Regular.
Username: The DN of the LDAP bind account configured in the FortiAuthenticator directory tree.
Password: The password of the LDAP bind account.
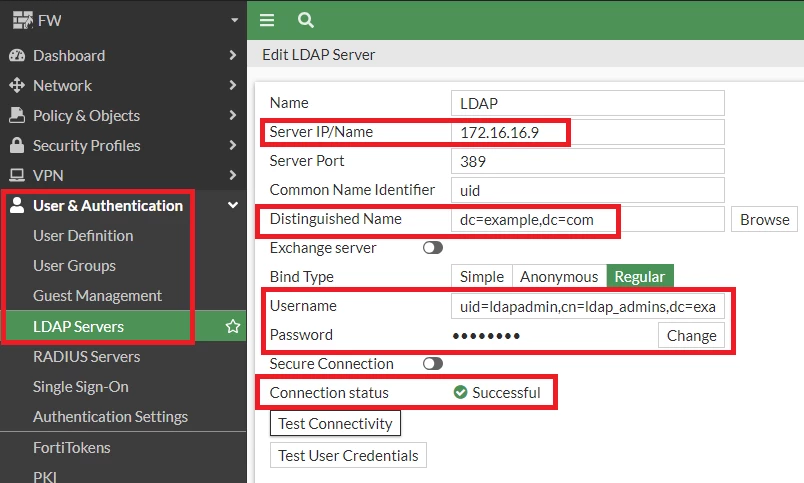
Test LDAP authentication from the FortiGate CLI.
Use the following command syntax:
diagnose test authserver ldap <LDAP_server_name> <username> <password>
Example:
diagnose test authserver ldap LDAP ldapadmin <password>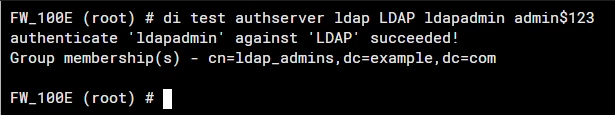
Verify the FortiAuthenticator authentication log.
Go to Logging -> Log Access -> Logs and locate the authentication event for the tested account.
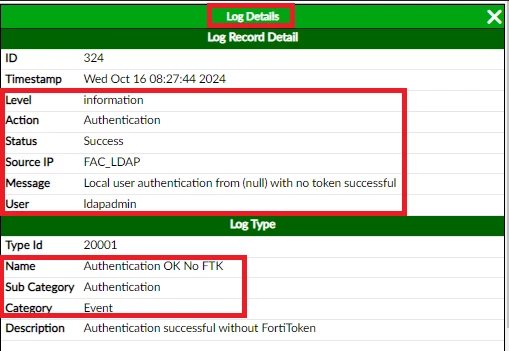
Create the FortiGate user group.
Go to User & Authentication -> User Groups and select Create New.
Enter a group name. Under Remote Groups, add the FortiAuthenticator LDAP server and select the required LDAP group.
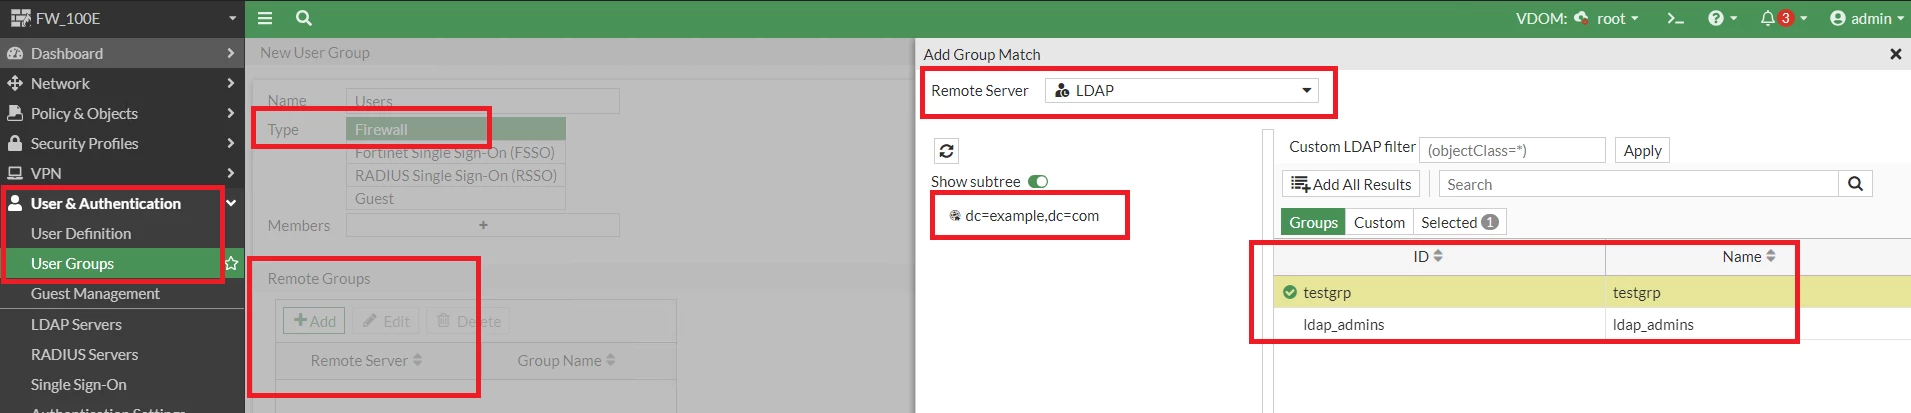
Use the FortiGate user group in the required firewall authentication policy.
To troubleshoot LDAP authentication on FortiGate, run the following commands and reproduce the authentication attempt:
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug application fnbamd -1
diagnose debug enable
After reproducing the issue, stop and reset the debug:
diagnose debug disable
diagnose debug reset
Example debug output:
2025-09-11 13:40:08 [1982] ldap_copy_grp_list-copied cn=ldap_admins,dc=example,dc=com
2025-09-11 13:40:08 [195] find_matched_usr_grps-Skipped group matching
2025-09-11 13:40:08 [2553] fnbamd_ldap_result-Result for ldap svr LDAP is SUCCESS
2025-09-11 13:40:08 [2564] fnbamd_ldap_result-Skipping group matching
2025-09-11 13:40:08 [909] update_auth_token_session-config does not require 2fa
2025-09-11 13:40:08 [239] fnbamd_comm_send_result-Sending result 0 (nid 0) for req 120598576119810, len=2629
2025-09-11 13:40:08 [600] destroy_auth_session-delete session 120598576119810
A result value of 0 indicates authentication success. A result value of 1 indicates authentication failure.
For additional FortiAuthenticator debug information, open:
https://<FortiAuthenticator_IP_or_FQDN>/debug
Related documents:


