Technical Tip: How to bypass the 2FA option
Description
This article describes the option that allows bypassing the 2FA option on the OWA agent for users without a FortiToken in FortiAuthenticator.
Scope
FortiAuthenticator.
Solution
- When the FortiAuthenticator OWA agent is integrated with an Exchange Server for Outlook Web Access (OWA) secured with 2FA, the 2FA prompt applies to all users.
- All users must be assigned a FortiToken in FortiAuthenticator to be allowed access.
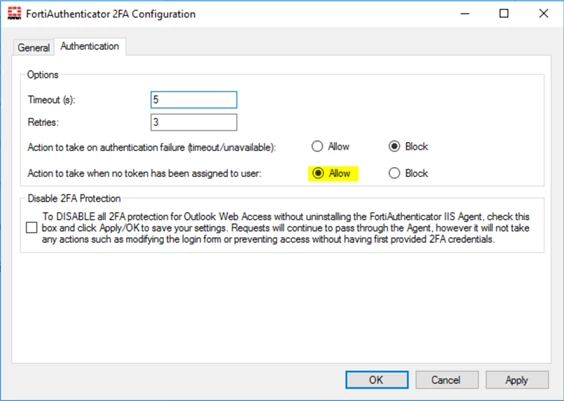
- In certain cases, to allow access for some users who are already imported into FortiAuthenticator but do not have 2FA provisioning, the following option can be enabled.
From GUI:
Go to OWA agent -> Authentication -> Options and allow the option 'Action to take when no token has been assigned to user'.