



Technical Tip: How to automatically assign Hardware FortiToken to a LDAP
Description
This article describes how to automatically assign LDAP users Hardware FortiTokens.
This is beneficial in case the user is deleted due to OU migration and when it is necessary to update the new user details with the new DN.
Scope
FortiToken.
Solution
- Assign the Hardware FortiToken to the serialNumber Attribute in the LDAP attributes:
Select the designated user and select Properties -> Attribute editor -> search for serialNumber Attribute and add the FortiToken after the list of FortiTokens to FortiAuthenticator is imported.
Note.
It is possible to select any available attribute.
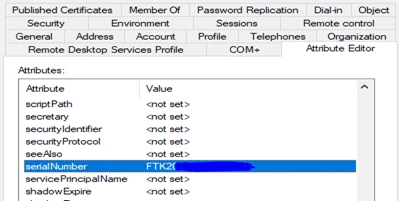
- On FortiAuthenticator go to Authentication -> User Management -> Remote User Sync Rules and create a new rule or modify existing rules.
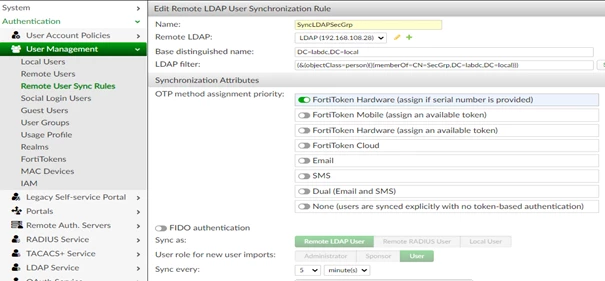
Amongst OTP method assignment priority: 'FortiToken Hardware (assign if serial number is provided)' should be the first option on top, it is possible to drag and drop to reorder:
In the same tab, under 'LDAP User Mapping Attributes', indicate 'serialNumber' in the FortiToken-200 serial number field.
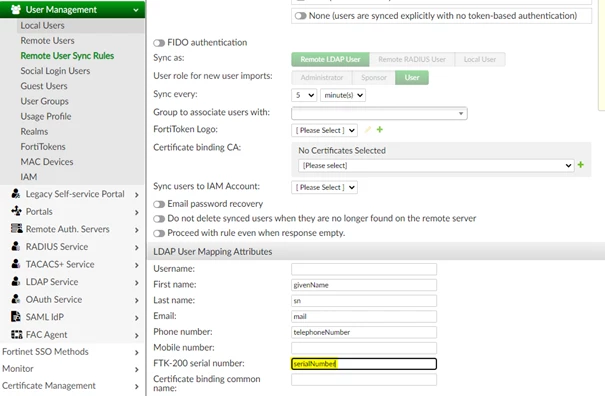
After doing the changes select 'Ok' to save the rule.
Finally, it is possible either to wait for users to be automatically synced or it is possible to manually initiate the Rule sync by checking the box next to the rule name and selecting 'Manual Sync'.
Finally, it is possible either to wait for users to be automatically synced or it is possible to manually initiate the Rule sync by checking the box next to the rule name and selecting 'Manual Sync'.
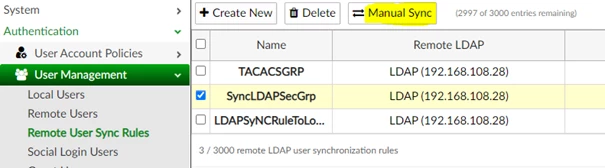
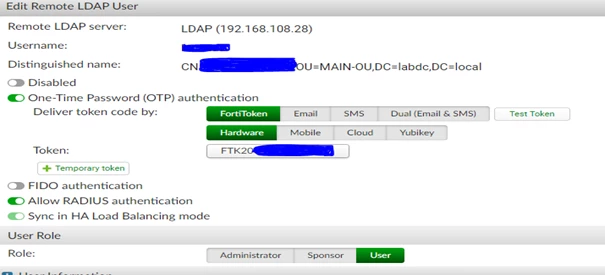
ForiToken will be automatically assigned to the user after Automatic or Manual Sync:
The solution can be applied to SAML sync rules also as long as there is a user attribute that contains the correct hardware Fortitoken serial number, and it is already claimed on the FortiAuthenticator.

