| For example, errors like the following may appear: ***
08/26/2022 15:58:32 [3897F700] libfac_comm: SSL server connection failed: sock: 10 error: SSL_ERROR_SSL(1): code=0x1417c0c7: error:1417C0C7:SSL routines:tls_process_client_certificate:peer did not return a certificate;
08/26/2022 15:58:32 [3897F700] FCT session SSL connection failed (IP): SSL_ERROR_SSL(1): code=0x1417c0c7: error:1417C0C7:SSL routines:tls_process_client_certificate:peer did not return a certificate;
08/26/2022 15:58:32 [3897F700] FCT disconnected: IP
*** Logs from the Agent: ***
8/26/2022 4:00:59 PM Debug SSOMA Start to resolve address for FortiAuthenticator:IP, TICC:832890, TID:1248
8/26/2022 4:00:59 PM Debug SSOMA Succeeded to resolve address for FortiAuthenticator:IP, FAC IP:IP, TICC:832890, TID:1248
8/26/2022 4:00:59 PM Debug SSOMA SendAndReceive(), Local IP:IP, FAC IP:IP, FAC Port:8001, TICC:832890, TID:1248
8/26/2022 4:00:59 PM Debug SSOMA ReceiveServerReply(), failed to receive hello message from authenticator, TID:1248
8/26/2022 4:00:59 PM Debug SSOMA SendAndReceive(), failed to send event to authenticator, TID:1248
*** To resolve this error, follow these instructions: - In 6.4.5, disable 'Enable encryption' under Fortinet SSO Methods - > SSO - > General.
- In 6.6.2, disable 'Enable encryption' under Fortinet SSO - > Settings - > FortiGate.
FortiAuthenticator now offers a server-side TLS support option so that FortiGate as an FSSO client can be configured to connect to FortiAuthenticator over a TLS connection, and this is enabled by default after an upgrade. Disable this by moving the toggle 'Enable encryption' under Fortinet SSO Methods -> SSO -> General or Fortinet SSO -> Settings -> FortiGate. 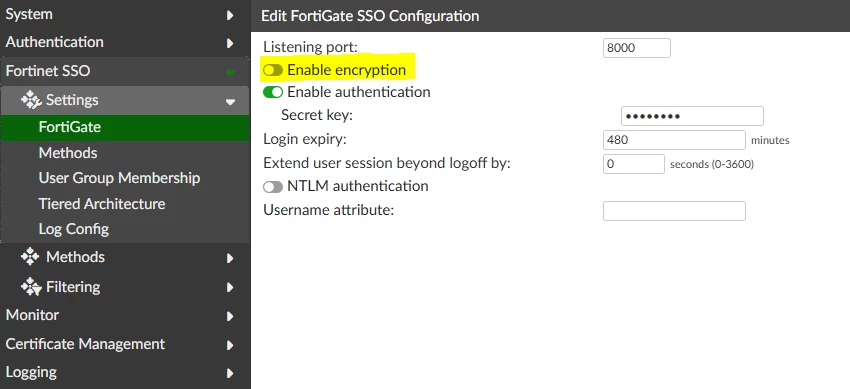
Note: Encrypted FSSO on FortiAuthenticator simply uses TCP/8000 (same as unencrypted).
When there is a change in FortiGate connector from unencrypted FSSO with TCP/8000 to encrypted, it automatically changes the port from TCP/8000 to TCP/8001. | 




