Technical Tip: FortiAuthenticator realm based authentication
Description
This article describes how users can authenticate with 'user@domain-name' as the username on a FortiAuthenticator.
Scope
Any supported version of FortiAuthenticator.
Solution
The objective in this example is to authenticate user 'administrator' against the domain 'forti.lab'.
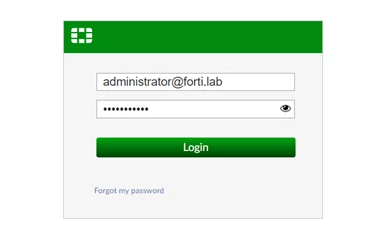
The username is 'administrator@forti.lab'.
- Create a realm. The realm should match the exact name of the domain. Select the LDAP server as the source. In this case, 'forti.lab' is used.
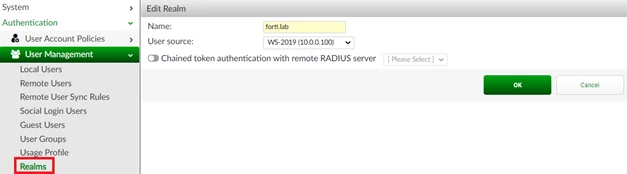
For more information regarding realms, see this article: Technical Tip: Realm-based authentication with local and remote users.
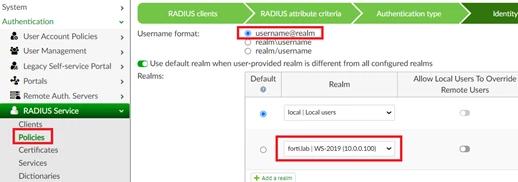
- Create a RADIUS client here, FortiGate/NAS is used as a radius client on FortiAuthenticator, and the realm is selected as the option for the authentication source.
Note: The default is still left with FortiAuthenticator local DB.
Next, authenticate with the domain name.
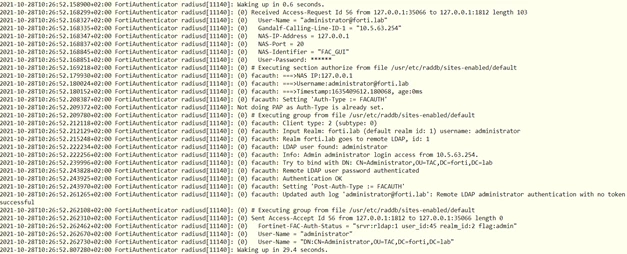
Using RADIUS debugging, it is possible to verify the authentication.