



Technical Tip: FortiAuthenticator HTTPS Management port
Description
This article provides information on the HTTPS management port of FortiAuthenticator. It expands on the System Access documentation.
Scope
FortiAuthenticator.
Solution
The HTTPS of FortiAuthenticator cannot be modified as of now (firmware version 6.6.2).
This impacts any service using HTTPS as well, including SAML, Portal services, and API.
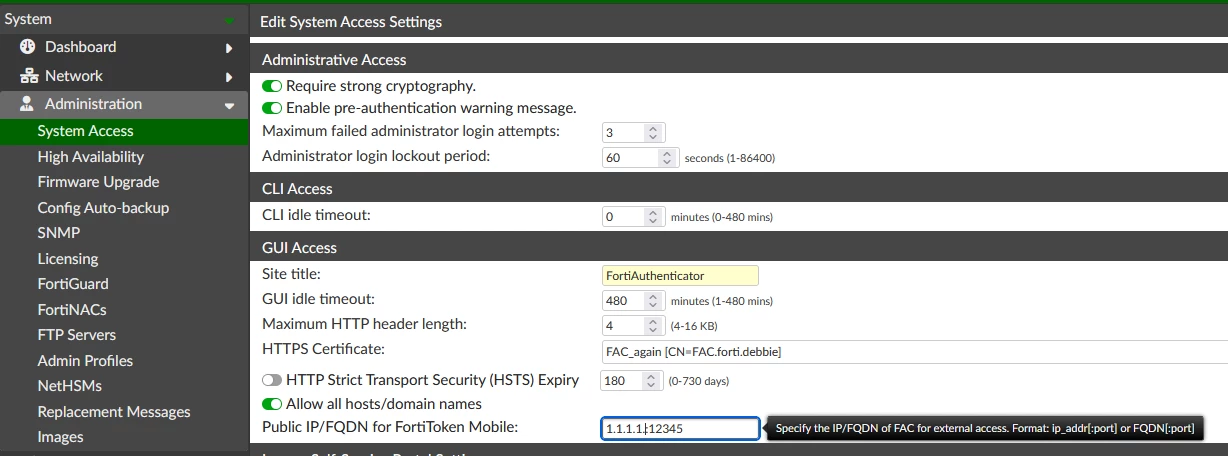
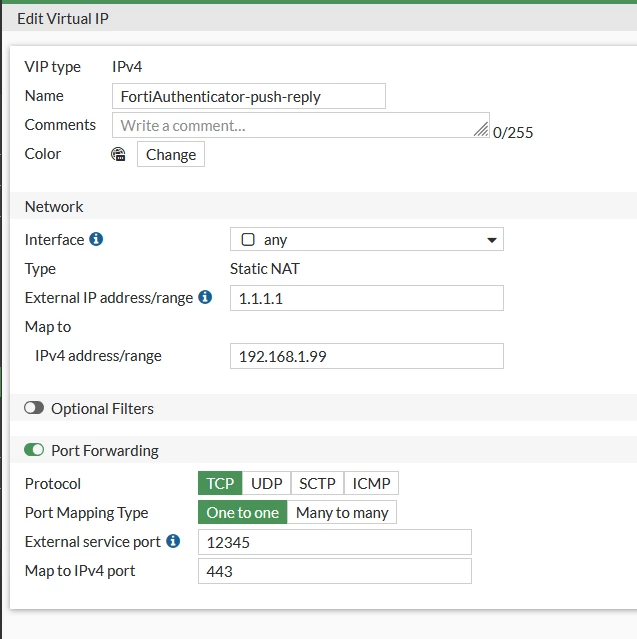
For outgoing push notifications, a public IP/hostname and port may be set. This should be mirrored on the gateway handling incoming traffic.
As an example (using FortiGate as gateway):
Public IP configured on FortiAuthenticator:
Corresponding Virtual IP on FortiGate:
- Go to System -> Administration -> System Access and under 'Public IP/FQDN for FortiToken Mobile' set <public_IP>:<port>.
- On the FortiGate (or other gateway), create a VIP/port-forwarding object to map incoming traffic from <public_IP>:<port> to <FortiAuthenticator>:443.
It is recommended to reboot the FortiAuthenticator once the above configuration has been done. This is to ensure that the web service restarts and can utilize the public IP setting.
In addition, if FortiGate serves as a gateway, FortiGate should have its local push service disabled so it does not mistakenly try to process the push responses itself instead of forwarding them to FortiAuthenticator.
Note:
If it is absolutely necessary to use a different HTTPS port to manage FortiAuthenticator, a feature request may be submitted to a Fortinet Sales representative.


