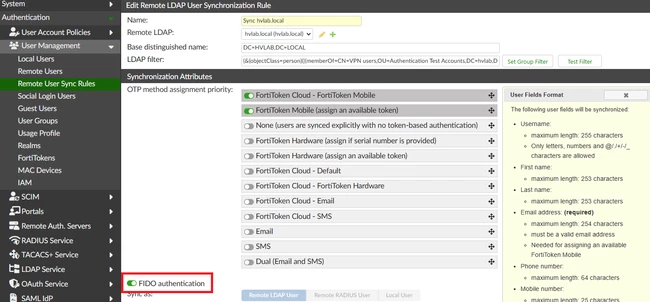
| Solution | This article assumes FortiAuthenticator is already configured as a SAML IdP or IdP Proxy. This is commonly used in combination with a Fortinet device, such as FortiGate, acting as a SAML Service Provider (SP). For example, see Configuring FortiAuthenticator as SAML IdP and FortiGate as SAML SP. FortiAuthenticator administrator steps: - Configure the user source to allow FIDO authentication. This can be defined on a Sync Rule or for the individual user.
On the Remote User Sync Rule:
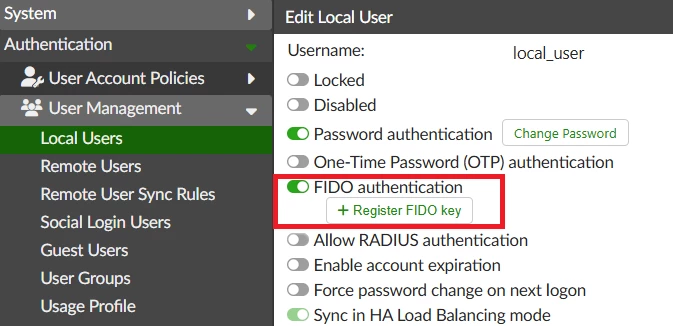
Individually, on the local or remote user:
 -
Create a portal allowing FIDO token registration: Go to Authentication -> Portals -> Portals -> Create New -> Post-Login Services -> Enable 'Token Registration' -> Enable 'Allow FIDO token registration'.
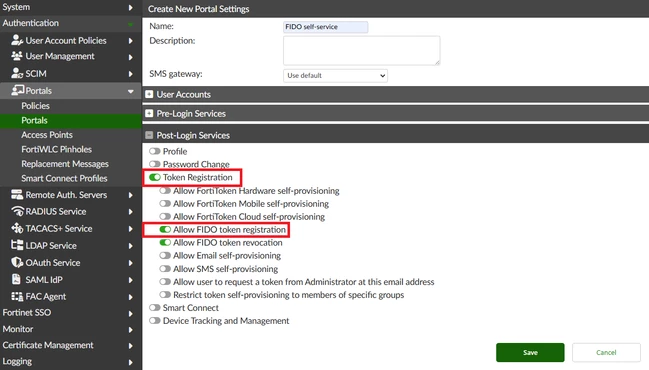
If users must be able to revoke the FIDO key if the physical security key is lost or stolen, enable 'Allow FIDO token revocation'.
-
Create a Self-service Portal Policy: Go to Authentication -> Portals -> Policies -> Self-Service Portal -> Select 'Create New'.
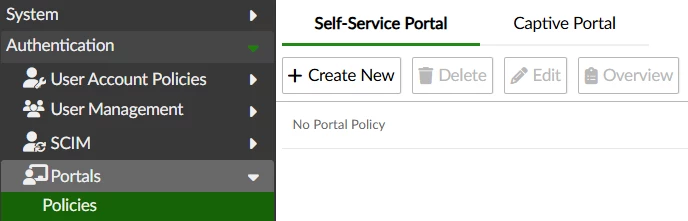
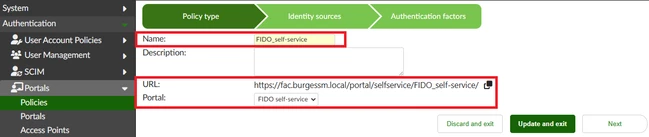
In Policy type, name the policy and record the generated URL. In the Portal field, assign the portal previously created in Step 2.
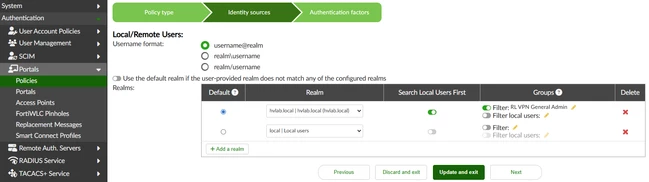
In Identity sources, configure one or more realms containing the users that require permission to self-manage FIDO keys.
In authentication factors, configure an authentication method.
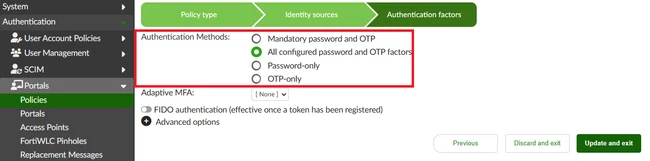
Note: If users must be able to revoke and generate a new token without administrator intervention in the event the security key is lost or reset, FIDO Authentication should be left disabled in Policy Authentication factors. If 'FIDO Authentication' is enabled in Policy Authentication factors, users with a registered FIDO token must present it when logging in to the self-service portal in the future.
-
Go to SAML IDP -> Service Providers -> Authentication -> enable FIDO as authentication method -> Select 'FIDO-only' or 'Password and FIDO'.
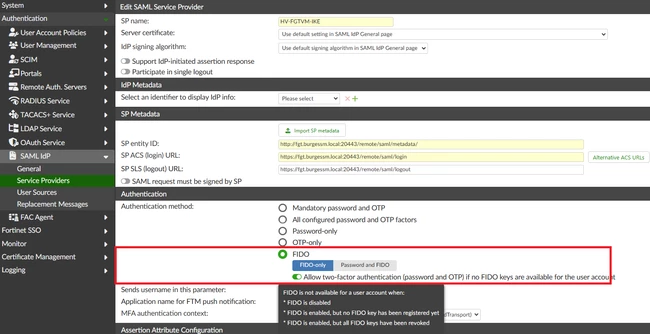
If FIDO-only is selected, users will only need their security key and security PIN to authenticate to the service. If 'Password and FIDO' is selected, users will also need to enter their existing password.
If the service is already in use by users without FIDO keys registered on FortiAuthenticator, enable 'Allow two-factor authentication (password and OTP) if no FIDO keys are available for the user account' to allow users with a password and OTP factor to continue to use the service before registering a FIDO key. If this option is disabled, users will only be able to authenticate to the service once a valid FIDO key is registered.
-
Educate users on the self-enrollment process below and provide the Portal Policy URL recorded in Step 3. Provide security keys to users if needed.
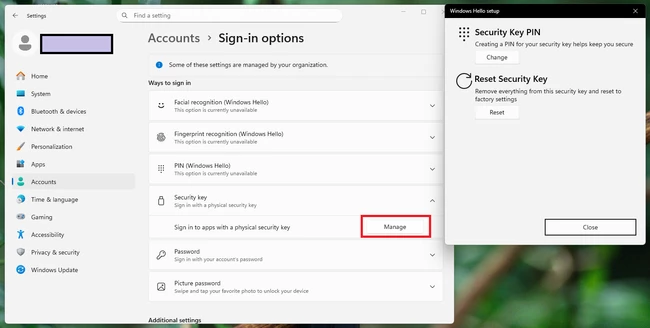
User Steps: - User performs initial setup of the security key, which is generally a USB or NFC-capable device. Typically initial setup consists of setting a security PIN for the device. If using FortiToken 410, see the 410 QuickStart Guide.
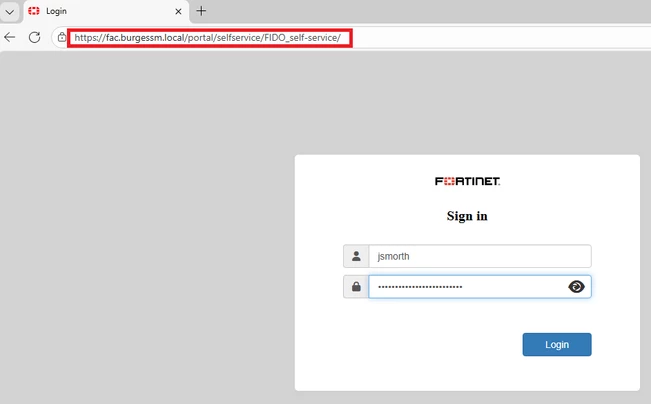
 - User enters the policy URL provided and enters their credentials.
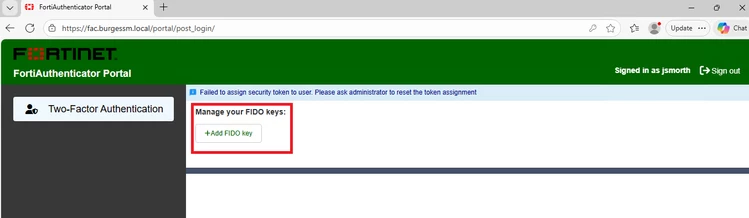
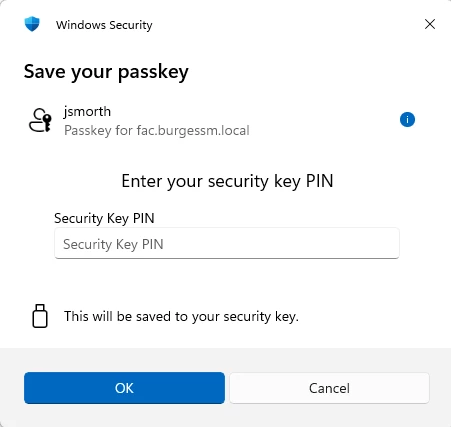
 - User creates a FIDO key and verifies their security key. The passkey proving ownership of the FIDO key is stored on the user's security key.
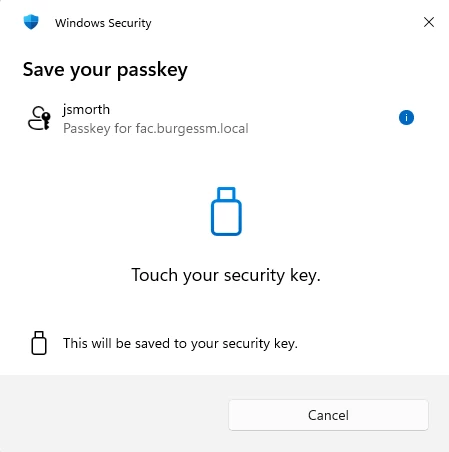 - The FIDO key can now be used as an authentication factor for services enabled by the administrator. In the example below, the user verifies the FIDO key by connecting to a FortiGate Remote IPsec dial-up gateway configured as a SAML service provider.
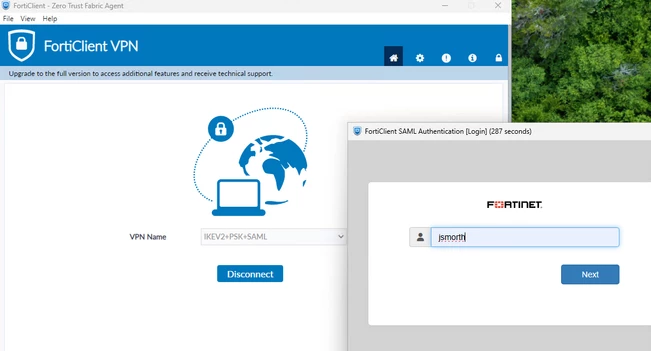
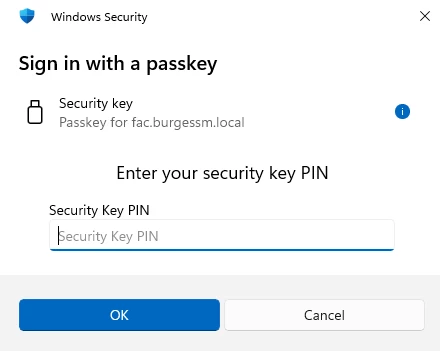
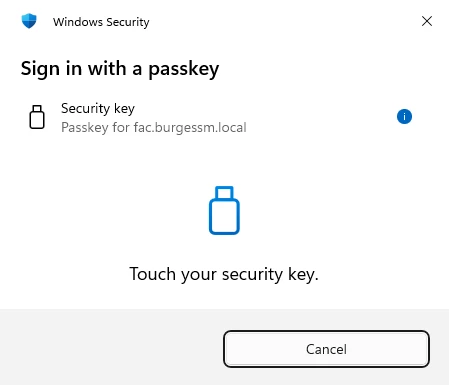
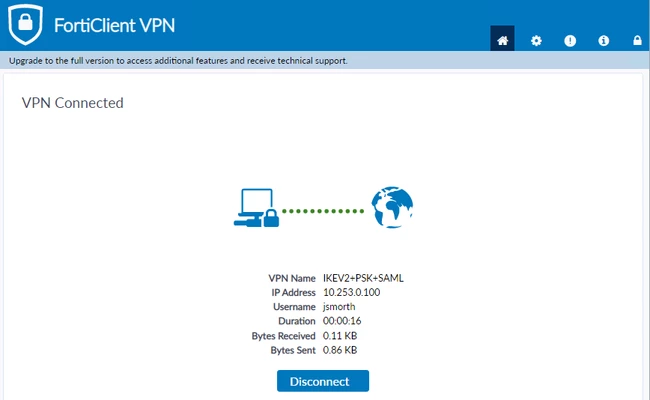 Note: From the service provider side, there is no difference in how the user authenticates. No changes were made to the FortiGate's configuration.
Administrator notes for FIDO: - 'FIDO' is a general term for the FIDO Alliance family of protocols, including the commonly used FIDO2. FortiAuthenticator supports FIDO2.
- FIDO is considered more secure than traditional username/password authentication. However, a password can be required in addition to a FIDO key if configured in FortiAuthenticator.
- While an administrator typically provides users with a USB security key or a smart card for use with FIDO protocols, it is possible for any user with a compatible security key to access the portal and self-register, as long as the FortiAuthenticator self-service portal and policy are enabled for the user.
- FortiAuthenticator administrators may add a FIDO key for an enabled user manually from the User Management page, without requiring a user Self-service Portal. Since this requires physical access to the security key and knowledge of its PIN, it is recommended that the user change the security key's PIN once it is provided to the user.
- Once FIDO is enabled in the SAML Service Provider configuration, users with only a password are not able to authenticate to the service provider. Users with a password and OTP factor are still able to authenticate if the 'Allow two-factor authentication (password and OTP) if no FIDO keys are available for the user account' option is enabled in FortiAuthenticator SAML Service Provider configuration.
Related article:
Technical Tip: activate FIDO authentication
|





