



Technical Tip: Considerations for using Local Users with 'Administrator' role as Remote Admin in RADIUS clients
Description
This article describes an authentication behavior observed when using local users with the Administrator role on FortiAuthenticator as a RADIUS server for remote administrator access on FortiGate.
Scope
FortiAuthenticator, FortiGate, and other RADIUS clients.
Solution
When configuring remote administrator authentication via RADIUS, the authentication method needs to be considered for the local FortiAuthenticator admin users.
FortiAuthenticator's local user can be used as a remote admin for Fortinet products' RADIUS client or any other third-party RADIUS clients.
In this example, FortiGate is acting as a RADIUS client. For FortiGate remote admin configuration, refer to the following KB articles:
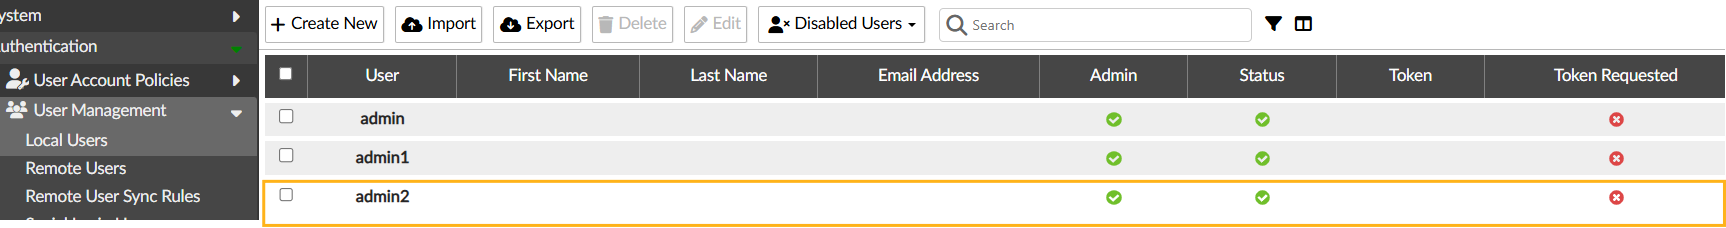
The remote admin for FortiGate is created in FortiAuthenticator with the "Administrator" role privilege.
Authentication failure error in FortiGate:
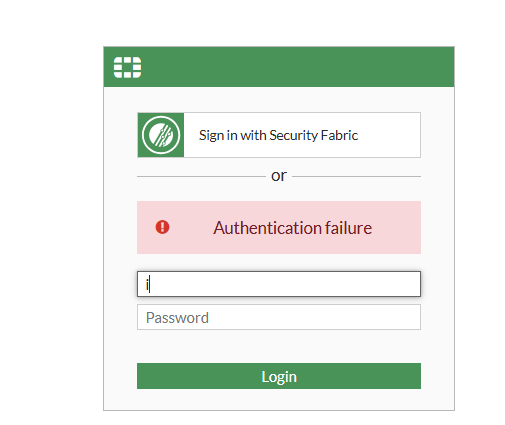
Upon receiving the error above while logging in as a Remote admin in FortiGate, RADIUS logs in FortiAuthenticator show the following error:
2026-05-05T11:32:34.893198+02:00 FAC radiusd[15598]: (6) facauth: Realm not specified, default goes to FAC local user
2026-05-05T11:32:34.894420+02:00 FAC radiusd[15598]: (6) facauth: Local user found: admin2
2026-05-05T11:32:34.894443+02:00 FAC radiusd[15598]: (6) facauth: Decided on [is_fido: false, two_factor: allow both, token_type: none]
2026-05-05T11:32:34.895355+02:00 FAC radiusd[15598]: (6) facauth: ERROR: ERROR: local user 'admin' auth require "User-Password" (pap)
2026-05-05T11:32:34.895377+02:00 FAC radiusd[15598]: (6) facauth: Authentication failed
2026-05-05T11:32:34.896081+02:00 FAC radiusd[15598]: (6) facauth: update_fac_authlog:165 nas_str = 10.1.10.10~172.21.98.9.
2026-05-05T11:32:34.896135+02:00 FAC radiusd[15598]: (6) facauth: Updated auth log 'admin2' for attempt from 192.168.2.254~172.21.98.9: Local administrator authentication from 172.21.98.9 (mschap) with no token failed:invalid user parameter
Local users with the Administrator (or Sponsor) role may fail to authenticate if only MSCHAPv2 is enabled.
This occurs because Administrator-role accounts use irreversible password hashing (bcrypt), which does not allow retrieval of the original password required for MSCHAPv2 challenge-response authentication.
In contrast, a remote administrator login using a FortiAuthenticator local user with the 'Administrator' role succeeds when PAP is used, as the password is validated directly during the RADIUS exchange.
Additionally, local users with the 'User' role use reversible encryption (AES256), which allows all supported authentication methods to function correctly; therefore, these users can be used for remote administrator authentication on RADIUS clients.
Successful RADIUS logs where the local user 'ic01' is with the 'User' role in FortiAuthenticator and using MSCHAPv2 as authentication method:
2026-05-05T10:53:24.863801+02:00 FAC radiusd[15598]: (4) Received Access-Request Id 2 from 10.1.10.10:13272 o 10.1.10.11:1812 length 209
2026-05-05T10:53:24.863823+02:00 FAC radiusd[15598]: (4)   MS-CHAP2-Response = 0x6d00930e220f33f4c4a3ed7d6a8e3f25fa720000000000000000ad6647c61fe5b9e95641bceb927a99bd945b9e6a414d5c61
2026-05-05T10:53:24.863828+02:00 FAC radiusd[15598]: (4)   MS-CHAP-Challenge = 0xf37523d7e91619c0aee80e76c1390019
2026-05-05T10:53:24.863833+02:00 FAC radiusd[15598]: (4)   User-Name = "ic01"
2026-05-05T10:53:24.863838+02:00 FAC radiusd[15598]: (4)   NAS-Identifier = "bentley-kvm15"
2026-05-05T10:53:24.863847+02:00 FAC radiusd[15598]: (4)   Framed-IP-Address = 172.21.98.9
2026-05-05T10:53:24.863863+02:00 FAC radiusd[15598]: (4)   NAS-Port-Type = Virtual
2026-05-05T10:53:24.863868+02:00 FAC radiusd[15598]: (4)   Calling-Station-Id = "172.21.98.9"
2026-05-05T10:53:24.863872+02:00 FAC radiusd[15598]: (4)   Acct-Session-Id = "000013900b007001"
2026-05-05T10:53:24.863876+02:00 FAC radiusd[15598]: (4)   Connect-Info = "admin-login"
2026-05-05T10:53:24.863880+02:00 FAC radiusd[15598]: (4)   Fortinet-Vdom-Name = "root"
2026-05-05T10:53:24.863976+02:00 FAC radiusd[15598]: (4)   Message-Authenticator = 0x8490bb4bb8d19269206efc2a17d0bf52
2026-05-05T10:53:24.864007+02:00 FAC radiusd[15598]: (4) # Executing section authorize from file /usr/etc/raddb/sites-enabled/default
2026-05-05T10:53:24.864157+02:00 FAC radiusd[15598]: (4) facauth: ===>NAS IP:10.1.10.10
2026-05-05T10:53:24.864165+02:00 FAC radiusd[15598]: (4) facauth: ===>Username:ic01
2026-05-05T10:53:24.864173+02:00 FAC radiusd[15598]: (4) facauth: ===>Timestamp:1777971204.863313, age:0ms
2026-05-05T10:53:24.864824+02:00 FAC radiusd[15598]: (4) facauth: Found authclient from preloaded authclients list for 10.1.10.10: FGT radius client (10.1.10.10)

2026-05-05T10:53:24.867765+02:00 FAC radiusd[15598]: (4) facauth: Local user found: ic01

2026-05-05T10:53:24.869324+02:00 FAC radiusd[15598]: (4) facauth: Updated auth log 'ic01' for attempt from 10.1.10.11~172.21.98.9: Local user authentication from 172.21.98.9 (mschap) with no token successful

2026-05-05T10:53:24.869390+02:00 FAC radiusd[15598]: (4) Sent Access-Accept Id 2 from 10.1.10.11:1812 to 10.1.10.10:13272 length 227
In any scenario, if the option 'Enhanced cryptography' for local users is enabled, PAP becomes the only supported authentication method for all FortiAuthenticator local users.
For more information regarding 'Enhanced cryptography', refer to the following KB article:
Since PAP is considered insecure and unsuitable for this deployment, RADSEC can be configured as a secure alternative.
Related documents:

