This example uses an OpenLDAP server with the base distinguished name dc=labtest,dc=com. The directory contains an organizational unit for users, an organizational unit for groups, three test users, a test group, and a read-only account for LDAP queries.
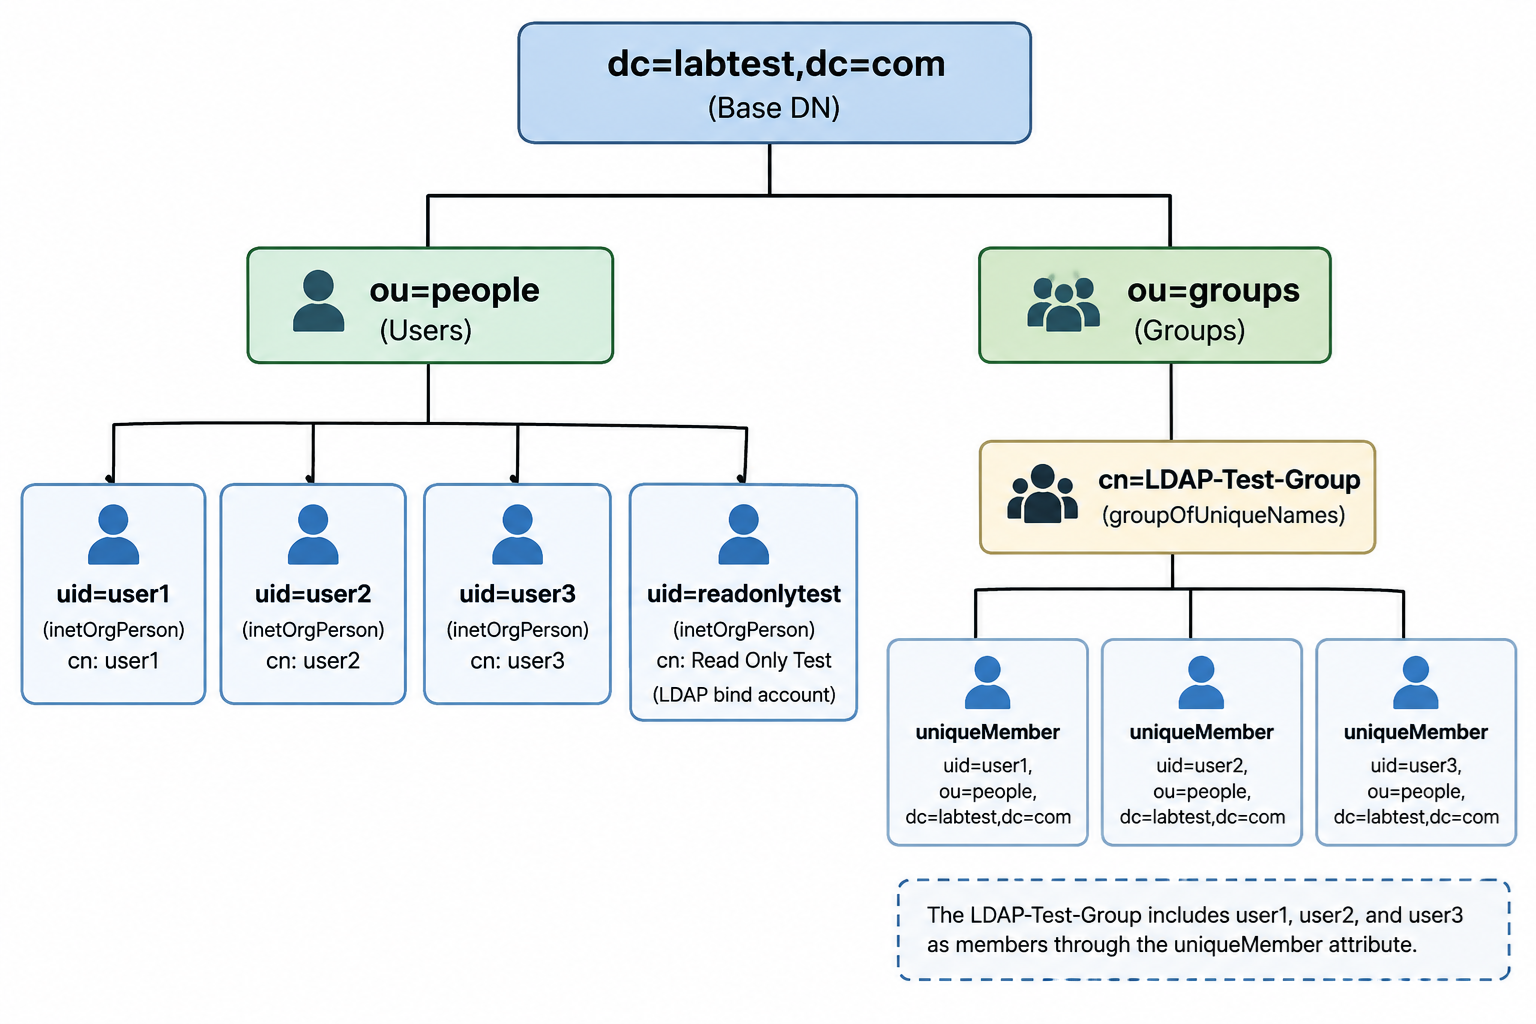
The example uses the following LDAP attributes:
User object class: inetOrgPerson
Username attribute: uid
Group object class: groupOfUniqueNames
Group membership attribute: uniqueMember
Note: OpenLDAP does not emulate Microsoft Active Directory. This lab is intended for testing generic LDAP operations and attributes such as LDAP bind, search, object classes, user attributes, groups, membership attributes, and LDAP filters.
Install OpenLDAP.
Install the OpenLDAP server and LDAP utilities on Ubuntu:
sudo apt update
sudo apt install slapd ldap-utils
During installation, configure the LDAP administrator password when prompted.
If required, reconfigure slapd:
sudo dpkg-reconfigure slapd
For this example, configure the LDAP directory with the following base DN:
dc=labtest,dc=com
The LDAP administrator DN is:
cn=admin,dc=labtest,dc=com
Verify that the LDAP directory can be queried:
ldapsearch -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -b "dc=labtest,dc=com"
A successful query returns:
result: 0 Success
Create the LDAP organizational units.
Create an LDIF file:
vi /tmp/base.ldif
Add the following entries:
dn: ou=people,dc=labtest,dc=com
objectClass: organizationalUnit
ou: people

dn: ou=groups,dc=labtest,dc=com
objectClass: organizationalUnit
ou: groups
Import the entries:
ldapadd -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -f /tmp/base.ldif
Create the test LDAP users.
Create the user LDIF file:
vi /tmp/users.ldif
Add the following entries:
dn: uid=user1,ou=people,dc=labtest,dc=com
objectClass: inetOrgPerson
uid: user1
cn: user1
sn: user1

dn: uid=user2,ou=people,dc=labtest,dc=com
objectClass: inetOrgPerson
uid: user2
cn: user2
sn: user2

dn: uid=user3,ou=people,dc=labtest,dc=com
objectClass: inetOrgPerson
uid: user3
cn: user3
sn: user3
Import the users:
ldapadd -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -f /tmp/users.ldif
Verify the users:
ldapsearch -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -b "ou=people,dc=labtest,dc=com" \
  "(objectClass=inetOrgPerson)" \
  dn uid objectClass
The search should return the three individual LDAP entries:
dn: uid=user1,ou=people,dc=labtest,dc=com
uid: user1

dn: uid=user2,ou=people,dc=labtest,dc=com
uid: user2

dn: uid=user3,ou=people,dc=labtest,dc=com
uid: user3
Create an LDAP group.
Create the group LDIF file:
vi /tmp/group.ldif
Add the following entries:
dn: cn=LDAP-Test-Group,ou=groups,dc=labtest,dc=com
objectClass: groupOfUniqueNames
cn: LDAP-Test-Group
uniqueMember: uid=user1,ou=people,dc=labtest,dc=com
uniqueMember: uid=user2,ou=people,dc=labtest,dc=com
uniqueMember: uid=user3,ou=people,dc=labtest,dc=com
Import the group:
ldapadd -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -f /tmp/group.ldif
Verify the group and its membership:
ldapsearch -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -b "ou=groups,dc=labtest,dc=com" \
  "(objectClass=groupOfUniqueNames)" \
  dn objectClass cn uniqueMember
The output should contain one group entry with multiple uniqueMember values:
dn: cn=LDAP-Test-Group,ou=groups,dc=labtest,dc=com
objectClass: groupOfUniqueNames
cn: LDAP-Test-Group
uniqueMember: uid=user1,ou=people,dc=labtest,dc=com
uniqueMember: uid=user2,ou=people,dc=labtest,dc=com
uniqueMember: uid=user3,ou=people,dc=labtest,dc=com
Create a read-only LDAP account.
Using the LDAP administrator account for FortiAuthenticator is not required when only directory search access is needed.
First, verify the existing OpenLDAP access configuration:
sudo ldapsearch -Y EXTERNAL -H ldapi:/// \
  -b "olcDatabase={1}mdb,cn=config" \
  olcAccess
For example, the following ACL permits directory entries to be read while restricting access to the userPassword attribute:
olcAccess: {0}to attrs=userPassword by self write by anonymous auth by * none
olcAccess: {1}to attrs=shadowLastChange by self write by * read
olcAccess: {2}to * by * read
Generate a password hash for the bind account:
slappasswd
Create the LDIF file:
vi /tmp/readonlytest.ldif
Add the following entry and replace <generated-password-hash> with the value generated by slappasswd:
dn: uid=readonlytest,ou=people,dc=labtest,dc=com
objectClass: top
objectClass: person
objectClass: organizationalPerson
objectClass: inetOrgPerson
uid: readonlytest
cn: Read Only Test
sn: Test
userPassword: <generated-password-hash>
Import the account:
ldapadd -x \
  -H ldap://127.0.0.1:389 \
  -D "cn=admin,dc=labtest,dc=com" \
  -W \
  -f /tmp/readonlytest.ldif
Verify that the account can authenticate:
ldapwhoami -x \
  -H ldap://127.0.0.1:389 \
  -D "uid=readonlytest,ou=people,dc=labtest,dc=com" \
  -W
A successful bind returns:
dn:uid=readonlytest,ou=people,dc=labtest,dc=com
Verify that the account can query the test group:
ldapsearch -x \
  -H ldap://127.0.0.1:389 \
  -D "uid=readonlytest,ou=people,dc=labtest,dc=com" \
  -W \
  -b "ou=groups,dc=labtest,dc=com" \
  "(cn=LDAP-Test-Group)" \
  dn cn objectClass uniqueMember
Verify that the account can also query the individual users:
ldapsearch -x \
  -H ldap://127.0.0.1:389 \
  -D "uid=readonlytest,ou=people,dc=labtest,dc=com" \
  -W \
  -b "ou=people,dc=labtest,dc=com" \
  "(|(uid=user1)(uid=user2)(uid=user3))" \
  dn uid cn objectClass
The query should return three separate user entries.
Configure the LDAP server on FortiAuthenticator.
On FortiAuthenticator, go to Authentication -> Remote Auth. Servers -> LDAP and select Create New.
Configure the LDAP server using the applicable server IP address and the following example parameters:
Port: 389
Base distinguished name: dc=labtest,dc=com
Bind type: Regular
Username: uid=readonlytest,ou=people,dc=labtest,dc=com
Server type: OpenLDAP/GSuite
User object class: inetOrgPerson
Username attribute: uid
Group object class: groupOfUniqueNames
Enter the password configured for the readonlytest account.
Save the LDAP server configuration and use Browse or Import Users to verify that FortiAuthenticator can query the LDAP directory.
The individual LDAP users should be available as separate remote users:
user1
user2
user3
Important: The OpenLDAP access control configuration can differ between installations. Verify the existing olcAccess rules before relying on an LDAP account as a read-only account or modifying LDAP access controls.
The object classes and attributes used in this example are intended for lab testing. Production LDAP directories may use different schemas, user object classes, username attributes, group object classes, and membership attributes.
OpenLDAP does not replace Microsoft Active Directory when reproducing AD-specific behavior such as Kerberos authentication, Active Directory-specific attributes, nested group processing, or other Microsoft Active Directory functionality.
| 




