



Technical Tip: Allow two different groups with or without two factor authentication
Description
Users with and without 2 factor authentication enabled have to be able to authenticate using respective users.
This article describes how to allow this feature.
Solution
Network diagram.
FAC IP: 10.40.6.105
FGT IP: 10.40.4.123
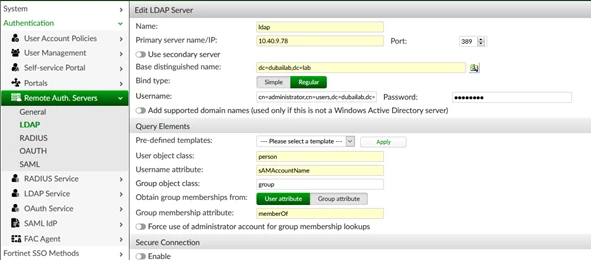
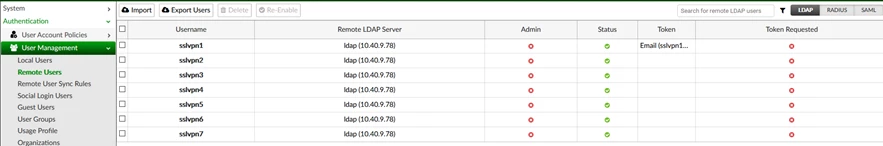
On FortiAuthenticator configured the LDAP server and imported the users.
Users with and without 2 factor authentication enabled have to be able to authenticate using respective users.
This article describes how to allow this feature.
Solution
Network diagram.
FAC IP: 10.40.6.105
FGT IP: 10.40.4.123
On FortiAuthenticator configured the LDAP server and imported the users.
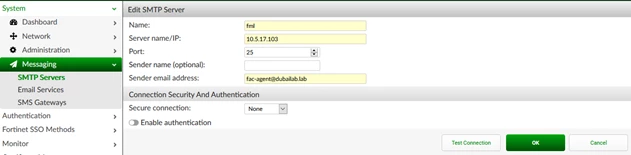
SMTP server configuration.
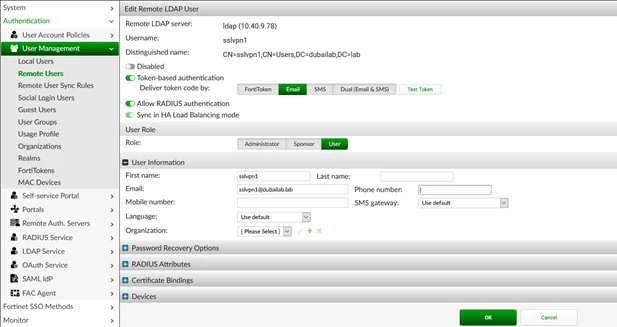
Enabling 2 factor authentication (email) for 'sslvpn1'.
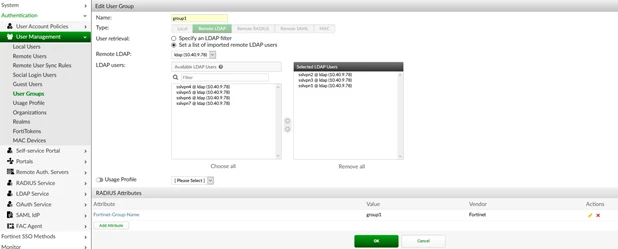
Configure Group1.
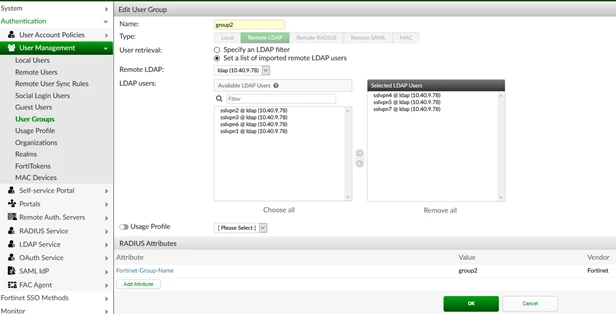
Group2.
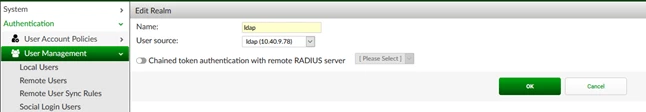
Configuring LDAP realm.
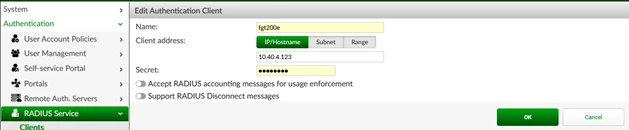
Configuring Radius client.
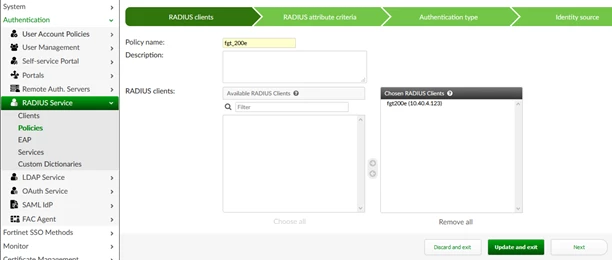
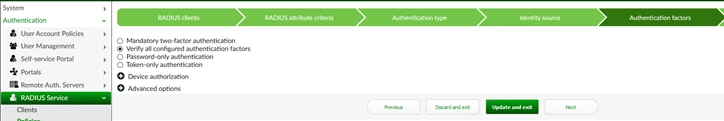
Configuring Radius policies.
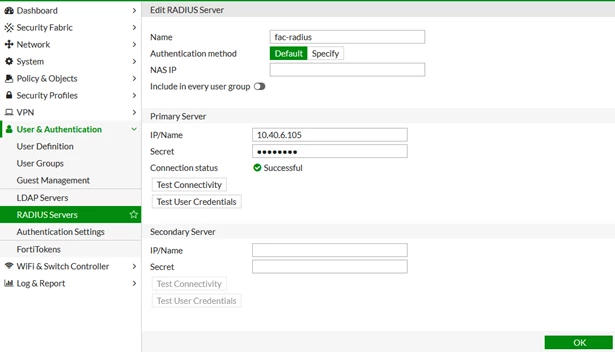
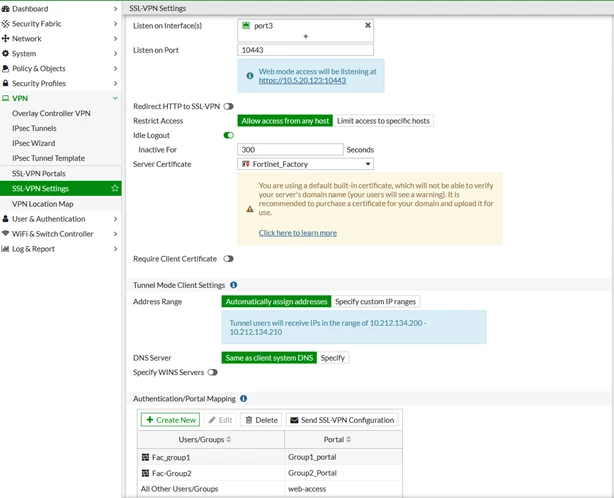
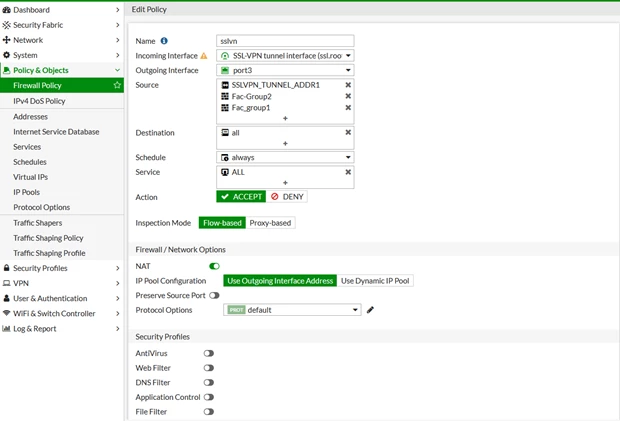
SSLVPN configuration on FortiGate.
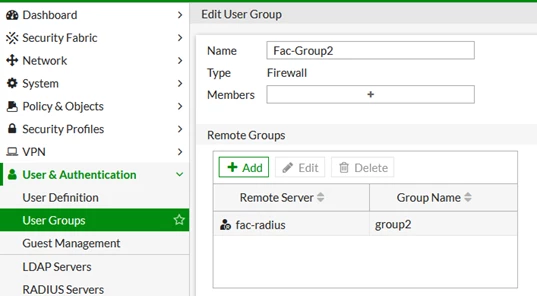
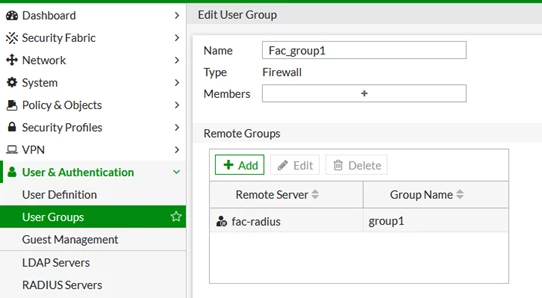
Configuring local groups.
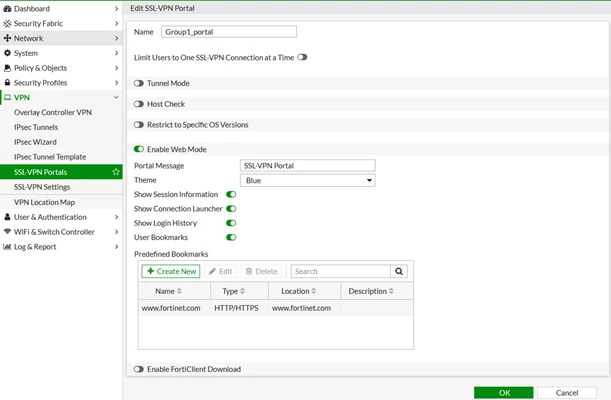
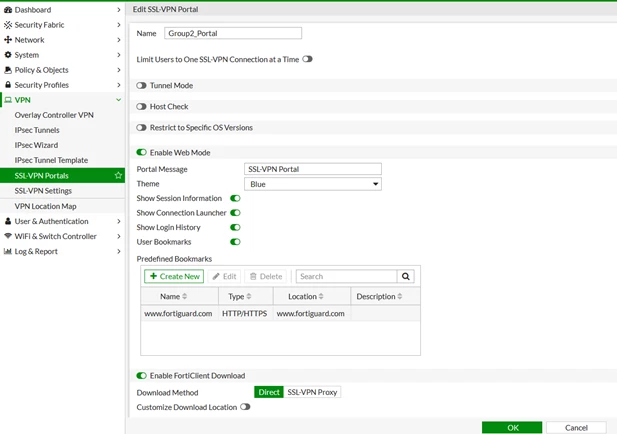
Configuring SSLVPN portals.
Configuring SSLVPN settings.
Configuring SSLVPN policies.
Troubleshooting.
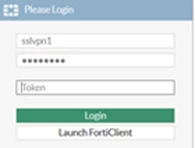
Login from SSLVPN1 where email 2 factor authentication is enabled.
Login from SSLVPN1 where email 2 factor authentication is enabled.
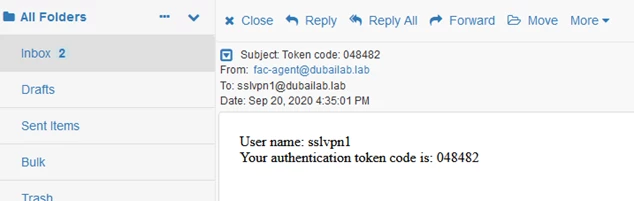
Email FortiToken.

