shafiq23
Staff & Editor
Staff & Editor
July 17, 2025

Technical Tip: How to verify Custom Rule parameter filter

  • July 17, 2025
  • 0 replies
  • 287 views
Description This article describes how to verify the custom rule parameter filter configuration.
Scope FortiAppSec Cloud WAF.
Solution

Configuration:
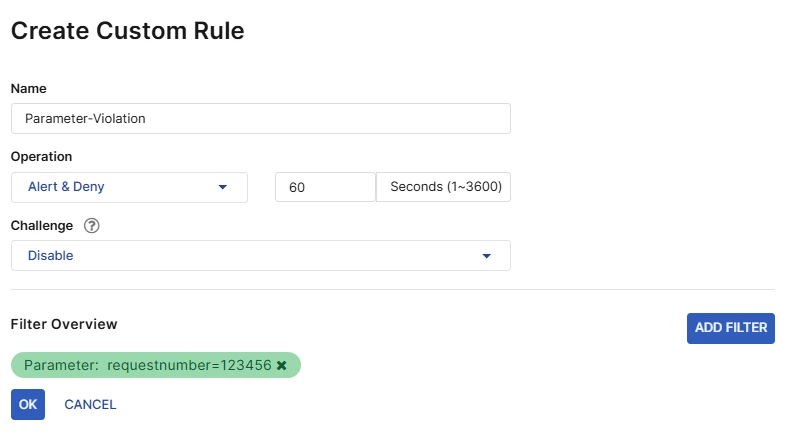
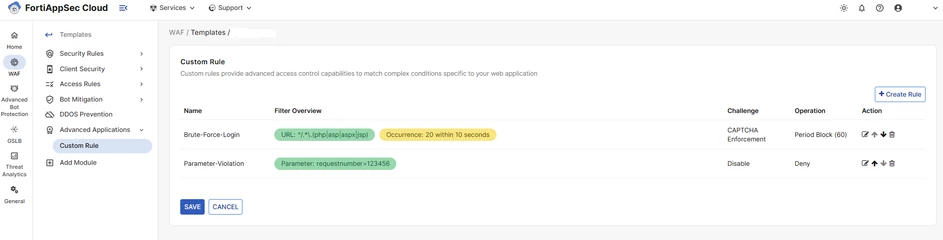
To block specific HTTP URL parameter names and values.


1.png


Note:

The parameter name and value can be either plain and/or regular expression.


2.png


Steps to verify:

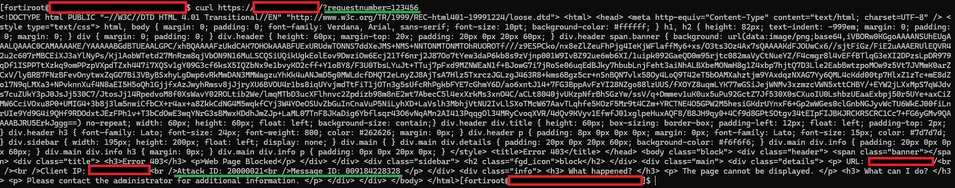
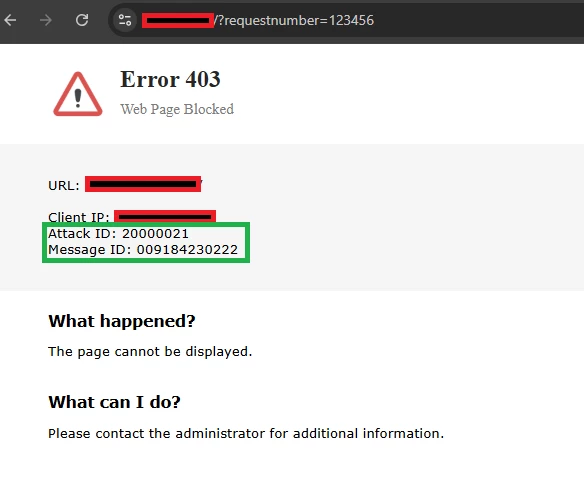
  1. Use curl or a browser to include the blocked parameter name or value in the HTTP request.


3.png


4.png


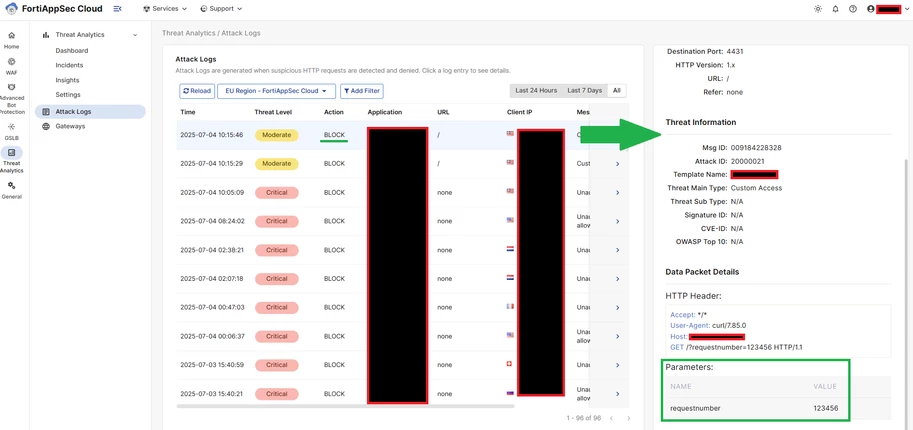
  1. The attack log will be generated in the FortiAppSec Cloud portal under Threat Analytics -> Attack Log.


5.png


Related article:
Custom Rule 

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!