



Technical Tip: Prevent false positive FAKE-AP-ON-AIR log entries on FortiGate devices
Description
This article describes how to whitelist authorized access points to prevent false positive FAKE-AP-ON-AIR log entries on FortiGate devices. It provides a step-by-step guide on how to classify rogue APs as accepted, allowing users to prevent false positive log entries.
Scope
FortiGate, FortiAP.
Solution
To whitelist authorized access points and prevent false positive FAKE-AP-ON-AIR log entries, follow these steps:
- Go to Dashboard -> WiFi -> Rogue APs.
- In the Rogue APs table, find the AP that needs to be whitelisted and select the State column.
- Select 'Accepted' from the dropdown menu.
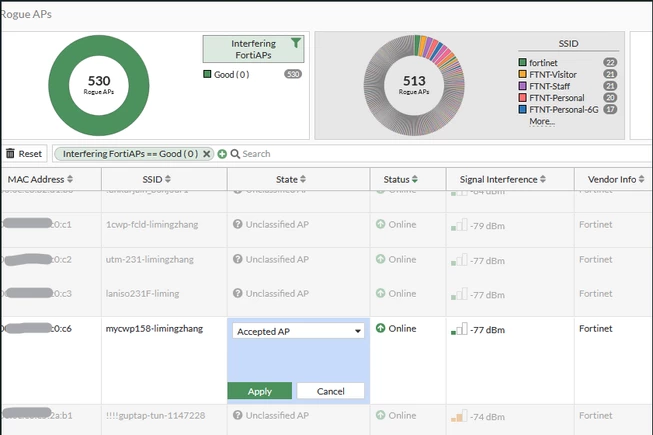
- To verify the MAC address of the access point, go to the AP CLI and run the vcfg command. Example:
------------------------------VAP Configuration 5----------------------------
Radio Id 2 WLAN Id 2 wpa3sae-transition ADMIN_DOWN(INTF_DOWN) init_done 0.0.0.0/0.0.0.0 unknown (-1)
vlanid=0, intf=wlan22, vap=0x1357f604, bssid=94:f3:92:ea:19:da
11ax high-efficiency=enabled target-wake-time=enabled
- Check the BSSID of each SSID being broadcast to confirm the MAC address.
Note: Make sure to only whitelist authorized access points to prevent potential security risks.

