



Technical Tip: How to assign the AC (FortiGate interface) IP statically
| Description | This article describes how to assign the AC (FortiGate interface) IP statically. |
| Scope | FortiAP 6.x, 7.x. |
| Solution | The FortiAP might be losing keepalives with FortiGate at random times, there could be multiple reasons behind that. However, one of the possible reasons could be due to the L2 congestion or switch side congestion which leads to keepalives miss between FortiGate and FortiAP.
The possible last failure reason that appears on FortiGate when FortiAP misses keepalive is 'Control message: maximal re-transmission limit reached' and 'ECHO REQ is missing'.
To avoid the network side or L2 congestion, have the AC (FortiGate) IP assigned statically on the FortiAP so that instead of trying all discovery types, it will directly check for the AC IP and get connected quickly.
The steps to do it from FortiAP CLI is as below:
# cfg -a AC_DISCOVERY_TYPE=1 # cfg -a AC_IPADDR_1= 192.168.6.1 <- FortiGate interface IP.
# cfg -s <- to verify if the config is correct or not. # cfg -c <- to save the config on FortiAP, the FortiAP will disconnect and rediscover the FortiAP after the change.
The screenshots on how to do it from FortiAP GUI are as below:
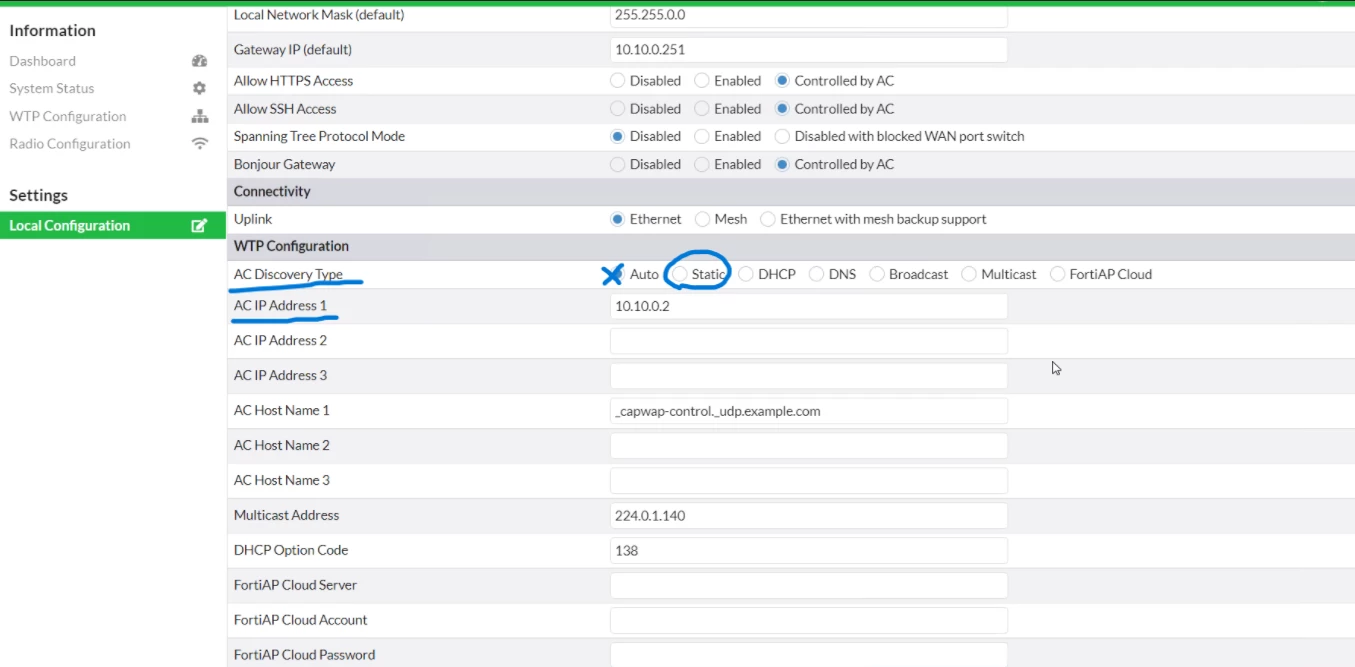
Select 'save' to save the config to take effect.
Once the FortiAP is online on FortiGate, it is possible to follow the below documents to configure the FortiAP accordingly based on the requirement:
|

