



Troubleshooting Tip: 'Self-Harm and Risky Term' and 'Bad Term or Phrase' showing single value instead of full sentence on the report
Description
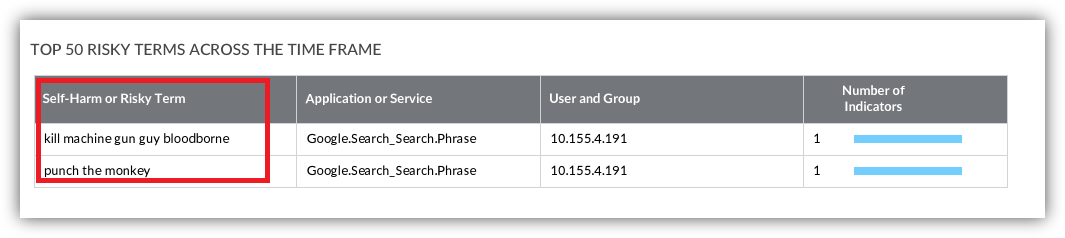
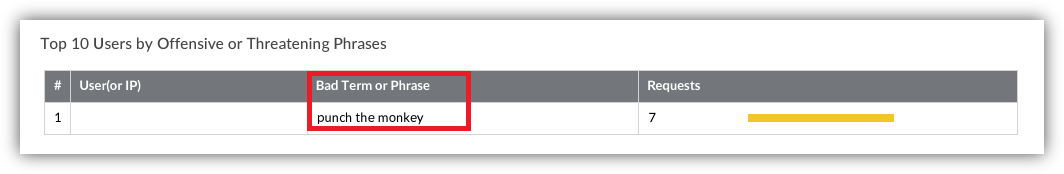
This article describes why the default report, which is the Cyber-Bullying Indicators Report and Self-Harm and Risk Indicators Report, shows the value of Bad Term or Phrase and Self-Harm and Risky Term as a single value instead of a full sentence.
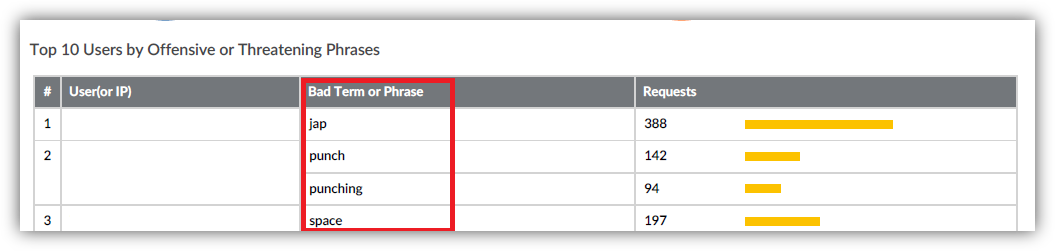
Cyber-Bullying Indicators Report
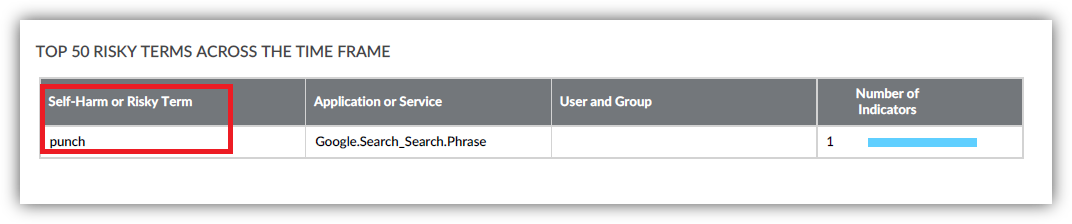
Self-Harm and Risk Indicators Report
Scope
FortiAnalyzer and FortiGate.
Solution
Identify on each default report which dataset value is being used to generate the output.
For the first example on Self-Harm and Risk Indicators Report, identify which chart is used under Reports -> Report Definitions -> Search 'Self-Harm and Risk Indicators Report' -> Select it -> Editor -> Go on "TOP 10 USERS WITH RISKY TERMS OR PHRASES" -> Select it -> Under Chart -> Self-Harm Risky Term User Drilldown.
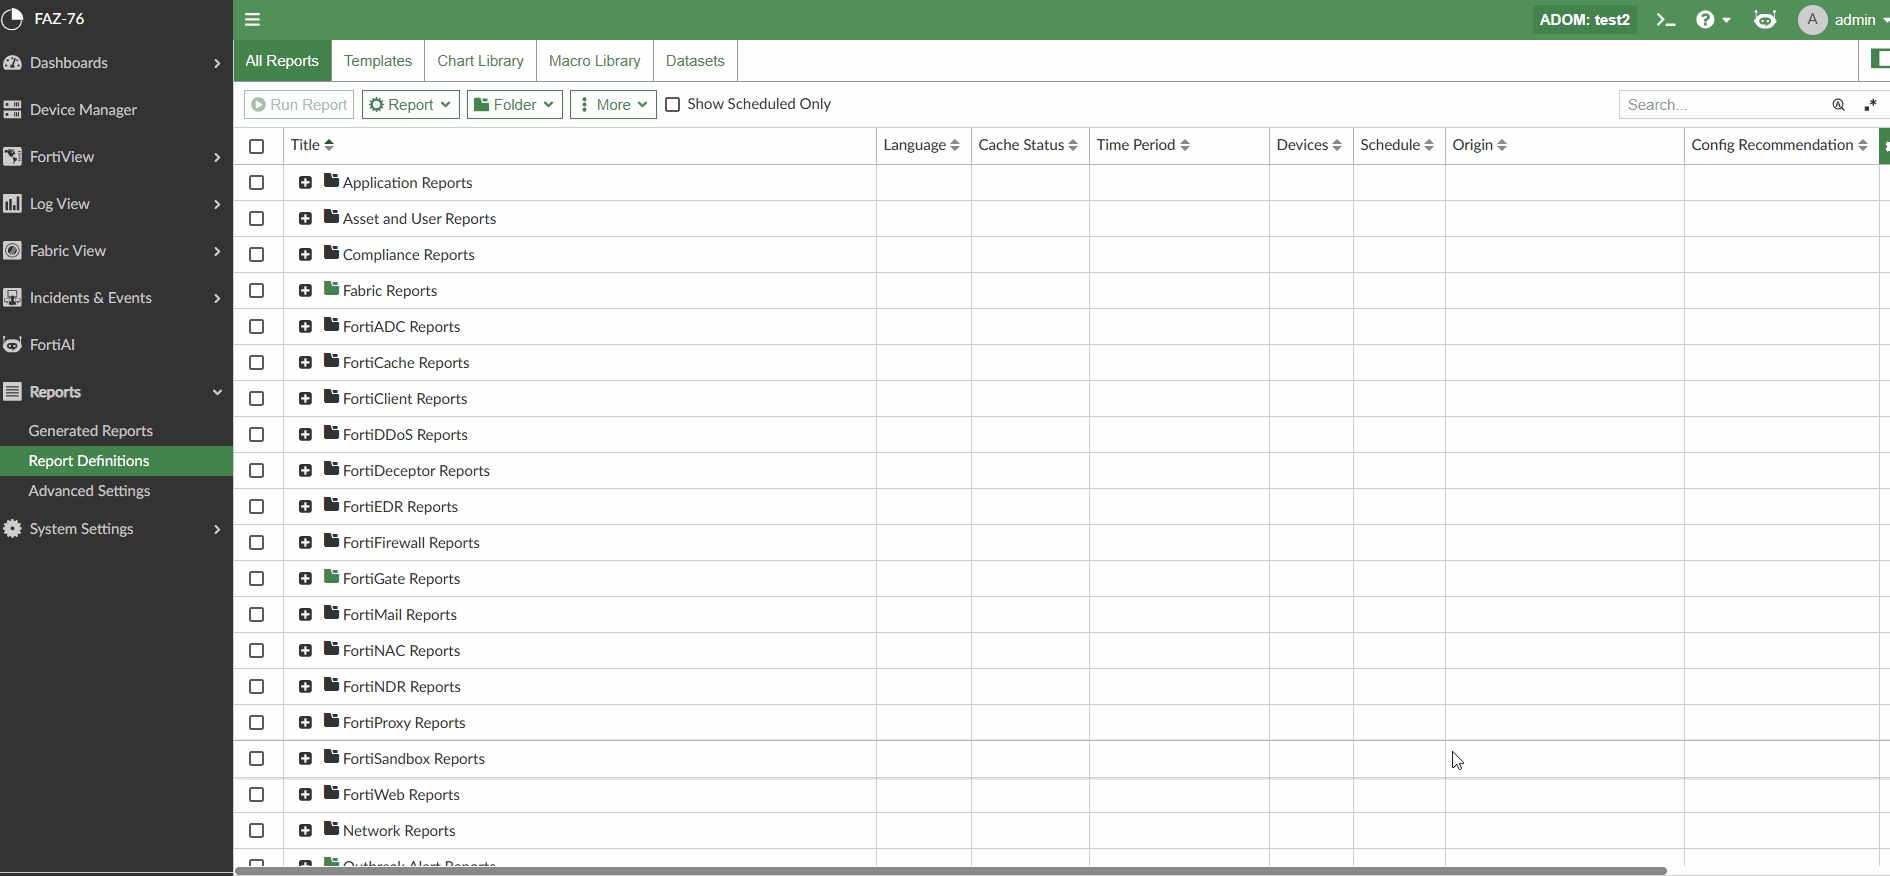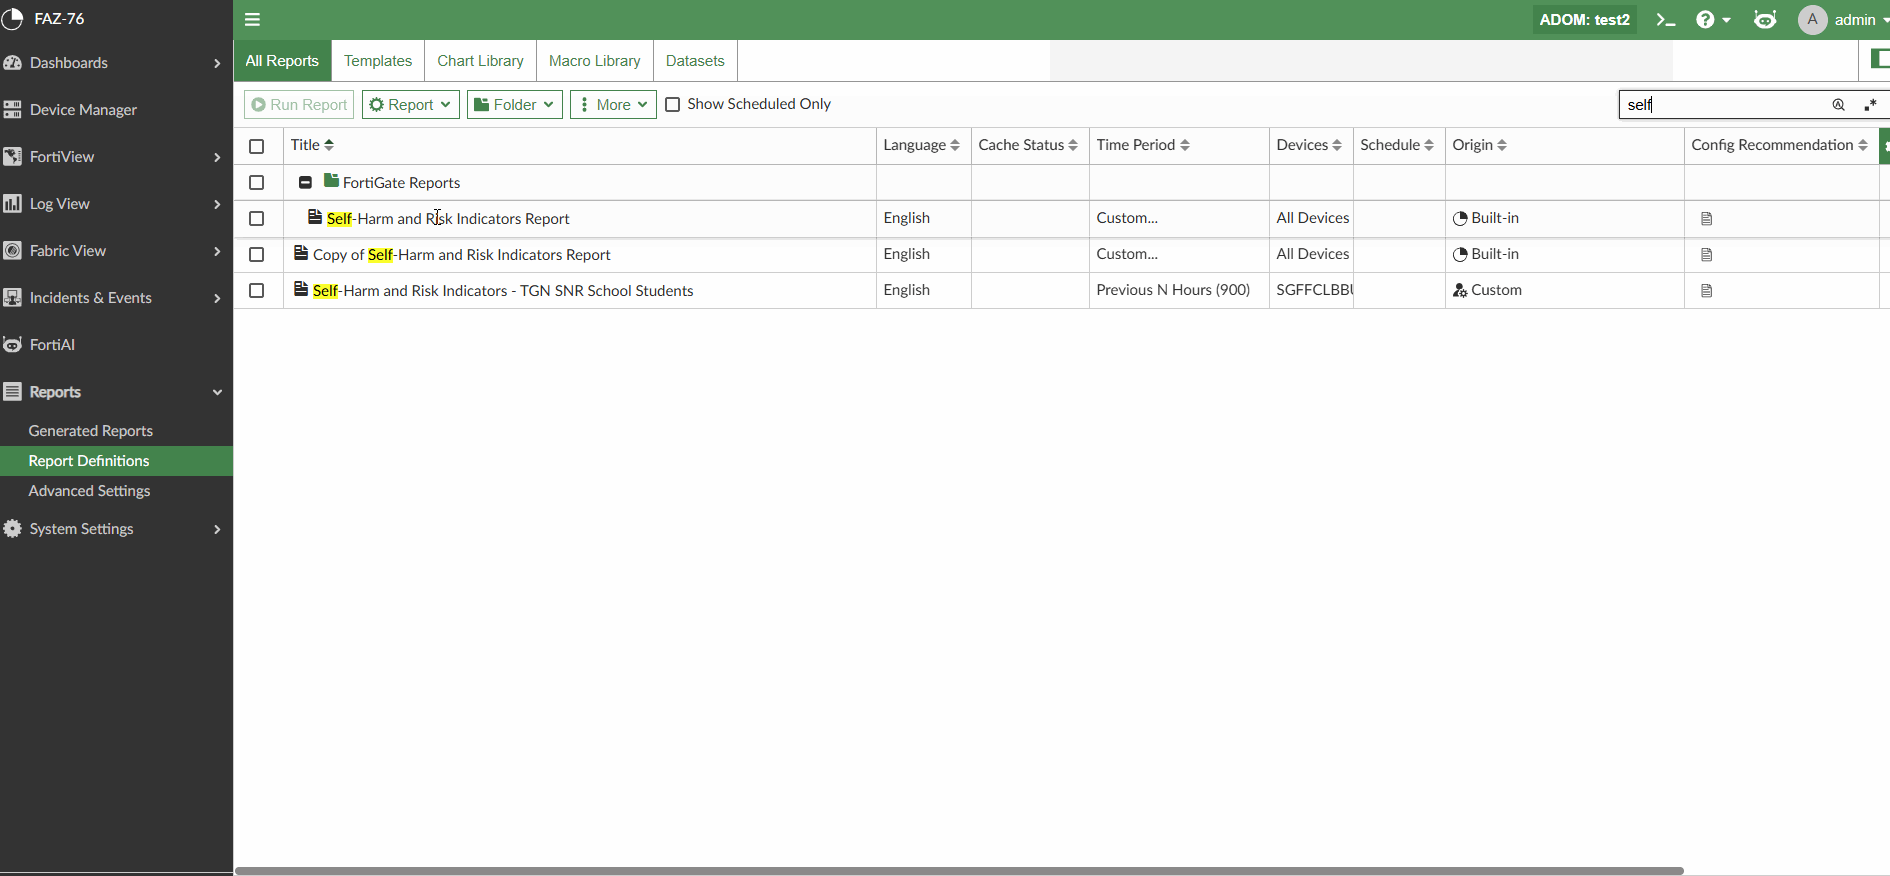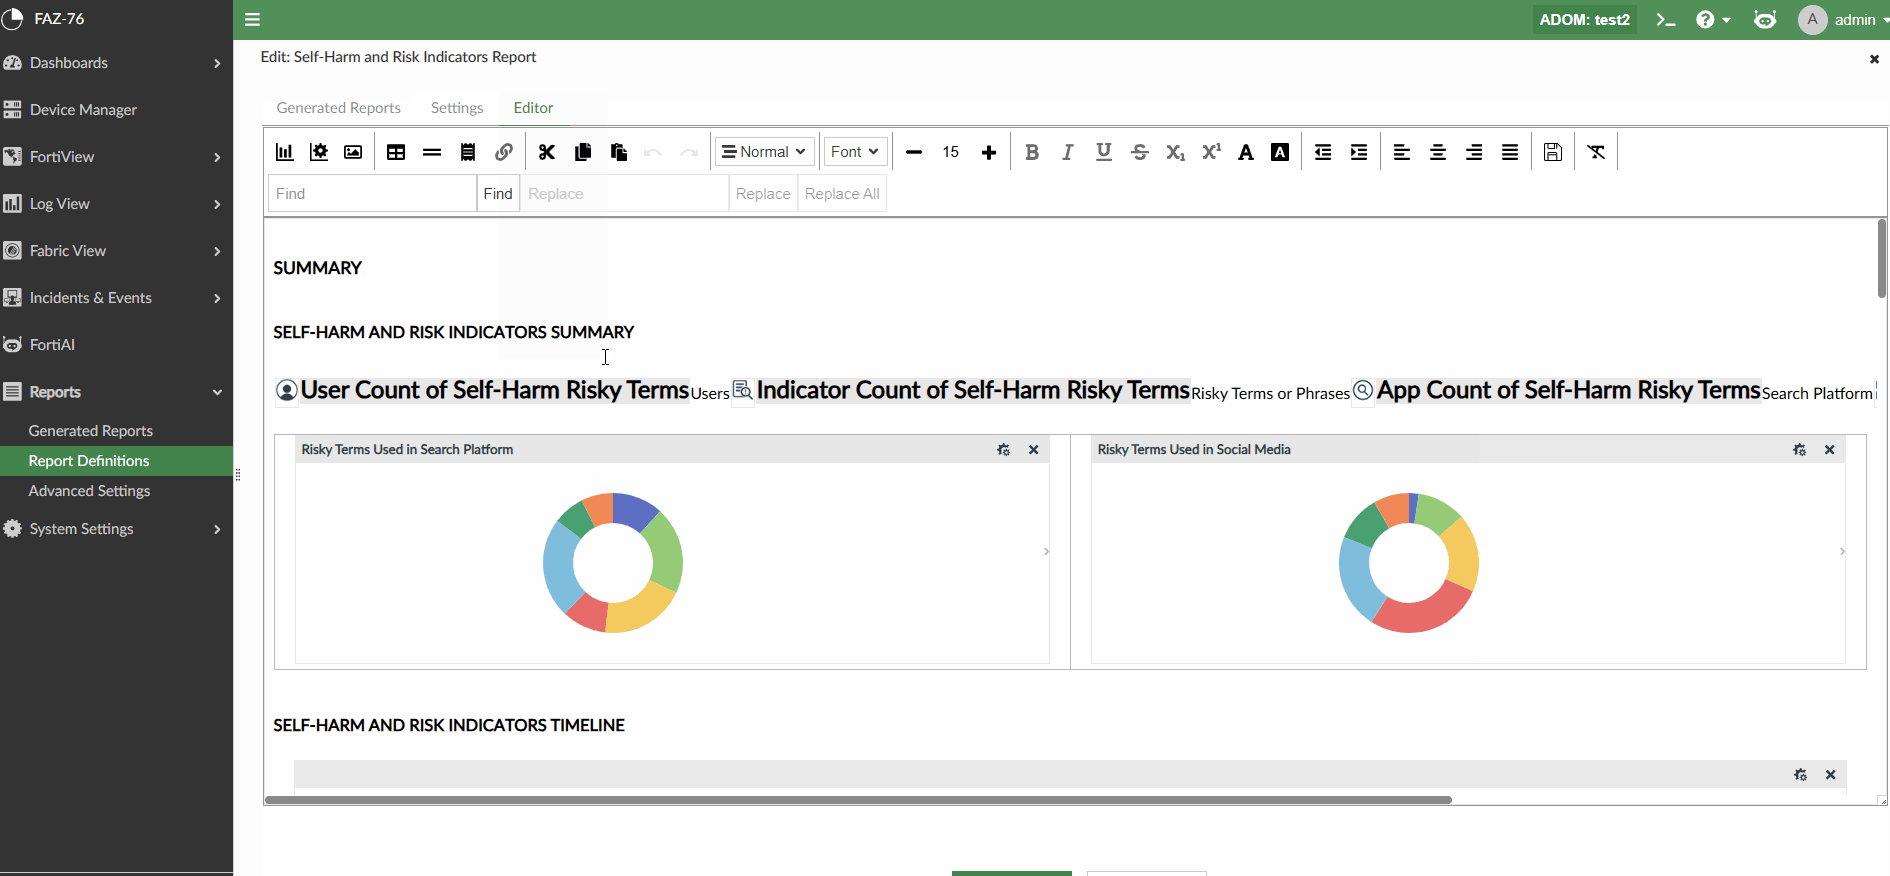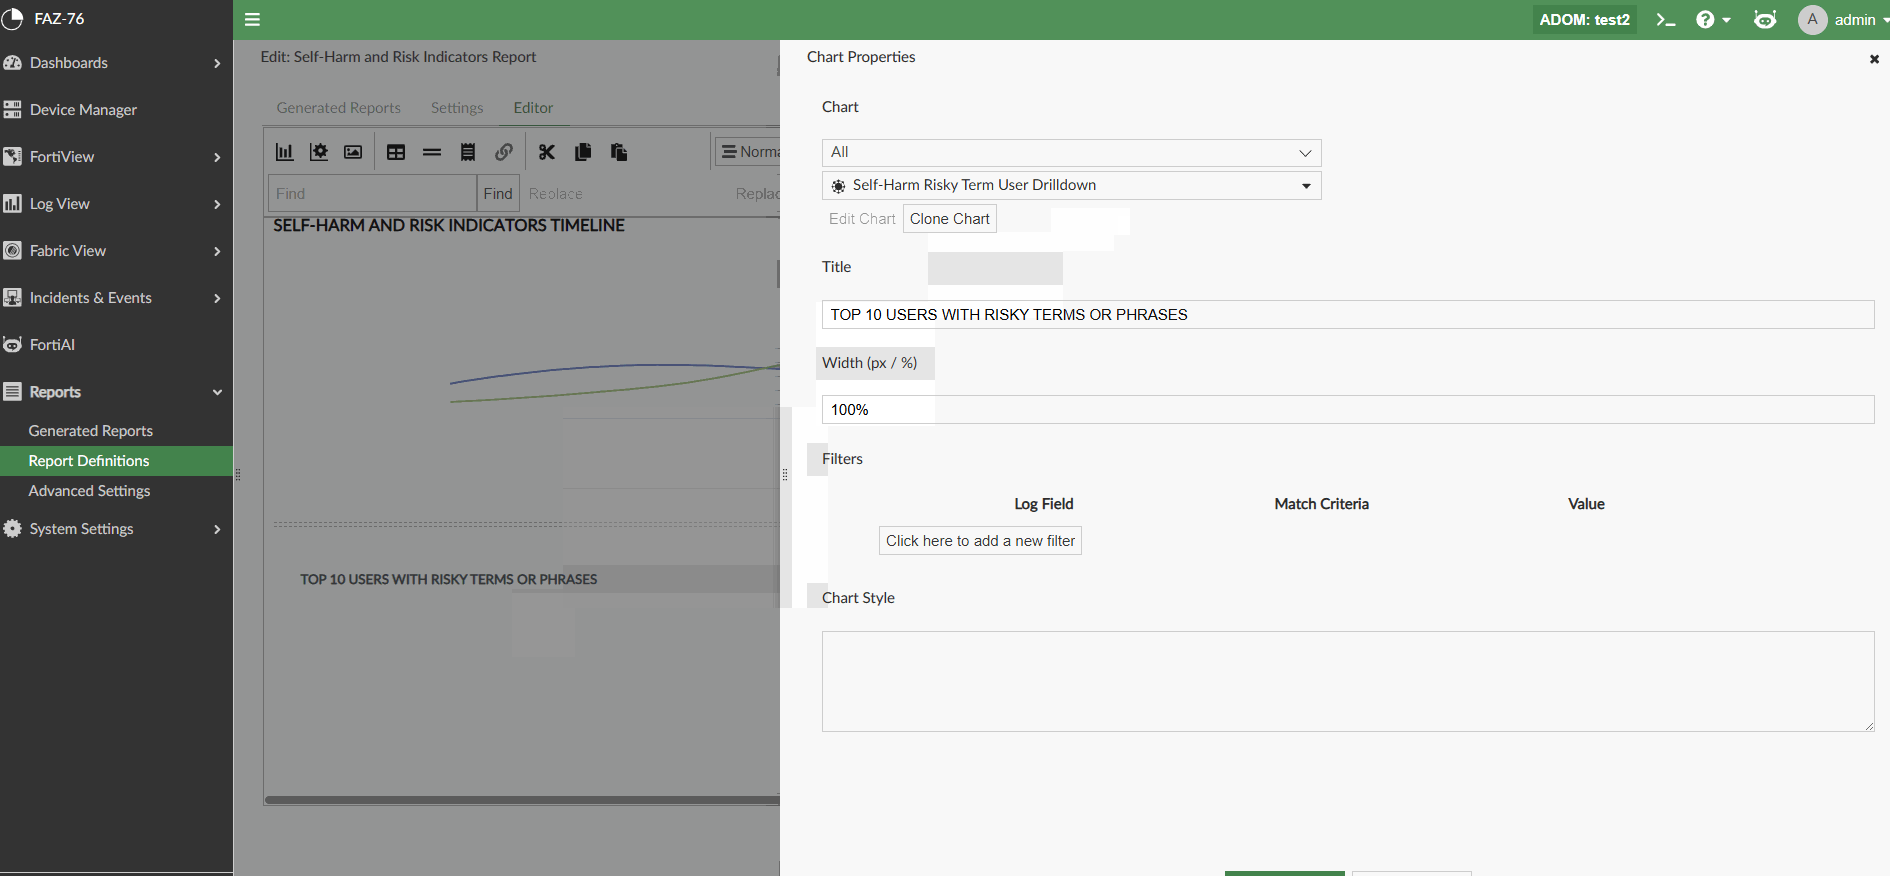
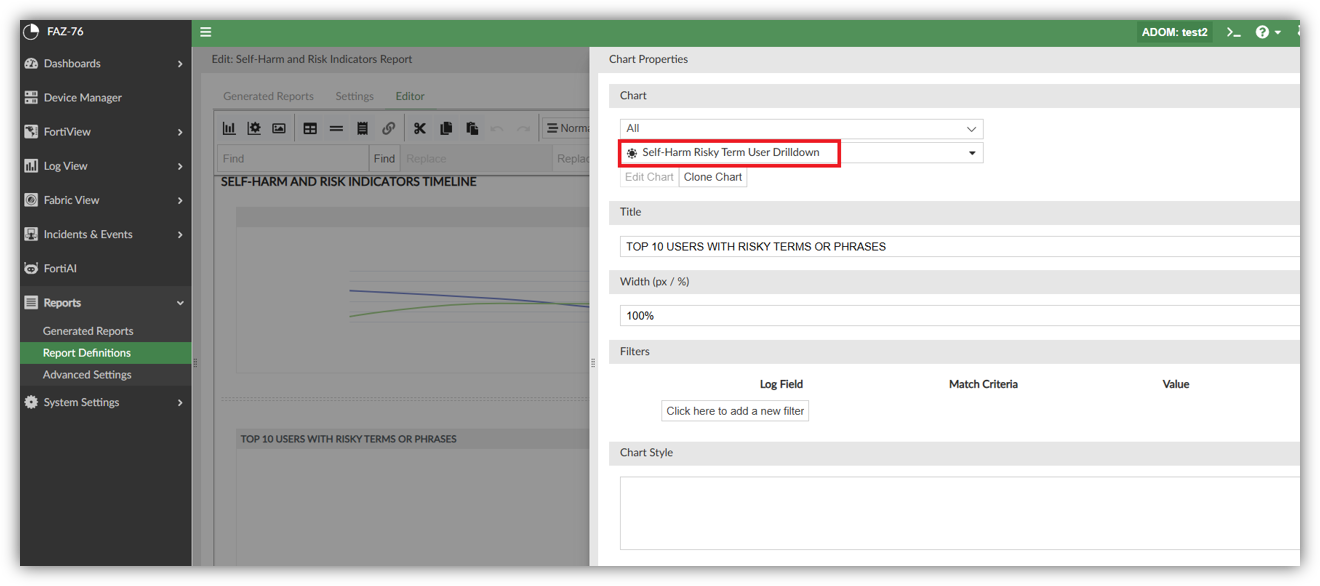
Once identified on which chart is used, proceed to check which dataset is used, under Reports -> Report Definitions -> Chart Library -> Search 'Self-Harm Risky Term User Drilldown' -> Select it -> Dataset -> Self-harm-Chat-Search-And-Message-Logging-By-User.
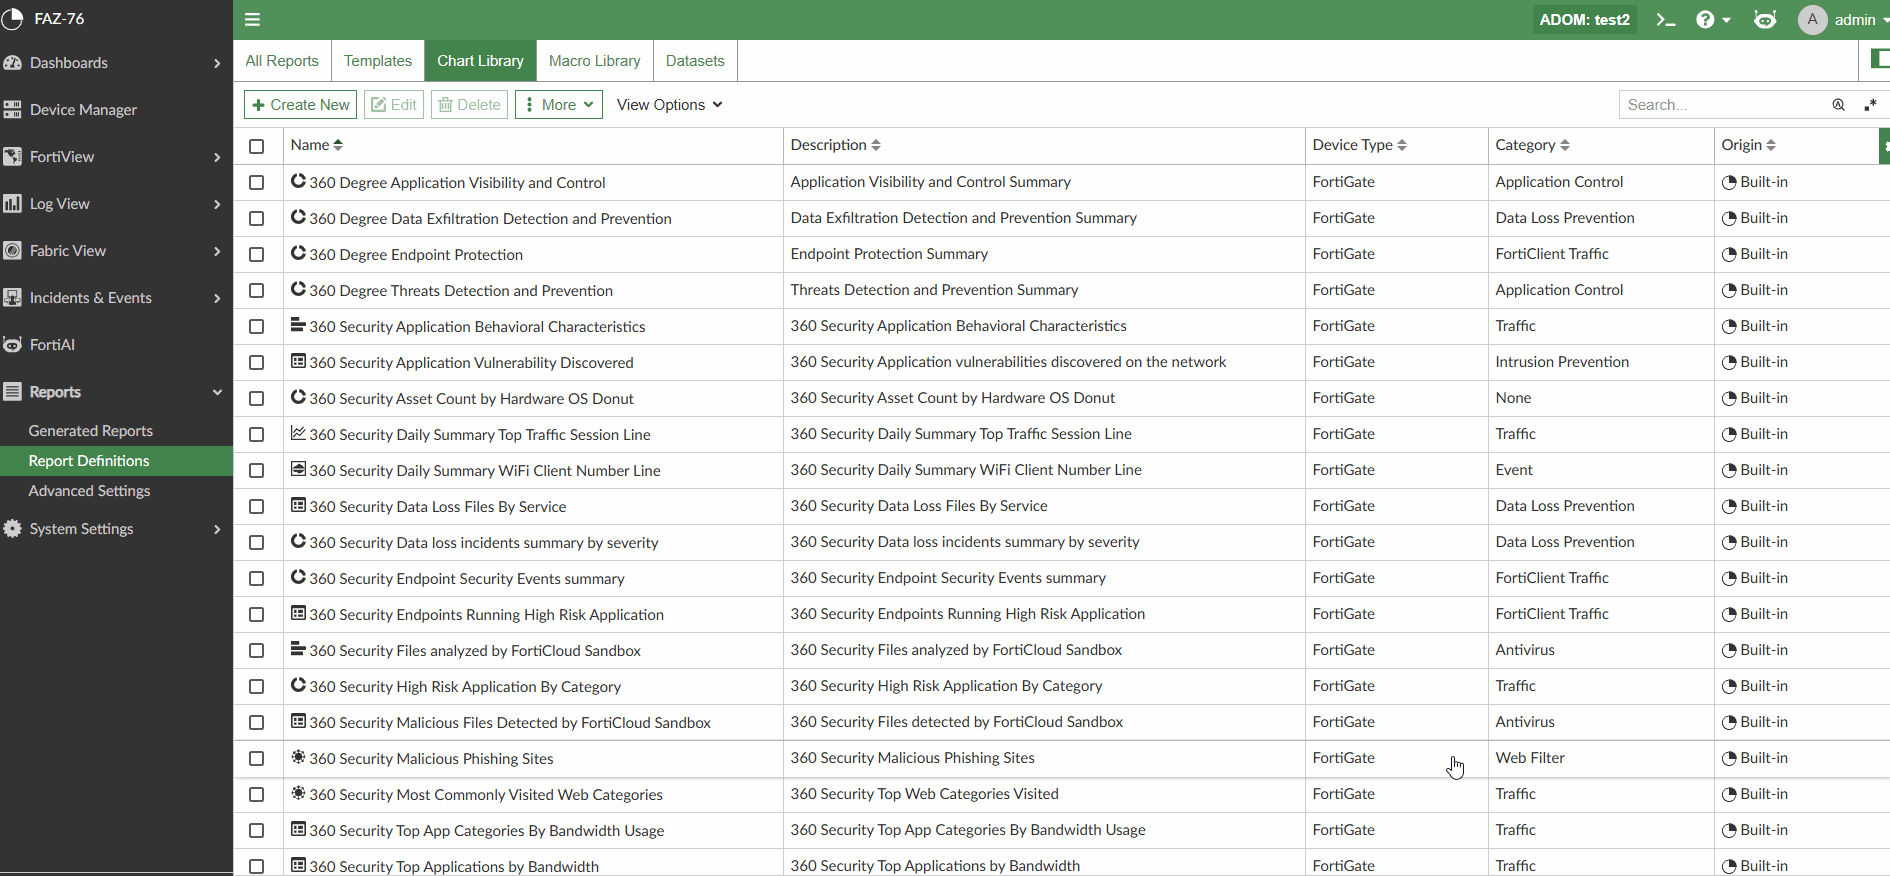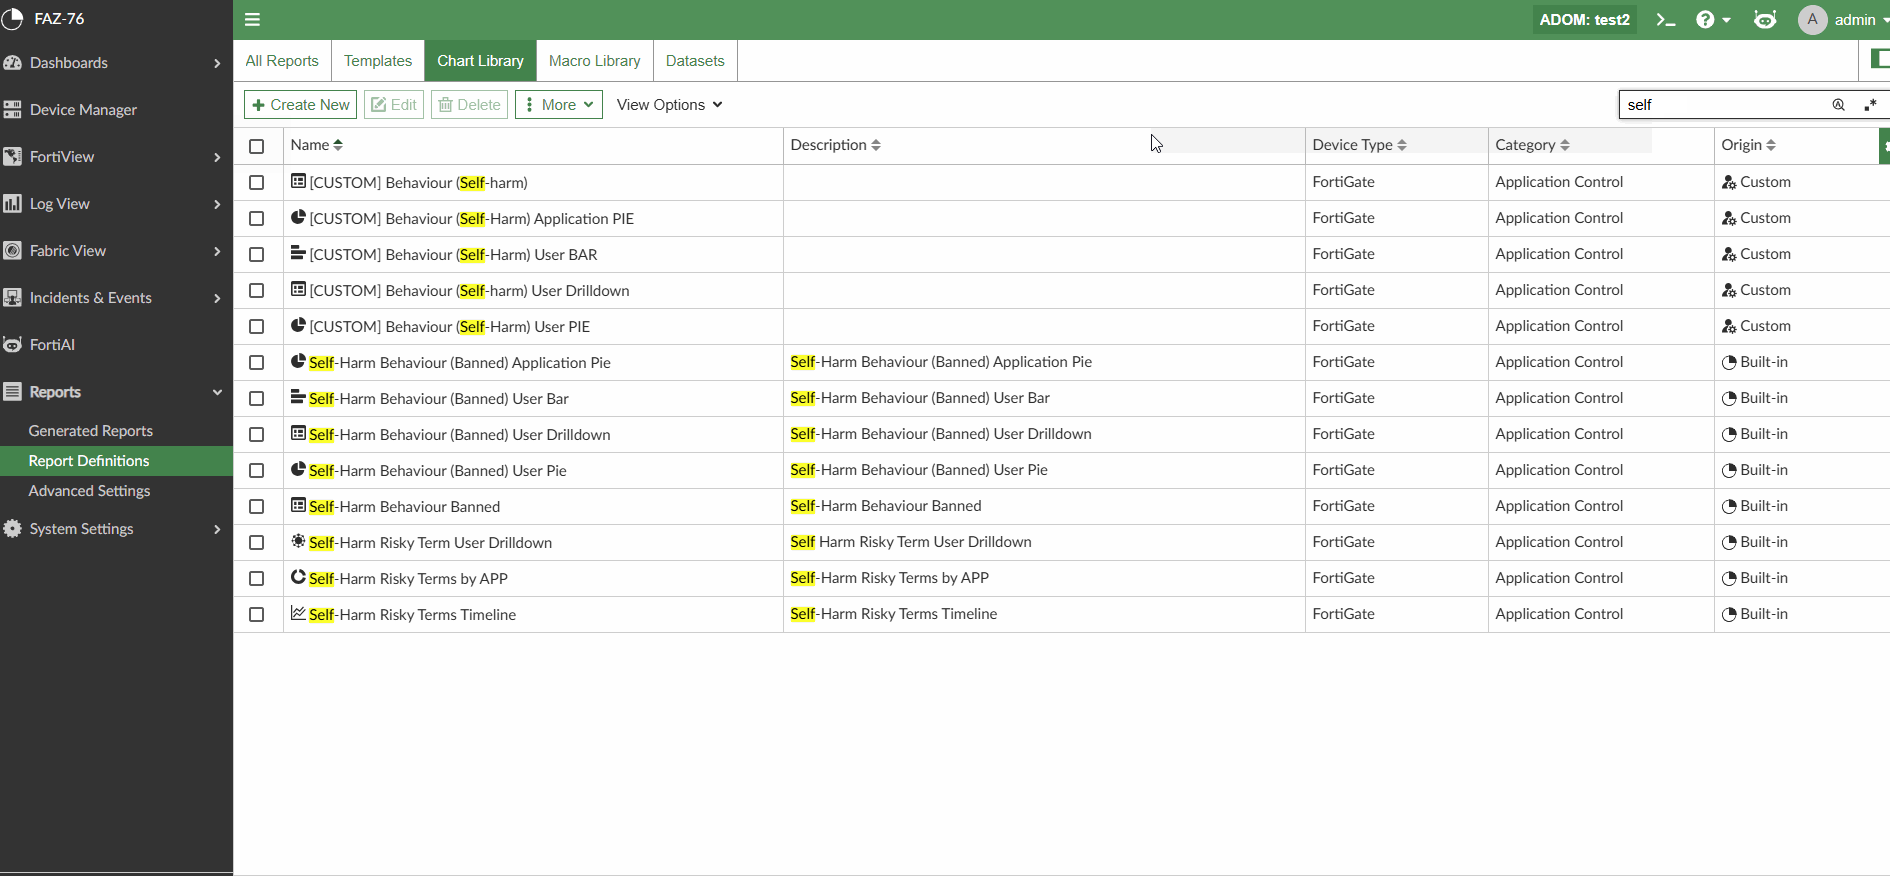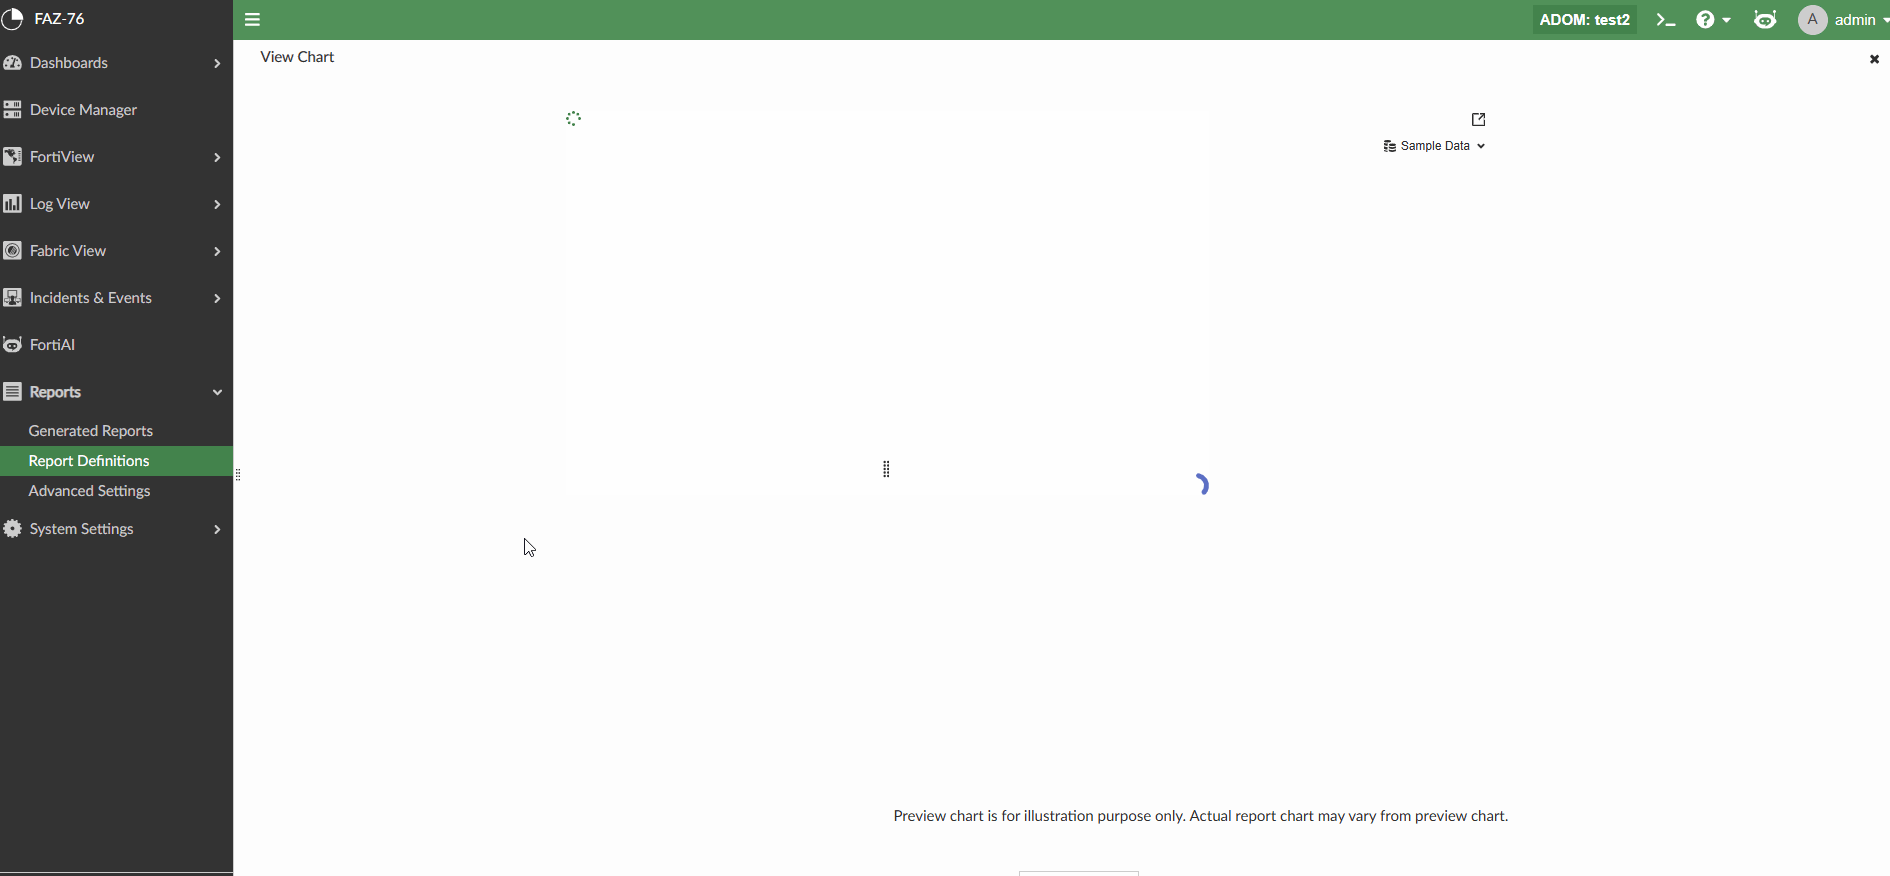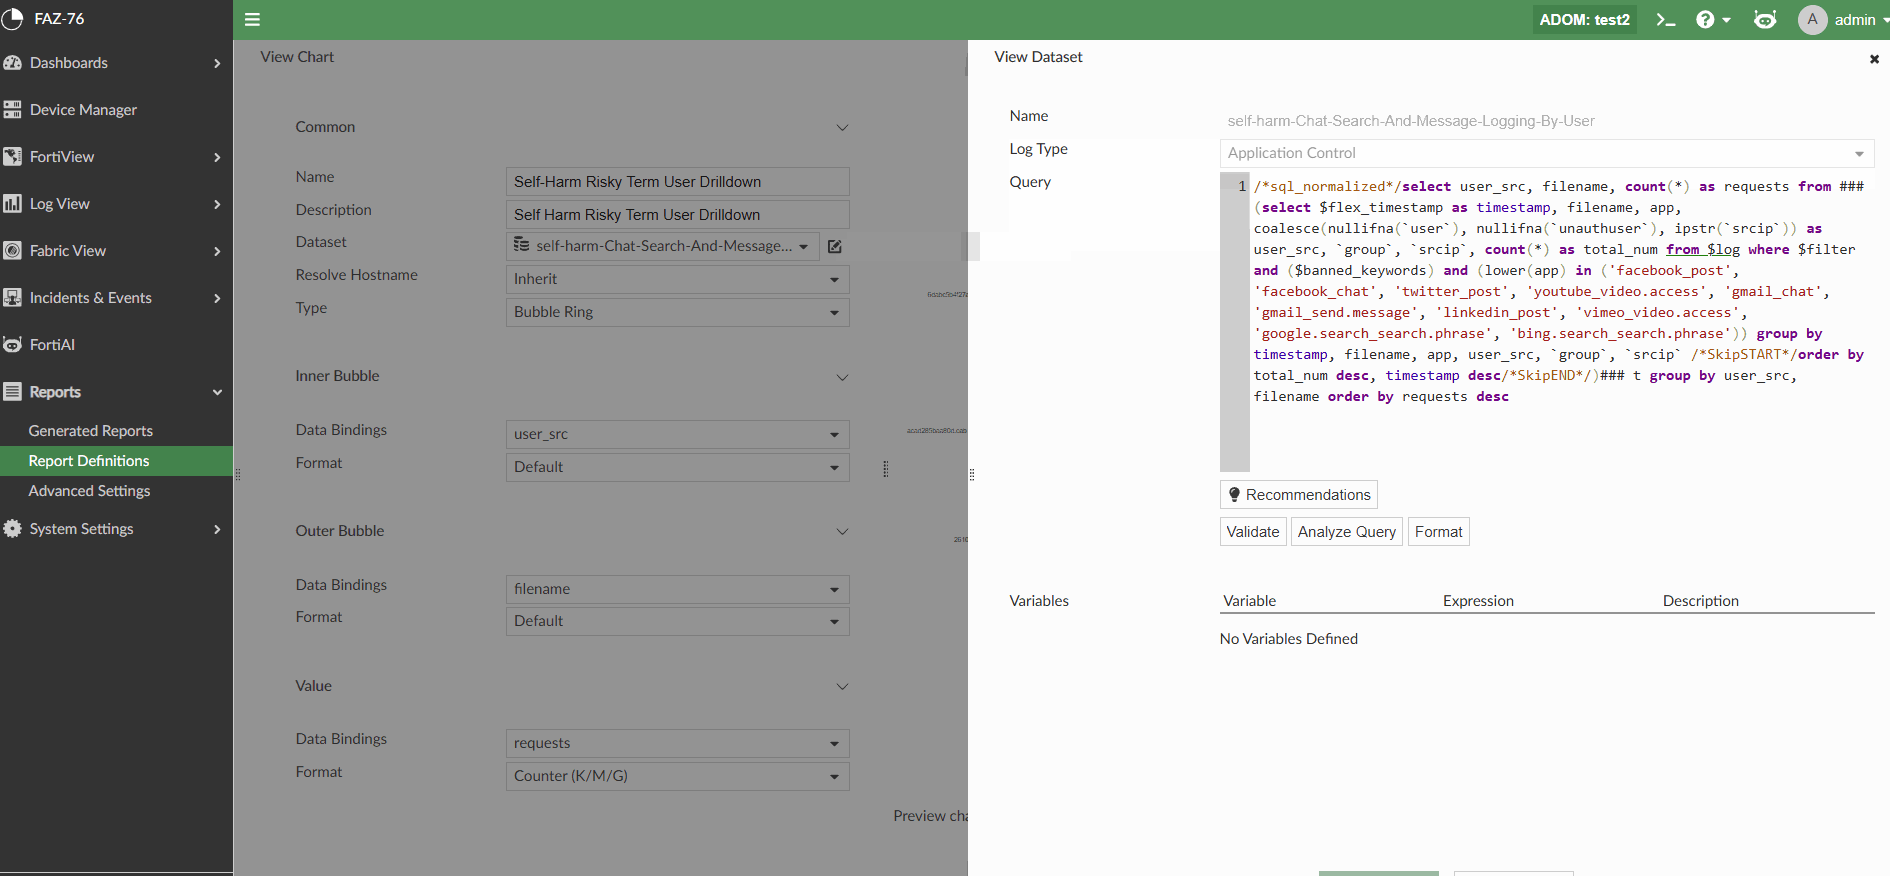
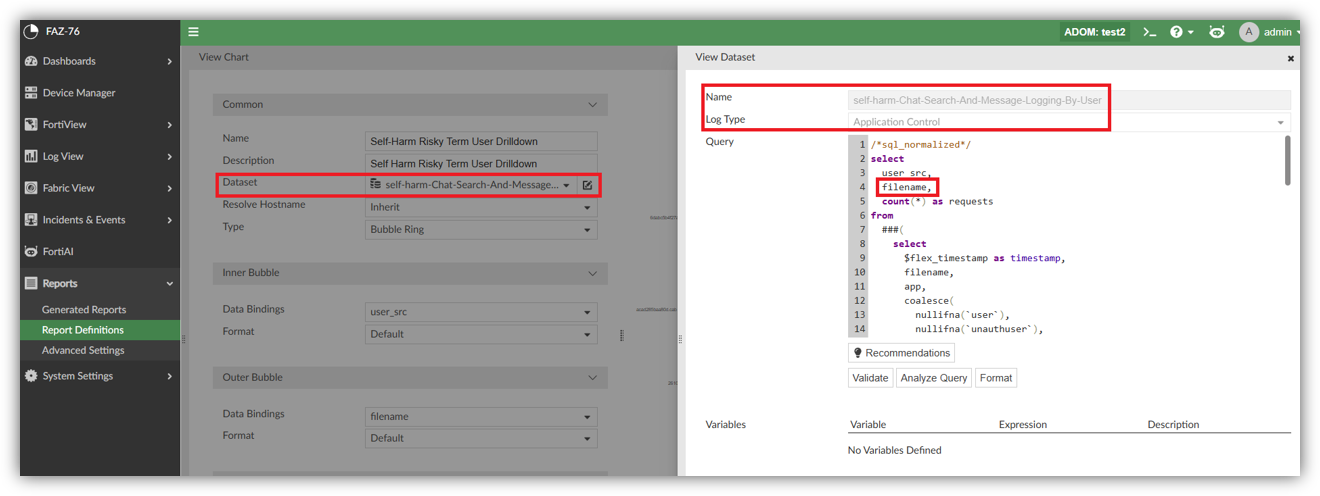
From the default dataset information shown for self-harm-Chat-Search-And-Message-Logging-By-User, the logs that it gets from the FortiGate are Application Control logs, and the column filename is used to select from the database.
The same steps to find for Cyber-Bullying Indicators Report, and it uses the user-chat-search-and-message-logging dataset.
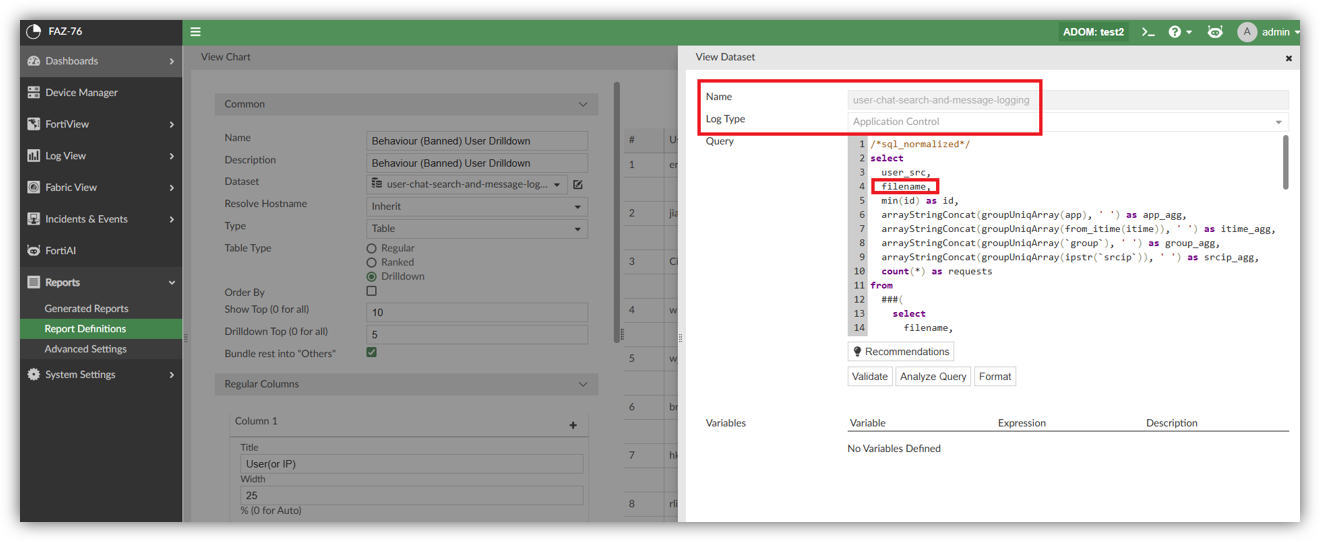
From this information, understand that logs need to be checked on the FortiGate side is Application Control logs, and specific on filename column.
Filter this information on Log View to make sure it is getting the same value, by using Text Mode filter where filename!="" , and the logs is under Log View -> Fortinet Logs -> FortiGate -> Security: Application Control.
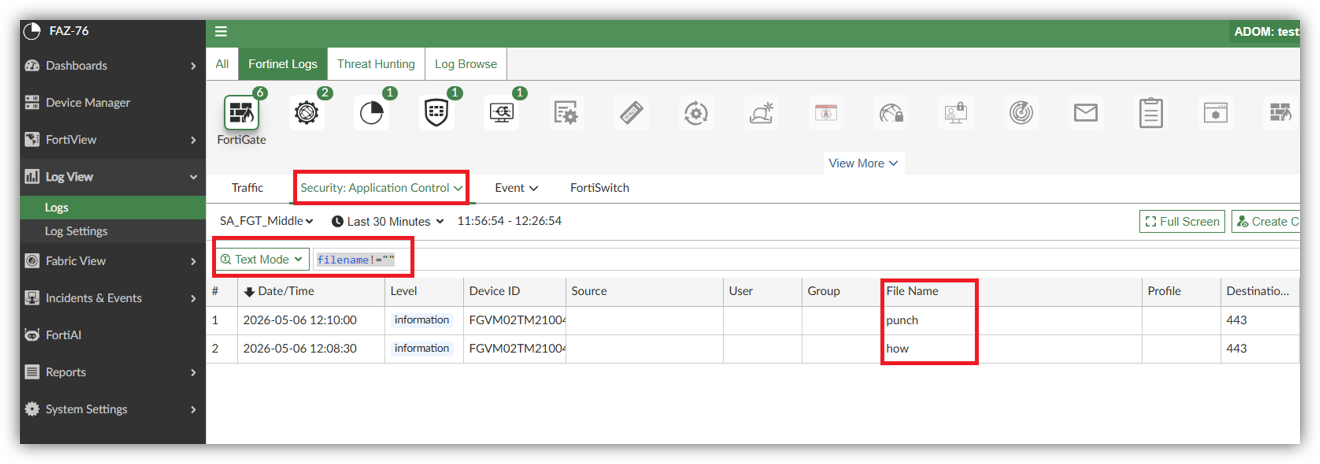
It has been concluded that the logs are coming from FortiGate, which contain the values to populate on the report are the same, and need to be checked on the FortiGate side.
On the FortiGate side, check on the 'config ips settings' if 'proxy-inline-ips' is enabled.
config ips settings
set proxy-inline-ips enable
end
Command below to confirm that HTTP/HTTPS traffic to be processed directly in WAD for Application Control and IPS UTM features.
# diagnose wad debug ips-db status
inline-ips db, version 2175001 checksum 2896234b396cfd84dfe8cb4870433bfe, compile took 43 sec
ips: 6.741 Tue Dec  1 02:30:00 2015
app: 36.214 Tue May  5 01:20:00 2026
app entries: 1862
app custom entries: 0
ips entries: 6050
ips custom entries: 0
Proceed to disable the 'proxy-inline-ips' to use an IPS and Application Control directly from the FortiGuard server instead, and check the logs command below to confirm if the 'filename' value shows the full phrase instead.
config ips settings
set proxy-inline-ips disable
end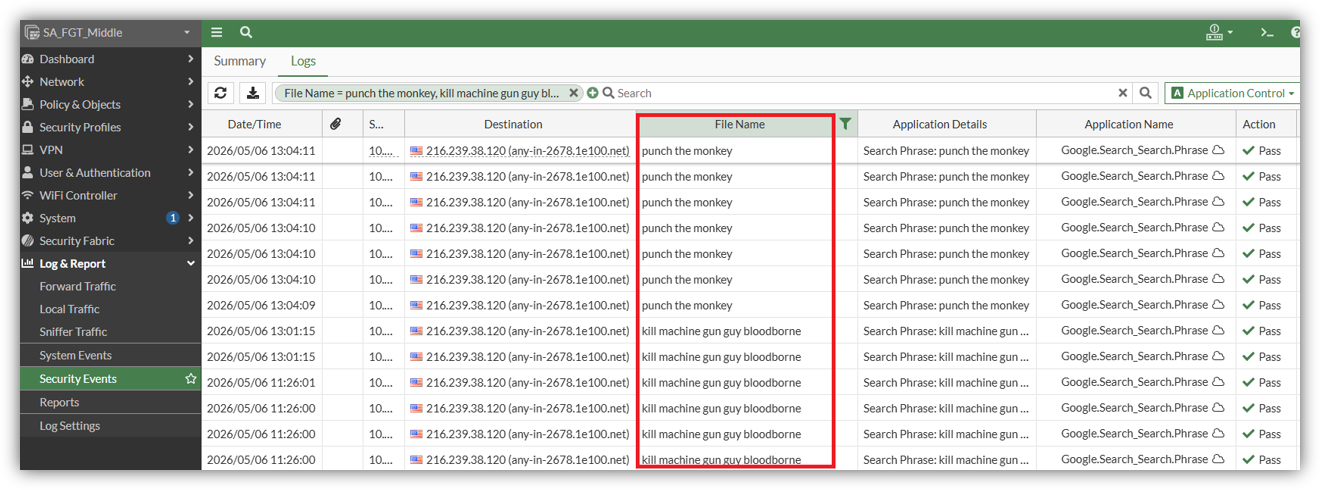
Check the same on the FortiAnalyzer Log View if the same logs are populated.
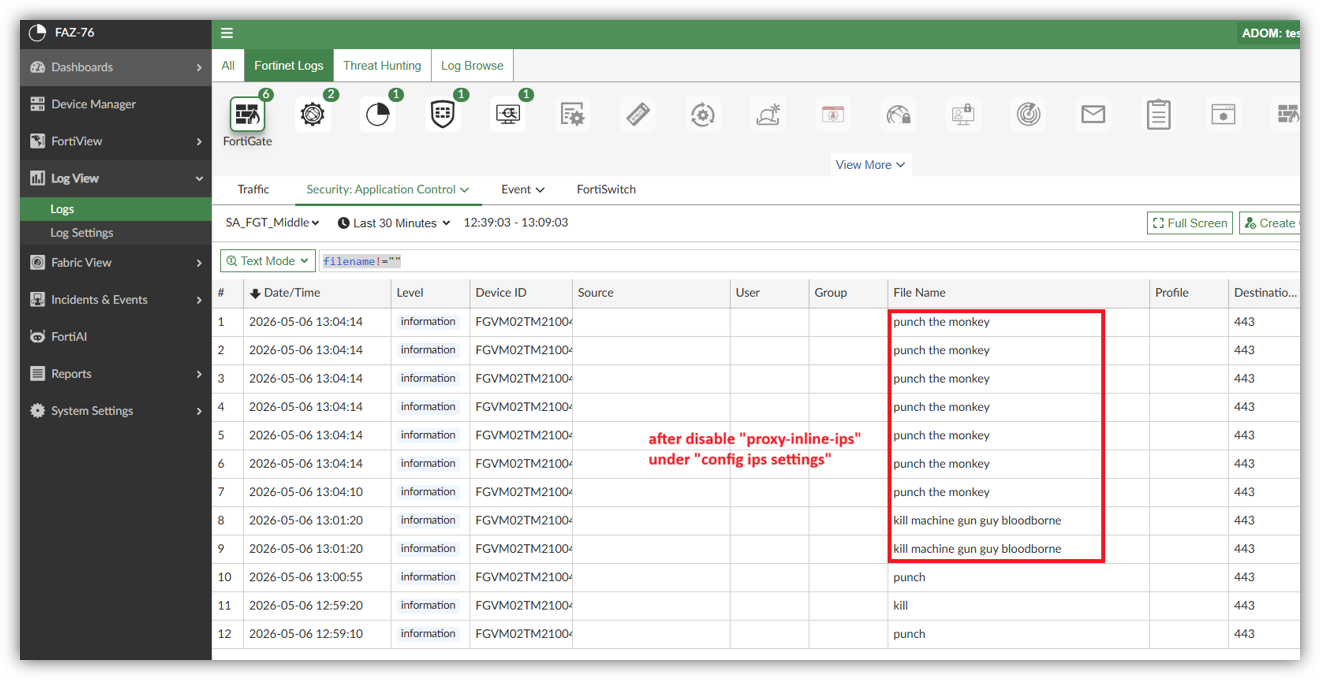
Once the expected logs are showing in the Log View, check the reports to confirm that the expected output is populated.
Related article:
Technical Tip: Proxy Inline Intrusion Prevention System feature in FortiOS

