Make sure to allow the traffic towards usfds1.fortinet.com on TCP port 443. 'For US FortiGuard region servers Only'.
Or:
Make sure to allow the traffic towards fds1.fortinet.com on TCP port 443. 'For Global FortiGuard servers'.
The traffic should not be deeply inspected because FortiGuard servers must see the FortiAnalyzer/FortiManager certificate.
Once the traffic is allowed, trigger a manual update with the following commands:
diagnose fmupdate service-restart fds
diagnose fmupdate service-restart fgd
Wait 5 minutes, then run:
diagnose fmupdate updatenow fds
diagnose fmupdate updatenow fgd
If the issue is still occurring, check the connection with FDS using the commands below and share the results with Support.
diagnose license list
diagnose fmupdate dbcontract
diagnose fmupdate view-serverlist fds
diagnose fmupdate view-service-info fds
diagnose fmupdate update-status fds
diagnose fmupdate get-device fds
diagnose fmupdate view-serverlist fgd
diagnose fmupdate view-service-info fgd
diagnose fmupdate update-status fgd
diagnose fmupdate get-device fgd
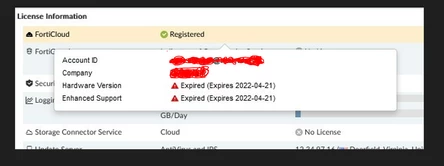
If the License is renewed and was not reflected on the device license information, check if the portal is updated with the new license information. This might happen because the previous license is still valid. In that case, the new expiry date will be reflected once the old license expires If the device has access to FortiGuard servers.
Note: If FortiAnalyzer/FortiManager are running in an air-gap network, re-applying the license file and the account entitlement will be required after the current license expired to take effect.
Related documents:
| 




