emorlang_FTNT
Staff
Staff
December 15, 2024

Technical Tip: Using FortiAnalyzer to detect activities related to the Mitel MiCollab Unauthorized Access Attack: CVE-2024-35286, CVE-2024-41713

  • December 15, 2024
  • 0 replies
  • 262 views
Description

This article describes how to use a custom event handler in FortiAnalyzer to raise alerts for incident response related to attacks that attempt to leverage the Mitel MiCollab Unauthorized Access Attack. A report is also provided to gain historical visibility into the logs.


Note that this article provides alpha files which are automatically generated. The article will be continually updated as more information becomes available.
Scope

This article contains the files necessary to load an event handler and report into the FortiAnalyzer for either a Fabric ADOM or a FortiGate ADOM. The Fabric report and event handler leverage logs from other Fortinet products that can be used to detect the attack in addition to FortiGate logs.


For more information about this attack, see the following FortiGuard Outbreak Alert:

Mitel MiCollab Unauthorized Access Attack

Solution

What is included in Fortinet_Mitel MiCollab Unauthorized Access Attack.zip:


  1. Mitel MiCollab Unauthorized Access Attack_event-handler.json: This event handler helps identify Mitel MiCollab Unauthorized Access Attacks detected by FortiGate and other Fortinet products. This event handler is configured for Fabric ADOMs.
  2. Mitel MiCollab Unauthorized Access Attack_report.dat: This report displays the findings on Mitel MiCollab Unauthorized Access Attacks from FortiGate and other Fortinet products. This report is configured for Fabric ADOMs.
  3. fgt_Mitel MiCollab Unauthorized Access Attack_event-handler.json: The event handler for FortiGate ADOMs is configured for FortiGate logs only.
  4. fgt_Mitel MiCollab Unauthorized Access Attack_report.dat: The FortiGate ADOMs report includes only FortiGate charts.

Steps:

  1. Download the Fortinet_Mitel MiCollab Unauthorized Access Attack.zip file (contains 4 files).
  2. Unzip Fortinet_Mitel MiCollab Unauthorized Access Attack.zip.
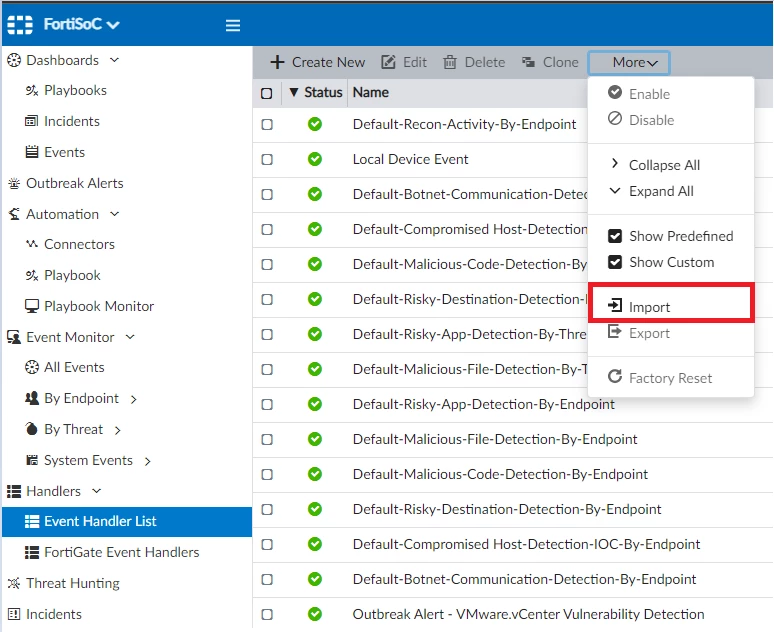
  3. Import Mitel MiCollab Unauthorized Access Attack_event-handler.json or fgt_Mitel MiCollab Unauthorized Access Attack_event-handler.json event handler:
  • Choose an ADOM (if ADOMs are enabled). The ADOM may have the Fabric or FortiGate type.
  • Choose the FortiSOC module. 
  • Select Event Handler List.
  • Select the Import option under More.
  • Select the appropriate event handler depending on the ADOM type.

event handler.png


Result:

The event handler is enabled and will be triggered if the appropriate logs are received following the import of the event handler. 

Edit the event handler to customize the notification section.


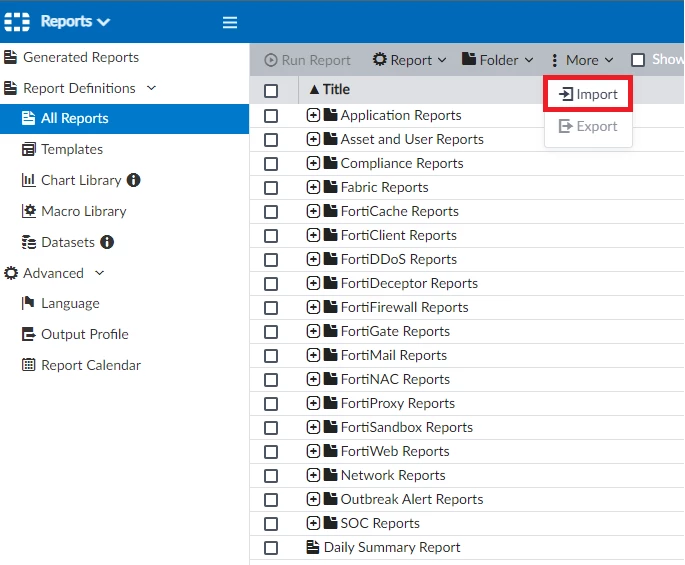
  1. Import Mitel MiCollab Unauthorized Access Attack_report.dat or fgt_Mitel MiCollab Unauthorized Access Attack_report.dat to Reports:
  • Choose an ADOM (if ADOMs are enabled). The ADOM may have the Fabric or FortiGate type.
  • Choose the Report module.
  • Select the Import option under 'More'.
  • Select the appropriate file for the ADOM type to add the report to the ADOM.

report.png


Result

The Mitel MiCollab Unauthorized Access Attack_report can be run anytime as determined by an admin user.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!