



Technical Tip: Remote admin login using RADIUS with FortiAuthenticator and admin profile selection
Description
This article describes how to create an admin profile and set up the RADIUS server on FortiAuthenticator, using RADIUS VSAs to select an adminitrator profile.
Scope
FortiAnalyzer, FortiManager, FortiAuthenticator.
Solution
FortiManager / FortiAnalyzer configuration:
RADIUS Server configuration:
Navigate to System settings -> Remote Authentication -> Create new -> select Radius server from the drop-down menu.
Name: FAC
Server IP/Name: 10.109.53.19
Server Secret: radius_secret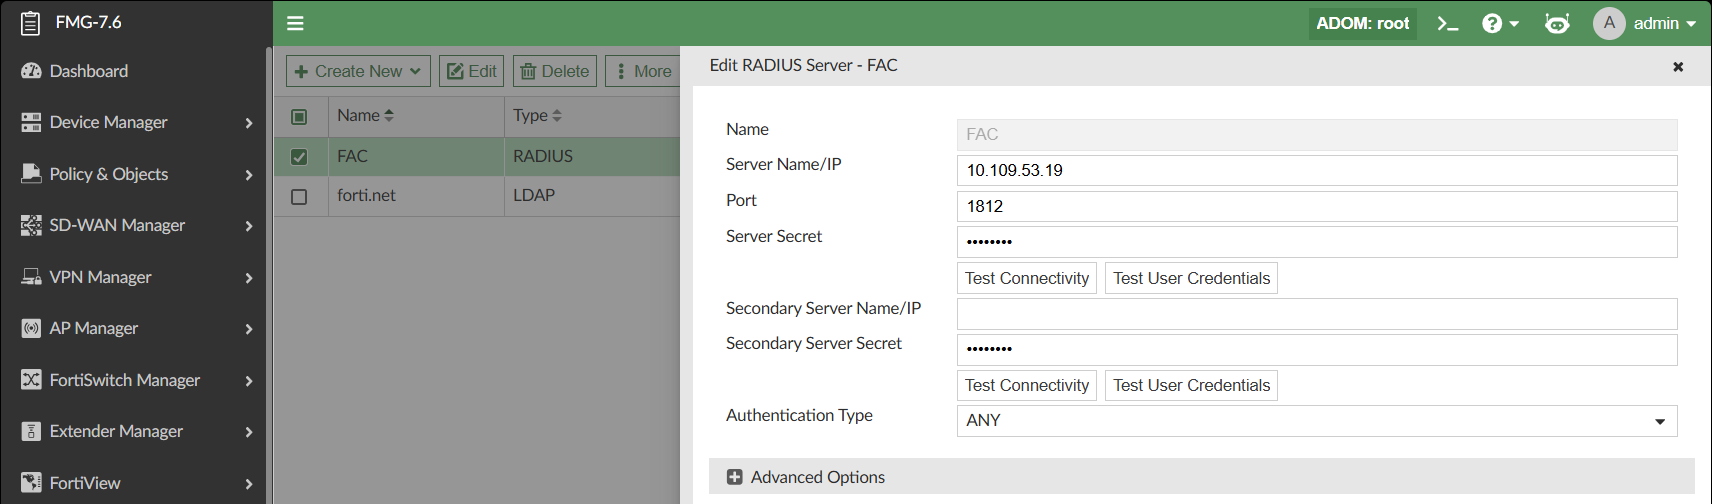
Alternatively, configure the following via the CLI:
config system admin radius
    edit "FAC"
        set server "10.109.53.19"
        set port 1812
        set secret radius_secret
    next
end
Admin user configuration:
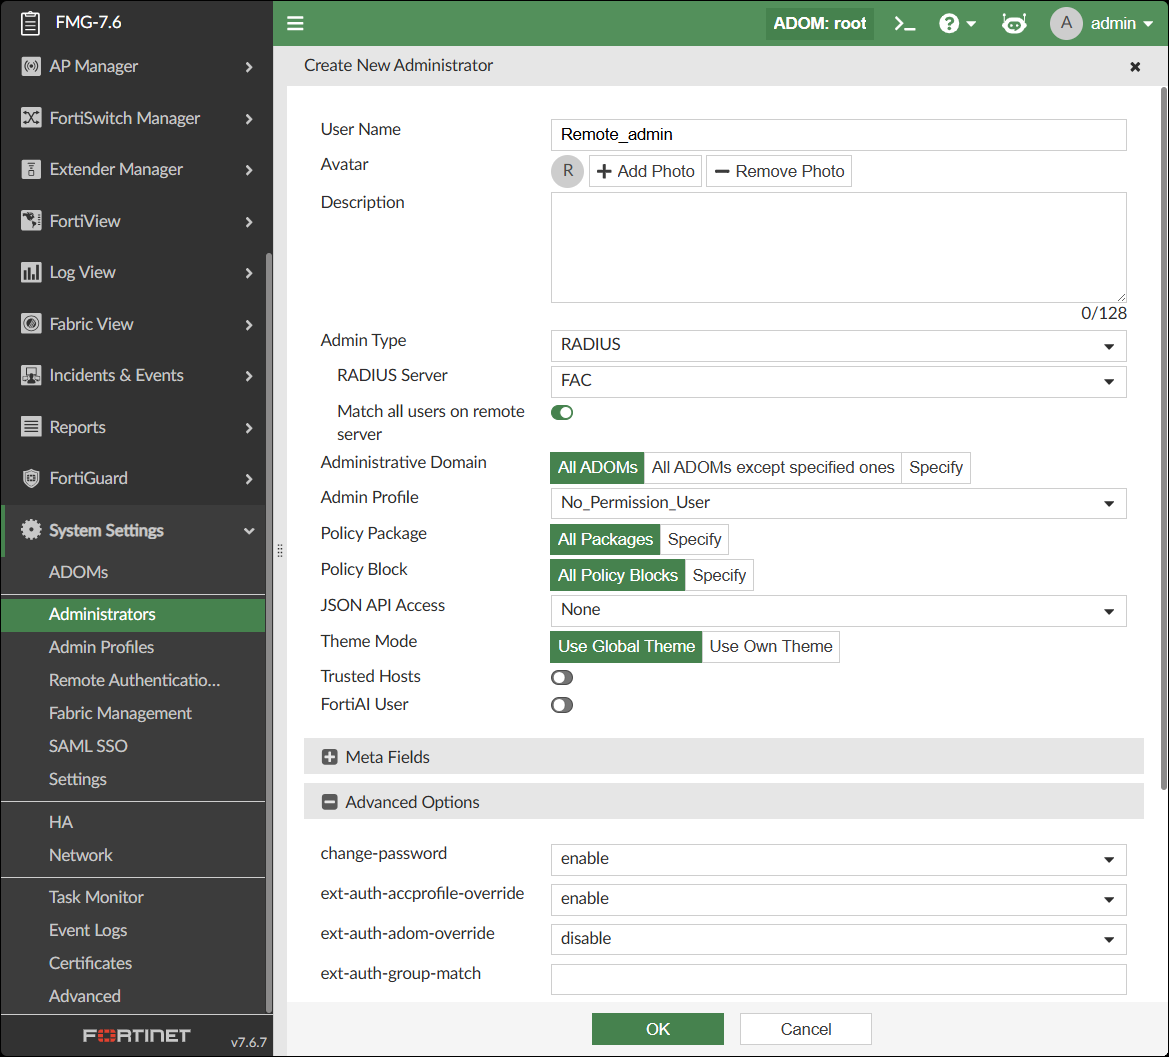
Go to System Settings -> Administrators -> Create New -> Administrator.
Under RADIUS, select the FortiAuthenticator server.
Enable Match all users on remote server.
Use the admin profile 'No_Permission_User'.
Expand Advanced Options -> Enable 'ext-auth-accprofile-override'.
Note - Match all users on the remote server:
When this option is enabled, at login, FortiManager/FortiAnalyzer will check for a matching user name (case sensitive).
If no match exists, FortiManager/FortiAnalyzer will send the entered username and password to this RADIUS server and grant access if the server responds with access_accept.
When this option is disabled, the profile will only be matched if the entered username matches. In this case, the profile would only be used if the administrator tries to log in as 'Remote_admin'.
FortiAuthenticator configuration:
RADIUS client:
Create a RADIUS client under Authentication -> RADIUS Service -> Clients by selecting 'Create New'.
Set up an entry to match the FortiManager/FortiAnalyzer configuration:
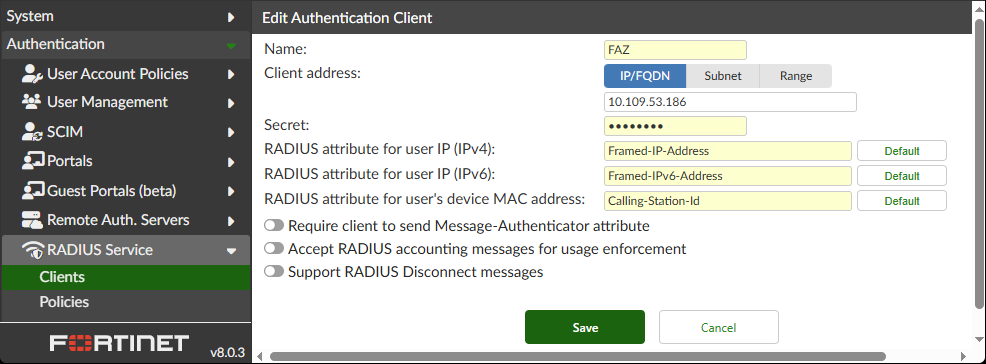
The client IP should match the FortiAnalyzer IP. FortiAuthenticator will only use this client profile when the access_request packet comes from the specified source IP.
The secret specified here must also match the one value by FortiAnalyzer for the RADIUS server to respond.
Admin Profile Attribute VSA:
To configure the FortiAuthenticator to reply to packets with the profile attribute, create a group and/or a user. The RADIUS attribute may be applied to the user or the group.
Configure the Super_User attribute on a 'Super Users' profile as follows:
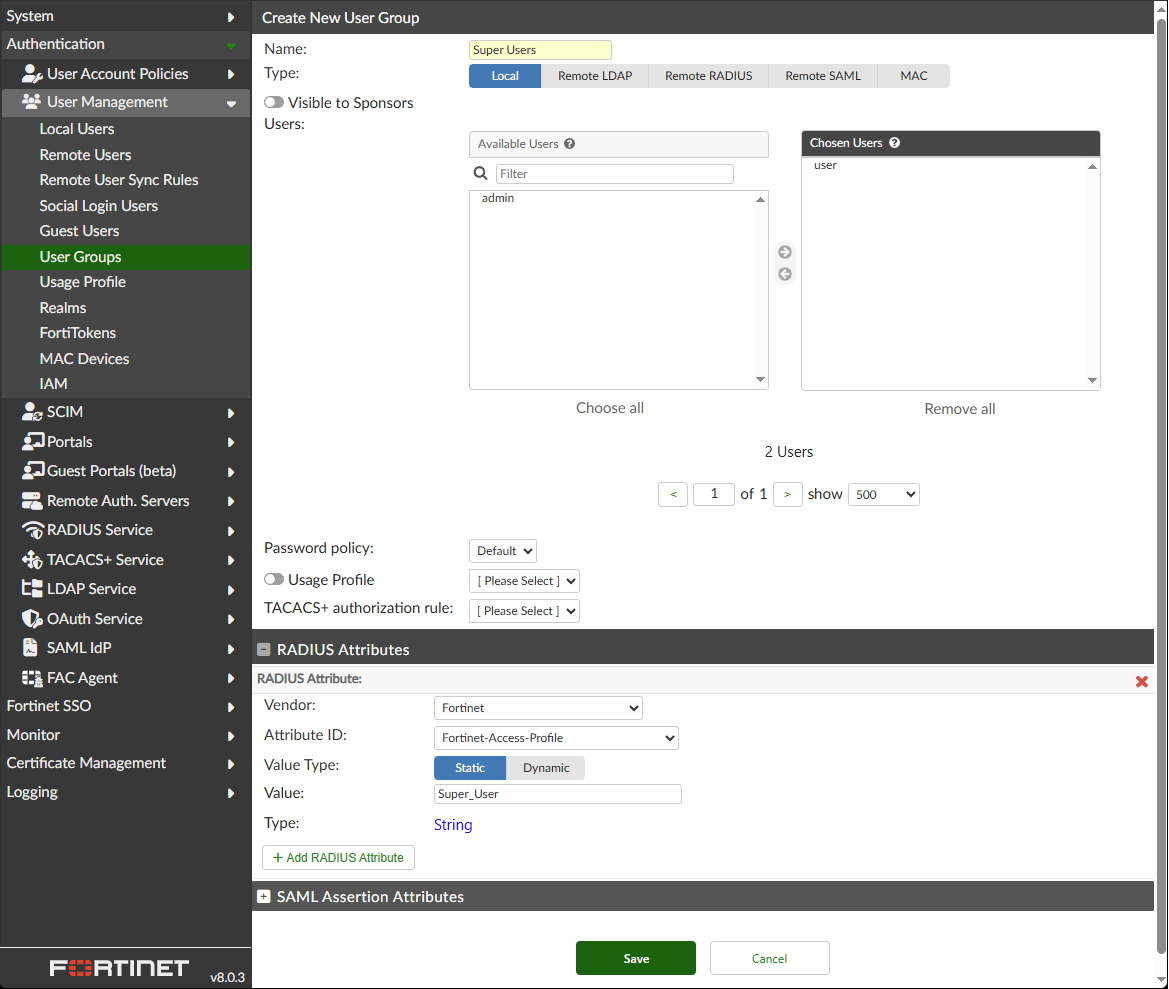
The attributes used in FortiManager/FortiAnalyzer administrator authentication are as follows:
RADIUS VSA name | FortiManager/FortiAnalyzer override setting |
|---|---|
Fortinet-Access-Profile | ext-auth-accprofile-override |
Fortinet-Vdom-Name | ext-auth-adom-override |
Fortinet-Group-Name | ext-auth-group-match |
A list of all of Fortinet's VSA is available in Technical Tip: Fortinet's RADIUS Dictionary and VSAs (latest).
RADIUS policy:
Authentication -> RADIUS Service -> Policies.
RADIUS clients: Select the appropriate client.
RADIUS attribute criteria: Skip.
Authentication type: MSCHAPv2/CHAP/PAP/EAP (Password/OTP).
RADIUS Auth (UDP/1812) must be enabled on the FortiAuthenticator interface settings.
Testing and troubleshooting:
Log in to FortiManager/FortiAnalyzer. If a private/incognito window is used, the main admin can stay logged in.
To debug an authentication attempt, use these commands:
diagnose debug application auth 255
diagnose debug enable
In this case, the server accepted:
s68100: auth request: user=user from=GUI(10.109.63.254)
s68100: wildcard admin: Remote_admin
s68100:   start radius: FAC
s68100:FAC: connecting to server 0: 10.109.53.19 ip=10.109.53.19 port=1812/udp
s68100:FAC: send request: type=pap id=12
s68100:FAC:   got reply: code=accept(2) id=12
s68100:FAC:   Message-Authenticator: len=16
s68100:FAC:   Ftnt-Profile: Super_User
s68100:FAC: success
s68100: profile from server: Super_User
s68100: wildcard admin matched: Remote_admin
s68100: profile-override: Super_User
s68100: auth result: success
If the authentication is rejected, it is possible to view detailed logs by navigating to https://<FortiAuthenticator_IP>/debug/, where <FortiAuthenticator_IP> should be replaced with the appropriate IP address.
