



Technical Tip: Logs disappeared in log view, it shows error 'CSRF verification failed. Request aborted'
Description
This article explains possible reasons for error '403 Forbidden CSRF verification failed. Request aborted.', when navigating to the Log View and FortiView pages of FortiAnalyzer.
Scope
FortiAnalyzer v7.4.4 and later.
Solution
Log View fails to show the logs and returns a 403 error as seen in the screenshot below:
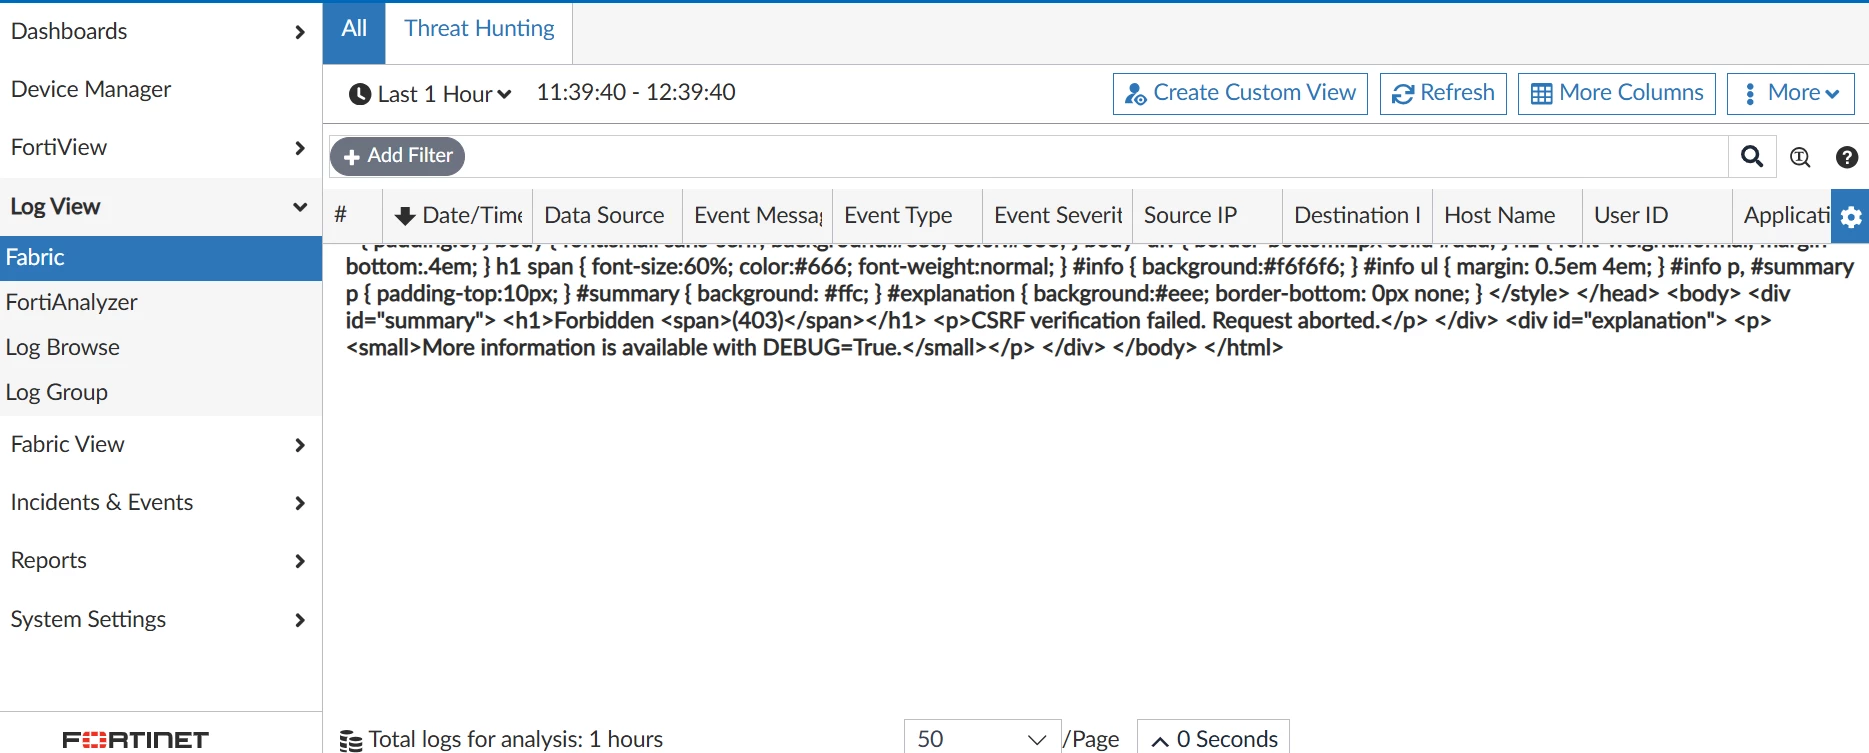
One possible reason for this error is a misconfiguration of the global admin-host setting, which was introduced from FortiAnalyzer/FortiManager v7.4.4 to provide additional protection against cross-site scripting (XSS) attacks.
Example configuration:
config system global
    set admin-host faz.example.com  <-----
end
config system interface
    edit port1
        set ip 10.11.12.13 255.255.240.0
    next
end
The admin-host value replaces the original Host header of the client request during redirection.
FortiAnalyzer validates the requested URL by comparing the address specified in the request with the expected host address. However, when admin-host is configured, FortiAnalyzer uses the admin-host value as the expected hostname instead of its own IP address.
As a result, if the address in the request does not match the configured admin-host value, the URL validation check fails and the request is rejected.So, with FortiAnalyzer configured as above, if the user accesses the FortiAnalyzer GUI by:
https://faz.example.com/ - the logs should load normally
https://10.11.12.13/ - would return 'CSRF verification failed. Request aborted.'
To allow access to FortiAnalyzer with both FQDN and IP address, the admin-host value should be unset:
config system global
    unset admin-host
end
Even with unset admin-host, the same error may also occur due to invalid characters in the FQDN. For example, a hostname containing underscore '_' may cause CSRF verification error.
The solution is to replace the underscore in the DNS record with a hyphen.
For example:
https://faz_01.example.com/ - may return error
https://faz-01.example.com/ - should work fine
Although accepted by many DNS servers, underscores are technically not permitted in standard hostnames and FQDNs. According to core Internet specifications (RFC-952 and RFC-1123), valid hostname labels can only contain letters, digits, and hyphens.


