Technical Tip: FortiAnalyzer expected behavior with FortiGate HA
| Description | This article describes what the FortiAnalyzer's expected behavior is with FortiGate HA. |
| Scope | FortiAnalyzer. |
| Solution | The following is the scenario:
There is a FortiGate HA connected to FortiAnalyzer.
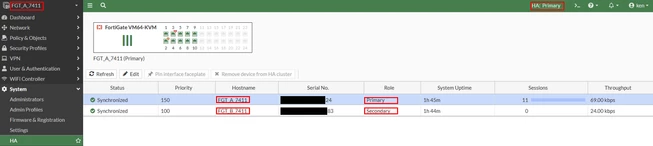
Before FortiGate HA failover: FGT_A (Primary role), Serial Number ended with ...24. FGT_B (Secondary role), Serial Number ended with ...83.
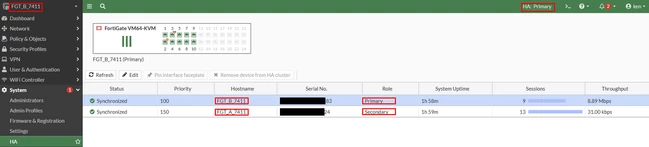
After FortiGate HA failover: FGT_B (Primary role), Serial Number ended with ...83. FGT_A (Secondary role), Serial Number ended with ...24.
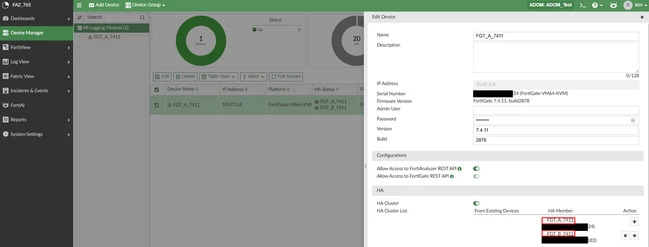
At FortiAnalyzer's Device Manager, it does not have FortiGate HA role information. When FortiGate performs any failover action, FortiAnalyzer will only show FortiGate Name and FortiGate Serial Number.
Notes: If both FortiGate (Primary and Secondary) HA can connect to FortiAnalyzer, then FortiAnalyzer will be able to receive logs from both FortiGate (Primary and Secondary) HA.
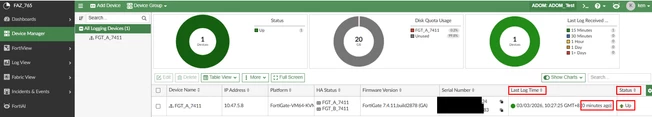
At FortiAnalyzer, go to Device Manager -> Last Log Time status shows (0 minutes ago), it mean FortiAnalyzer continuously receives logs from FortiGate.
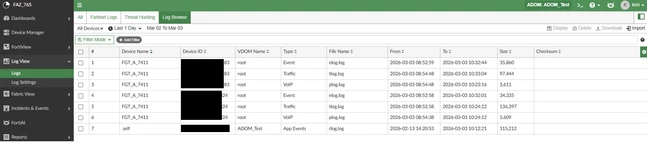
At FortiAnalyzer, go to Log View -> Logs -> Log Browse -> It is possible to show both FortiGate (Primary and Secondary) HA's Serial Number.
|