


Technical Tip: FortiAnalyzer compromises host showing detect method as infected-domain
Description
This article describes why FortiAnalyzer Compromises host shows the Detect Method as Infected-domain.
Scope
FortiAnalyzer.
Solution
IOC Uses Threat info database.
Here is how IOC works:
As the WF logs come in, the breach detection engine parses the logs and categorizes the 'normal looking' web traffic into two main categories (based on the information from the TDS package):
Infected: real breach.
'A match or matches of the blacklisted IPs/DGA domains, etc. have been found from the web logs'.
The whole idea of IOC is identifying potential threat domains that are not identified by the FortiGate web filtering service. The
IOC engine monitors each URL/IP this host has visited over a period of time and continuously analyzes the behavior pattern using its internal algorithm to determine if the host is compromised.
The IOC requires a separate threat detection license.
Difference between demo and paid version, and potentially the reason for the 'verdict', potentially giving 'outdated' results.
The demo mode IOC uses the default threat package, which comes with the firmware release.
The default package is not up-to-date.
The licensed IOC uses a fresh threat package (daily downloaded) from FortiGuard, and it produces highly accurate detection.
To check the IOC license and the IOC database version (TIDB version), run the command below on FortiAnalyzer CLI. This will also list down the TIDB DB load time and further details about the number of infected domains/URL/IP.
diagnose test application sqllogd 204 stats
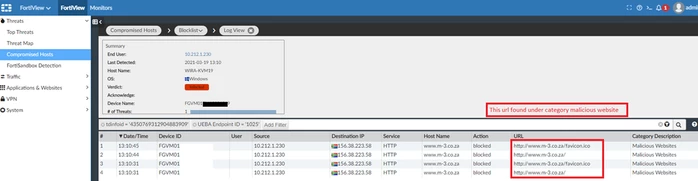
How to check domain is infected as per the TIDB database:
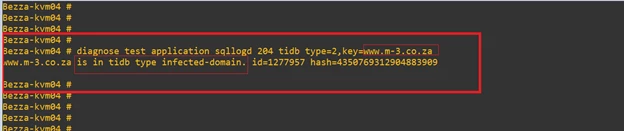
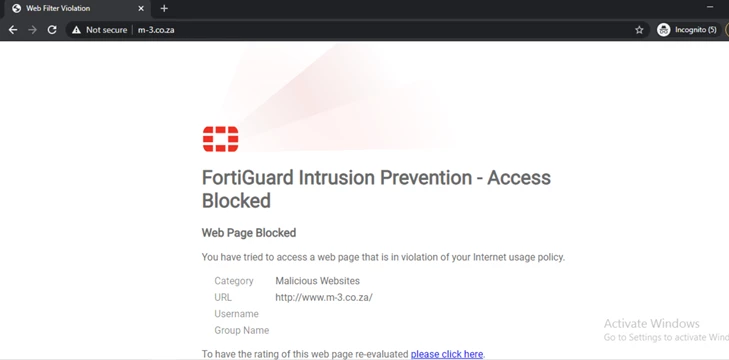
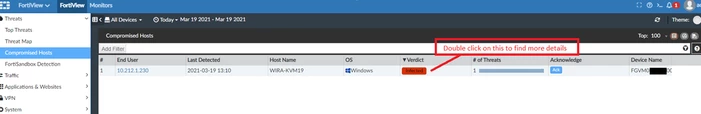
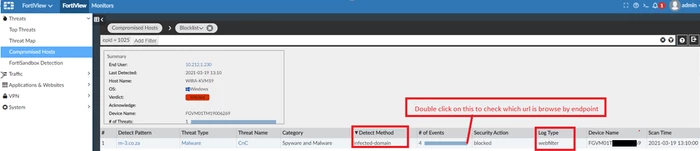
Example: Endpoint(LAN USER) tries to access URL www.m-3.co.za.
Related documents:


