Sending FortiGate logs to a remote FortiAnalyzer
Article
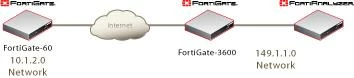
| Description | This article describes how to configure a remote FortiGate unit to send log packets to a FortiAnalyzer unit behind an office FortiGate unit using a VPN tunnel.
In this scenario, any computer on the 10.1.2.0 network can ping the FortiAnalyzer unit. However, the logs generated by the FortiGate-60 have a source IP address of the external interface (192.168.1.1), which is not allowed to traverse through the tunnel and reach the 149.1.1.0 network (the office FortiGate-3600). A VPN tunnel is already configured between the FortiGate-60 and the FortiGate-3600 to successfully communicate between the 10.1.2.0 network and the 149.1.1.0 network. |
| Components |
|
| Steps or Commands | Note: NAT-Traversal Tunnel mode between FortiOS v2.80 and FortiAnalyzer v3.0 is not supported. Tunnel mode is supported between FortiOS v3.0 and FortiAnalyzer v3.0.
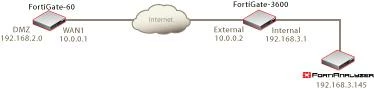
IPSec interface mode (new in FortiOS 3.0) enables the communication between devices as long as IP addresses are assigned to the IPSec device at each end, and the FortiAnalyzer unit has a route for that IP address. For example consider the following:
For this example, the IPsec tunnel the IP address pair is 10.100.100.1 and 10.100.100.2. The following setup uses the following CLI commands. FortiGate-60 Configurationconfig system interface edit "wan1" set vdom "root" set ip 10.0.0.1 255.255.255.0 set allowaccess ping set type physical next end config vpn ipsec phase1-interface edit "peer" set interface "wan1" set dpd enable set proposal 3des-md5 3des-sha1 set remote-gw 10.0.0.2 set psksecret ENC yCHLVEsi2Q7eu/yXyZA9Mqr5I next end config vpn ipsec phase2-interface edit "p2" set phase1name "peer" set proposal 3des-md5 3des-sha1 set replay enable next end config system fortianalyzer set status enable set server 192.168.3.145 end config system interface edit "peer" set vdom "root" set ip 10.100.100.1 255.255.255.255 set type tunnel set remote-ip 10.100.100.2 set interface "wan1" next end config router static edit 1 set device "peer" set dst 192.168.3.0 255.255.255.0 next end config firewall policy edit 1 set srcintf "dmz" set dstintf "peer" set srcaddr "all" set dstaddr "all" set action accept set schedule "always" set service "ANY" next end Configuring the FortiGate-3600config system interface edit "external" set vdom "root" set ip 10.0.0.2 255.255.255.0 set allowaccess ping set type physical next end config system interface edit "external" set vdom "root" set ip 192.168.3.0 255.255.255.0 set allowaccess ping set type physical next end config vpn ipsec phase1-interface edit "peer" set interface "external" set dpd enable set proposal 3des-md5 3des-sha1 set remote-gw 10.0.0.1 set psksecret ENC 3HeoZa62F/5A8b2p/m9r3uvnE9Mqr5I next end config vpn ipsec phase2-interface edit "p2" set phase1name "peer" set proposal 3des-md5 3des-sha1 set replay enable next end config system interface edit "peer" set vdom "root" set ip 10.100.100.2 255.255.255.255 set type tunnel set remote-ip 10.100.100.1 set interface "external" next end config router static edit 1 set device "peer" set dst 192.168.2.0 255.255.255.0 next end config firewall policy edit 1 set srcintf "peer" set dstintf "internal" set srcaddr "all" set dstaddr "all" set action accept set schedule "always" set service "ANY" next edit 2 set srcintf "internal" set dstintf "peer" set srcaddr "all" set dstaddr "all" set action accept set schedule "always" set service "ANY" next end If the FortiGate-3600 is the default gateway for the FortiAnalyzer unit or RIP/OSPF is running, then no configuration on the FortiAnalyzer unit is required. If not then FortiAnalyzer requires a static route for 10.100.100.1. Note: A similar configuration using a syslog server is also available in the Knowledge Base article Sending Syslogs from a FortiGate over a IPSec tunnel - A configuration example. |