



How to use FortiAnalyzer to detect a “Sunburst”/SolarWinds Hack
Description
Scope
Solution
This article describes how to use a custom Event Handler and Report in FortiAnalyzer to detect activity that may be related to "Sunburst" backdoor software in a compromised SolarWind’s Orion IT monitoring and management software update system.
For more information on this hack, see the Fortinet blog post:
What We Have Learned So Far about the “Sunburst”/SolarWinds Hack | FortiGuard labsWhat is included in Solarwinds.zip:
1. SolarWinds Normalized Report
A historical report to show CnC connections per updated list of file hashes, CnC IPs and domains released by FortiGuard for supply chain attack on SolarWinds.
2. Fortinet_SOC-Compromised_Host_Detection_SolarWinds
An event handler to trigger compromised host detections based on filters configured for signatures seen in AV and IPS logs, and also file hashes, IPs, URLs and domains seen in traffic, web filter and DNS logs.
See the Solution section for instruction on how to load these into a FortiAnalyzer unit.
Scope
The custom report provided must be imported into a Fabric ADOM in a FortiAnalyzer running FortiAnalyzer 6.4.4
The custom Event Handler provided can be used in FortiAnalyzer 6.2 and FortiAnalyzer 6.4.
Solution
All screenshots provided below for illustration purposes are taken from FortiAnalyzer 6.4.4.
1. download the Solarwinds.zip file (contains 2 files)
2. unzip Solarwinds.zip
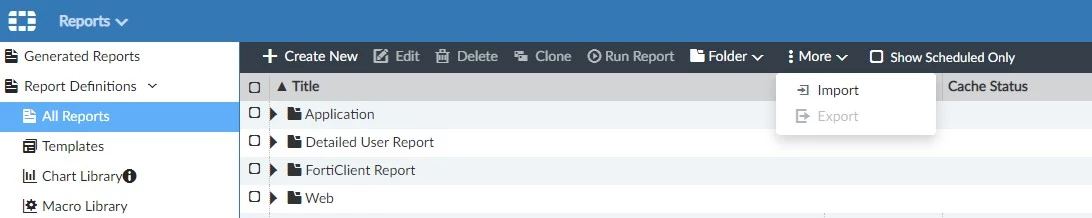
3. Use the SolarWinds Normalized Report.dat to import into Reports
a. choose a Fabric ADOM (if ADOMs are enabled)b. choose the Report modulec. select the Import option under "More"d. select SolarWinds Normalized Report.dat
Result: "SolarWinds Normalized Report" is now a report that can be run at a time determined by an admin user.
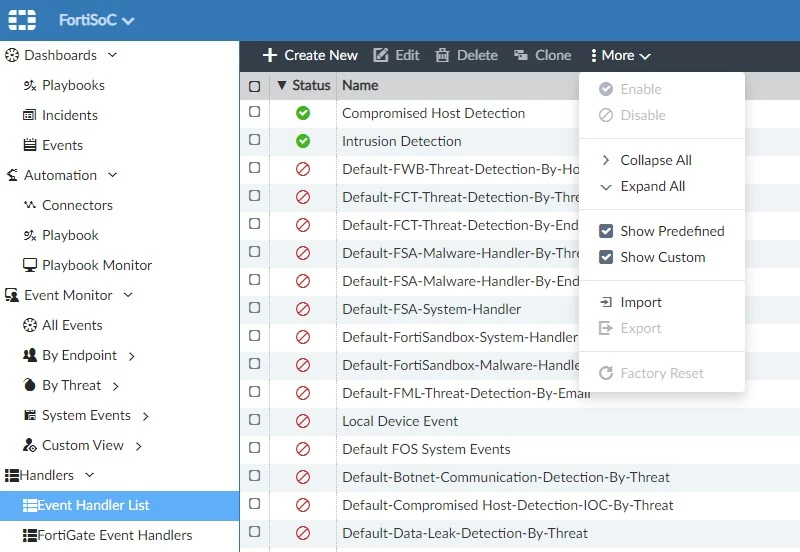
4. Use Fortinet_SOC-Compromised_Host_Detection_SolarWinds.json to import into Event Handlers
a. choose an ADOM (if ADOMs are enabled)b. chose the FortiSOC modulec. select Event Handler Listd. select the Import option under "More"e. select Fortinet_SOC-Compromised_Host_Detection_SolarWinds.json
Result: Fortinet_SOC-Compromised_Host_Detection_SolarWinds is enabled and will be triggered if the appropriate logs are received after the event handler was imported
Related Articles
Technical Tip: How to use FortiSIEM to detect a “Sunburst”/SolarWinds Hack

