Technical Tip: Allow FortiADC to Fortinet Distribution Network(FDN) services
| Description | This article describes the requirement to allow FortiADC connection to the Fortinet Distribution Network (FDN). |
| Scope | FortiADC and FortiADC VM. |
| Solution | FortiADC periodically connects to FDN services for its FortiGuard service license verification and signature database/engine updates.
When FortiADC is deployed behind a firewall or security system, the connection to FDN services may be blocked, preventing FortiADC from validating its license and components.
FortiADC requires at least a DNS and HTTPS connection to the below domains:
update.fortiguard.net
Perform the below actions once FDN domains are allowed in the firewall policy or security devices.
From GUI:
Or:
From CLI:
execute ping service.fortiguard.com execute ping update.fortiguard.com execute update-now
Debugs:
diagnose debug reset
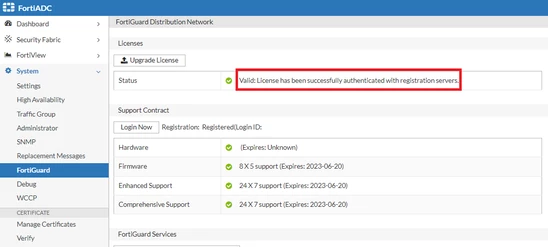
Steps to verify:
From GUI:
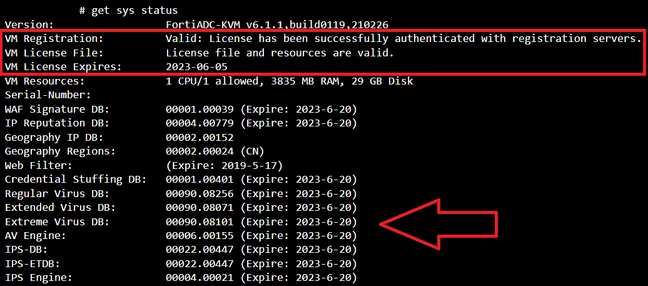
From CLI:
get system status
Related document: |